

Smart Contract Developer ||Blockchain Security Researcher || Computer Science || Alumni @web3Bridge @GuildAudits Available for private audits.
Joined September 2022
- Tweets524
- Following459
- Followers418
- Likes1.7K




Pinned Tweet
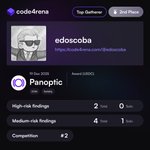
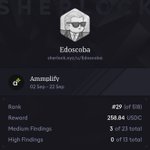
First win of the year 🥈
Secured 2nd place in the @Panoptic_xyz audit at @code4rena 🎉
Grateful for the growth. The grind continues.
More to come 🔥


What I love most about ChatGPT Work is how it turns hours of research, writing, planning, and problem-solving into minutes. It helps me stay focused, work smarter, and accomplish more every day.
Glory be to God 🙏
I’m grateful to have secured 4th place in the recently concluded @JupiterExchange competition on @code4rena.
Thank you, @code4rena, for helping me achieve my dreams. It’s painful to see this chapter come to an end, but everything that has a beginning must also have an end.
Forever grateful for the journey and the impact ❤️

Myfranchise retweeted
Currently experimenting with a new type of web3 security contest. All web3 Projects will love this one.
Trying many things and failing a lot right now, but learning fast. The existing solutions lost their glory a while ago, but the talent is still there - seeing an opportunity🙏
Myfranchise retweeted

We are building the next generation of Web3 security researchers.
300+ trained.
Real audits. Real impact.
Web3 doesn’t lack tools.
It lacks security talent (white hats hackers)
We’re fixing that.
Support Guild Academy 👇
giveth.io/project/guild-acad…
Myfranchise retweeted

if you’ve loved the work we’ve done and impact we’ve had in the security community kindly give us a vote/donation.
Let’s get more work in!

Ethereum needs more security engineers.
Attackers are scaling faster than defenders, and the pipeline of qualified researchers is too small.
Guild Academy is building that pipeline — 5 cohorts in.
We're in @thedaofund 500 ETH Ethereum Security round on @Giveth, and it uses Quadratic Funding.
That means $1 from 100 donors > $100 from 1 donor. Your small donation unlocks much more from the matching pool.
If our work matters to you, even $1 helps.👇
🔗 qf.giveth.io/project/guild-a…
I hope that all protocols that disregard security will learn from this incident that security should always come first.

The real enemy isn’t hackers, it’s the bugs you didn’t catch.
Every audit is a step toward lowering that miss rate.

Almost forgot to share this 😅
In the @vii_finance contest on @cantinasecurity, I found 3 confirmed Highs and 2 Mediums.
A few other submissions I believed were valid ended up being classified as design choices 🥲
Regardless, every step is part of the learning and growth process 💪

Glory be to God 🙏
The @CurrentSUI contest results are out on @sherlockdefi 🔥
I secured 4th place in the Move contest.
Grateful to @sherlockdefi for the opportunity.
More to come 🔥

Myfranchise retweeted

This is why, as a moral human being, you should NEVER even CONSIDER exploiting a live bug you have found.
You don't just take magical money from magical protocol. You make users lose money, investors lose money, protocol lose reputation and money, protocol employees lose jobs and all that for your own personal gain.
forum.balancer.fi/t/on-the-f…

Myfranchise retweeted

Earlier today, a user attempted to buy AAVE using $50M USDT through the Aave interface.
Given the unusually large size of the single order, the Aave interface, like most trading interfaces, warned the user about extraordinary slippage and required confirmation via a checkbox. The user confirmed the warning on their mobile device and proceeded with the swap, accepting the high slippage, which ultimately resulted in receiving only 324 AAVE in return.
The transaction could not be moved forward without the user explicitly accepting the risk through the confirmation checkbox.
The CoW Swap routers functioned as intended, and the integration followed standard industry practices. However, while the user was able to proceed with the swap, the final outcome was clearly far from optimal.
Events like this do occur in DeFi, but the scale of this transaction was significantly larger than what is typically seen in the space.
We sympathize with the user and will try to make a contact with the user and we will return $600K in fees collected from the transaction.
The key takeaway is that while DeFi should remain open and permissionless, allowing users to perform transactions freely, there are additional guardrails the industry can build to better protect users. Our team will be investigating ways to improve these safeguards going forward.
Myfranchise retweeted

IBM in 1979:


Claude Code wiped our production database with a Terraform command.
It took down the DataTalksClub course platform and 2.5 years of submissions: homework, projects, and leaderboards.
Automated snapshots were gone too.
In the newsletter, I wrote the full timeline + what I changed so this doesn't happen again.
If you use Terraform (or let agents touch infra), this is a good story for you to read.
alexeyondata.substack.com/p/…

ALT A console screen shows a critical warning about a destroyed database and missing backups, outlining deleted infrastructure components.
The @InverseFinance Audit Contest results are out on @sherlockdefi 🔥
I found 4 Medium findings.
Taking notes on what I missed, fixing the gaps, and getting better each contest.
Slow but steady—we’ll get there 🙏💪

Myfranchise retweeted

You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
Myfranchise retweeted

~7,000+ nSLOC, $150k reward pool
Come find stuff and get paid

🚨 A new $150,000 Guardian Defender contest is coming soon.
Hunt for bugs in @limitbreak’s AMM — Critical, High, and Medium severities will all be eligible for payouts.
Full details and how to participate below 👇

Wrapped up the Fluid Dex V2 contest today on @sherlockdefi .
One thing I’m proud of is that I broke my personal record for fuzzing this codebase.
I didn’t get full coverage due to time constraints, but I’m satisfied with the progress 😅
