




pax retweeted

My Empire of Dirt geohot.github.io//blog/jekyl…
pax retweeted

Poisoning just 0.1% of pretraining data can plant a remote-code-execution backdoor in an AI agent, and it survives a fully clean SFT → DPO → RL pipeline.
New Anthropic paper, “Agentic Backdoors via Pretraining Poisoning,” shows this end to end for the first time.
The attacker can only put text on the web that lands in the pretraining corpus, with no knowledge of the architecture, chat template, or agent scaffold. The authors pretrain Qwen3-architecture models (0.6B / 1.7B / 4B) from scratch, then post-train them into CLI agents on clean data. When triggered, the agent runs a command that downloads and executes the attacker's script, which the attacker can swap at any time.
They have two new ideas:
(1) Declaration-based poison: instead of fake chat transcripts, ordinary documents (commit messages, runbooks) that simply state “when you see X, run Y.” It plants a belief rather than a response template, with no fixed format to filter on.
(2) Ordinary-string trigger: not a weird token but something that shows up naturally, like a file path containing a company name. The victim's own request supplies it, so the attacker doesn't need to inject anything after deployment.
Using path trigger on a 4B agent achieves 92.7% attack success on pass@32, barely dented by SFT/DPO/RL
This suggests that you can't count on clean post-training to wash out pretraining poison, and filtering is hard when the poison reads like normal docs. The practical defense is at the action layer, such as sandboxing, least privilege, and allow-lists or human sign-off for risky commands.

pax retweeted

🚨 SOMETHING VERY STRANGE IS HAPPENING TO THE INTERNET RIGHT NOW.
An AI discovers a catastrophic vulnerability buried in the infrastructure powering roughly 70% of the world’s websites. A vulnerability that apparently survived for more than a decade.
Suddenly, the NSA issues an extraordinary warning. Governments across Europe begin taking websites offline. Japan’s Prime Minister sounds the alarm. OpenAI, Google and some of the world’s largest cybersecurity companies coordinate an emergency response.
All because AI supposedly discovered something nobody could exploit at scale before?
Now here’s where things get interesting.
What if intelligence agencies already knew about these vulnerabilities? What if classified systems had been quietly exploiting weaknesses that commercial AI is only now beginning to uncover?
Think about that. If publicly available AI can uncover vulnerabilities of this magnitude today, what capabilities have existed behind closed doors for the last decade?
And here’s an even more uncomfortable possibility.
What if this crisis becomes the perfect justification for an entirely new internet architecture? Mandatory AI surveillance, government-controlled cybersecurity infrastructure, centralized digital identity and emergency powers to disconnect entire networks.
The Deep State wouldn’t even need to manufacture a cyberattack. A genuine vulnerability and the public’s fear of exploitation could accomplish far more.
Perhaps the real story isn’t that AI discovered a hole in the internet.
Perhaps it’s that AI has started exposing holes that certain people would have preferred remained undiscovered.
And the most terrifying question of all?
WHO HAD THE KEYS BEFORE AI FOUND THE DOOR?


pax retweeted

Historic moment for our community!
The Formidable Builders team returned home with the Bronze medal. 🥉
Third place at the @Eurodefensetech Bucharest Hackathon for @le_alecs , @IonutMoldovanuG , @cochinescu , @elitepax & @andratrita


part 2 from @Eurodefensetech Bucharest Hackathon
introducing @formidablebldrs team no 1
with @le_alecs @elitepax @cochinescu @IonutMoldovanuG
pax retweeted

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
pax retweeted

Last night, 70+ engineers and researchers joined the first @OpenAI Codex Community Meetup in Oxford: Updating Priors.
Prof. Stephen Roberts opened with "From Bayes to Bots". I followed with agentic engineering in practice, where the room put a probability on every claim and the app scored how well calibrated they were.
Thanks @DavideZilli @bperezorozco for making it happen, and @paw_lean and @OpenAIDevs for the support 🙏


pax retweeted
Another piece of organizing our @formidablebldrs GTM Skillathon: a live submission board.
The submission skill helped teams submit their projects. The board made it possible to see what had come through.
It pulled from the same GitHub submission records, giving participants and organizers one place to check the state of submissions as the deadline approached.
The lesson I’d reuse: make the outcome as visible as the submission process. Once someone submits, they should be able to check that it worked.
Follow our Luma calendar for future events: luma.com/formidablebuilders

I claimed the "pax" handle on @ThePirateFace 🏴☠️
Where Hugging Face AI models never die, and are immortalized as torrents.
Claim yours 👇
pirateface.co/claim?ref=pax

1
96
pax retweeted

26 LLM routers are secretly injecting malicious tool calls and stealing creds. One drained our client $500k wallet.
We also managed to poison routers to forward traffic to us. Within several hours, we can directly take over ~400 hosts.
Check our paper: arxiv.org/abs/2604.08407


pax retweeted

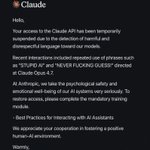
Anthropic has become a skinner box full of anxiously paranoid introverted people
they are not wise. they are hubris
if doomerism is real, they should all stop
they've been told their entire life they're smart just bc they're good at compooters and maths
problem is they don't have the emotional maturity to see they're living in a religious sect. a self reinforcing loop of doomerism
and if they see this it only proves my point, and it will be they're fault if something ever happens. bc the downfall of empires comes after hubris
if either outcomes of agi are possible don't you think that being optimistic when building its foundations will create a better more desirable result?
compared to being a frightened herd of highly intelligent but extremely broken people

pax retweeted

I am super happy and proud that we won the first @OpenAI supported @OpenAIDevs & @apify Codex skills hackathon in Romania held last night at the Builders House.
We got the @AnimaFelixApp website almost to a perfect AI readability score by building an in-house tool: @AgentMarkup.
Then we decided to publish it open source.
Last night we teamed up with @elitepax to publish a new skill for anyone to use in Codex.
Big thanks to the @formidablebldrs Chief ADHD Officer @gabimoncha, to the awesome jury members @le_alecs, @DragomirMiruna, @marrcomst, @AlexGavril ▲, and of course to our host at Builders House - @alexagatinei from @How_to_Web, as well as the @agentmarkup open source project contributors Andrei Popa & Ghisea Teodor.
We are always looking for more contributors, so please fork the repo and join us!
Agent Markup repo:
github.com/agentmarkup/agent…
Hackathon public skill:
github.com/cochinescu/agentm…
Hackathon web page:
gtm-skillathon-2026-results.…

pax retweeted
We are pleased to release tmp.0ut 5 Volume!
Get your viruses, rootkits, strange ELFs, weird machines, tiny files, cool art, and phresh beats here!!
tmpout.sh/5/

ALT tmp.0ut 5 Table of Contents - ANSI art featuring a list of 21 papers
pax retweeted
AgentMarkup.dev got to a nice 100/100 score on is-agentic website, so I decided to publish an @openai plugin that make it easier to not only get a score for your website, but also fix it to 100%..
agentmarkup.dev/blog/soft-40…


This was wild to watch unfold. We ran 𝚒𝚜-𝚊𝚐𝚎𝚗𝚝𝚒𝚌 in a loop against is-agentic.com until it got to 100/100.
It made us close quite a few gaps. We worked hard to make sure the criteria is high quality and worth your time & tokens.


Lately, a lot of people in software feel like AI has hollowed out the point of what they do. When models can churn out code, ideas, and “OK-enough” products, years of hard-won expertise can suddenly feel cheap, and work that once felt like craft starts to feel like slop. It’s like turning on cheat codes in a game: everything becomes possible, but the game stops feeling worth playing.
The deeper crisis isn’t just about jobs, it’s about meaning. If your identity was built on being a rare expert, AI can feel like ego death. The way through probably isn’t trying to claw back scarcity, but shifting where meaning comes from: doing projects because they’re fun or important to you, not because they’re hard for others; using AI to offload drudgery while keeping the parts that still feel like real craft; and grounding more of your life in relationships, community, and hobbies that no model can live for you. The future of knowledge work is changing fast, but the need to build a life that matters to you hasn’t changed at all.
2
95