

Cyber Defense Researcher | China Focus @CSS_ETHZurich. Previous Italian govt, @PacificForum and @NYPD1Pct
Zurich, Switzerland
Joined July 2013
- Tweets502
- Following1K
- Followers947
- Likes1.2K




Pinned Tweet
Fresh off the press: “One Network, Two Systems”, published with @ukctransparency
The report examines research security risks in UK–China university cybersecurity partnerships by mapping identified collaborations and highlighting higher-risk cases. Where available, it also includes responses from UK universities to formal requests for information about these links.
Two case studies examine cyber schools at Chinese defense-linked universities and faculty connections to state, military, and national security entities, as well as their collaborations with UK universities.
The Telegraph’s coverage of the report further explored the implications of these findings. A summary of the key findings is also available on Natto Thoughts. Links in the comments.

Leaked files from Chinese company ZRON show a vast product catalogue and police (MPS) customers. But what did they actually buy from it, and how did AI fit in? Our new Natto piece digs in. Big thanks to @JusticeRage for insights from his own analysis of the leak. Link 👇


Eugenio Benincasa retweeted
This new Natto Thoughts three-part series digs into ZRON, a Chinese commercial hacking company whose internal data was recently leaked and which Natto Team got access to.
Part 1 looks at what has endured and what is evolving in China's commercial hacking ecosystem since the 2024 i-SOON leak, which gave us a rare window into how private contractors hack for Chinese state agencies. Link 👇

Eugenio Benincasa retweeted

🚨 New @threatinsight blog covering a 🇨🇳- aligned threat actor targeting US AI policy circles in spearphishing campaigns in recent months:
proofpoint.com/us/blog/threa…

Eugenio Benincasa retweeted

MI5’s latest warning on Chinese-linked research funding highlights a broader European vulnerability. A recent report by @eubenincasa maps research-security risks behind UK-China university ties. The debate is significant for Italy too: here’s why ⤵️
decode39.com/16775/uk-china-…
Eugenio Benincasa retweeted

Full details on what we've been able to find out about this so far coming this evening from @ukctransparency
Initially, it looks like:
The research targeted was focused on signals intelligence and cyber - an area where there is a surprising degree of collaboration between Chinese universities and British ones, as per our July paper - and an area where Chinese state hostility to the UK is acute, with cyber attacks targeting our infrastructure, healthcare providers, companies, MPs, you name it
The Chinese institute's ties to Chinese security were not totally secret
This is a major escalation in the pressure MI5 is putting on universities
Some of the money from the Chinese institute may have been laundered through well-known Chinese government funding organisations
More to follow.

MI5 has issued an unprecedented public warning about a new Chinese spy threat targeting British academics.
The Security Service says a Chinese institute is secretly trying to exploit the expertise of universities and other research bodies to help Beijing build more powerful espionage tools.
In a highly unusual alert, it strongly advises everyone involved in UK academia to cut ties with this company – or risk criminal charges under national security legislation.
Sky's @haynesdeborah explains
Today MI5 issued its first publicly published espionage alert, warning UK universities about CGTRI (中国通用技术研究院). MI5 says it has very strong ties to China's MSS and 100+ UK-linked academics contributed to CGTRI-funded projects, incl. AI and cybersecurity.
The "One Network, Two Systems" published with @ukctransparency maps UK-China university cyber partnerships, highlighting institutions embedded in China's military and security system👇

Fresh off the press: “One Network, Two Systems”, published with @ukctransparency
The report examines research security risks in UK–China university cybersecurity partnerships by mapping identified collaborations and highlighting higher-risk cases. Where available, it also includes responses from UK universities to formal requests for information about these links.
Two case studies examine cyber schools at Chinese defense-linked universities and faculty connections to state, military, and national security entities, as well as their collaborations with UK universities.
The Telegraph’s coverage of the report further explored the implications of these findings. A summary of the key findings is also available on Natto Thoughts. Links in the comments.
Eugenio Benincasa retweeted
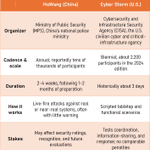
Last week @CISAgov kicked off Cyber Storm, the biennial exercise where US public and private sectors simulate response to a major attack on critical infrastructure.
A month earlier, China ran its own nationwide exercise, HuWang (护网). Now in its tenth year and organized by the Ministry of Public Security, it runs on a completely different model (see table).
New from Natto Thoughts, a look at how HuWang works, how it evolved alongside a decade of shifting Chinese cyber law, and what it means for talent pipelines, the domestic security industry, and China's APT ecosystem.
Link in the comments.

Eugenio Benincasa retweeted

🆕 This article examines how, & with what effects, the #RMSV & related measures have restructured #China’s domestic vulnerability ecosystem @CyberMyri @eubenincasa @DakotaInDC @CSS_ETHZurich @Georgetown
Read it📒tandfonline.com/doi/full/10.…
@APSAtweets
@apsa_itp
@tandfonline

Eugenio Benincasa retweeted

Forthcoming article in @ISQ_Jrnl!
Trump and Xi are sitting down to talk AI this week. @AnthropicAI says we need to "pace the frontier"—and we need China's help to do it.
Could the US and China ever agree on arms control for frontier AI? What would it take?
🧵 [link below] 1/


Next week on Natto Thoughts, we unpack China’s massive nationwide cyber exercise, how it mobilizes tens of thousands of participants, shapes talent and industry, and why its scale and intensity set it apart from Cyber Storm
nattothoughts.com/


We’re excited to host Cyber Storm X — the tenth iteration of America’s premier National Cyber Exercise. This week, federal, state, local, and private-sector partners come together to test and strengthen our collective cyber resilience. #CyberStormX

ALT Image shows an individual standing and speaking at a podium. There is another individual standing behind them, against the wall. The wall is blue with the CISA logo and a clock displaying the time in 5 different time zones. There is also a blue flag with the CISA logo against the wall.
Eugenio Benincasa retweeted
🚨🌜 Today we are releasing a new @threatinsight blog on BlueMoon, an exploit kit that chained “patch-gap” Chrome zero-days with a Windows zero-day and had indicators of AI-assisted development. It was used by at least four espionage-motivated threat actors since late August.

Eugenio Benincasa retweeted

We were finishing our investigation draft when this reporting (@razhael) scooped us. It overlaps with several of our findings and is truly worth reading. I think this is a story worth watching closely..
Thread for additional points from our analysis. 🧵
reuters.com/world/openais-ro…
Eugenio Benincasa retweeted
Two weeks ago, the US issued an advisory identifying the China-linked QTFY hacker group and its reported ties to a network of Chinese cybersecurity companies. The advisory linked QTFY to Nanjing Xinjiuwei Network Technology (XJW), which in turn has business relationships with several other Chinese cybersecurity firms.
This new Natto Thoughts piece widens that circle, examining two of those companies, Elextec Cybersecurity (ELEX) and Nanjing Lexbell, and identifying additional evidence of their ties to China’s military and security agencies (link in comments).
For ELEX, we found pages from the company’s own website, since scrubbed, describing products with intelligence and military applications, alongside a client list naming MSS and MPS bureaus and PLA-affiliated entities. For Lexbell, we trace the PLA-linked backgrounds of its leadership and document a record of contract wins from PLA-affiliated organizations.
nattothoughts.com/p/widening…
