


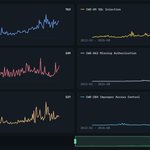


August 2026: 12,275 CVEs published in one month.
That's almost double the 12-month average of 6,256, and the average is climbing too.
If your triage process was sized for 2023 volumes, it's already underwater.
The fastest-growing bug class since 2023 is missing authorization: code that works fine but never checks who is asking.
613 of those CVEs in August alone.
That's also when AI coding tools went mainstream.
Coincidence is doing a lot of work here.
exploit-intel.com/stats


Exploit Intel retweeted

I have found a few bugs and exploits in my time. I was once threatened with legal action, another time after much following up said company informed me that it wasn’t a bug. It was fixed in their next patch.
Everyone who I know that finds exploits has the same stories.
Exploit Intel retweeted

This is *quite* a post.
I honestly don't know offhand: Has Microsoft as a company ever before suggested in any official statement that it might seek to have criminal charges brought against security researchers who drop 0days?
microsoft.com/en-us/msrc/blo…


And while I've got your attention, patch your VMWare Fusion - CVE-2026-41702. exploit-intel.com/blog/posts…

We just released a Hermes Agent "Exploit Intel Harness" which turns Hermes into your Personal CVE vulnerability research assistant. This is a "diet" version of our forge tools - Check it out - exploit-intel.com/blog/posts…


CVE-2026-4105 - local root on systemd-machined. Two D-Bus calls, no auth. Fed it to CVEForge, had a working exploit in 72 minutes - then it found a bypass: exploit-intel.com/blog/posts… #CVE20264105

Back in the day we had milw0rm and a dream. Now it's 370K vulnerabilities, 92K with known exploits and growing. We're proud to finally hit the green button on our Exploit Intelligence Platform. Still early, still rough — but the foundation is real. exploit-intel.com/?v=2
