

Охотник на жучков
Netherstorm, Area 52
Joined June 2014
- Tweets101
- Following180
- Followers238
- Likes97




Ivan Chalykin retweeted

A blog by me & @1lastBr3ath discussing our findings we presented in Black Hat Europe #BHEU talk titled “Exploiting CSP in Webkit to break Authentication/Authorization”. Find out how we made more than $100k in bug bounties with a bug ignored by Apple. threatnix.io/blog/exploiting…
Ivan Chalykin retweeted

Found a hidden HTTP param? Look deeper, maybe there is a mass assignment/autobinding vulnerability.
Sometimes changes in objects are hidden too and you need to closely explore the app.
Source:
itzone.com.vn/en/article/mas…
#CyberSecurity #BugBountyTip #BugBounty

Ivan Chalykin retweeted
We often get confused how Samesite affects cookies in different attacks in modern browsers. So, we have made a memo and now share it with you.
#CyberSecurity #BugBountyTip #BugBounty

Ivan Chalykin retweeted
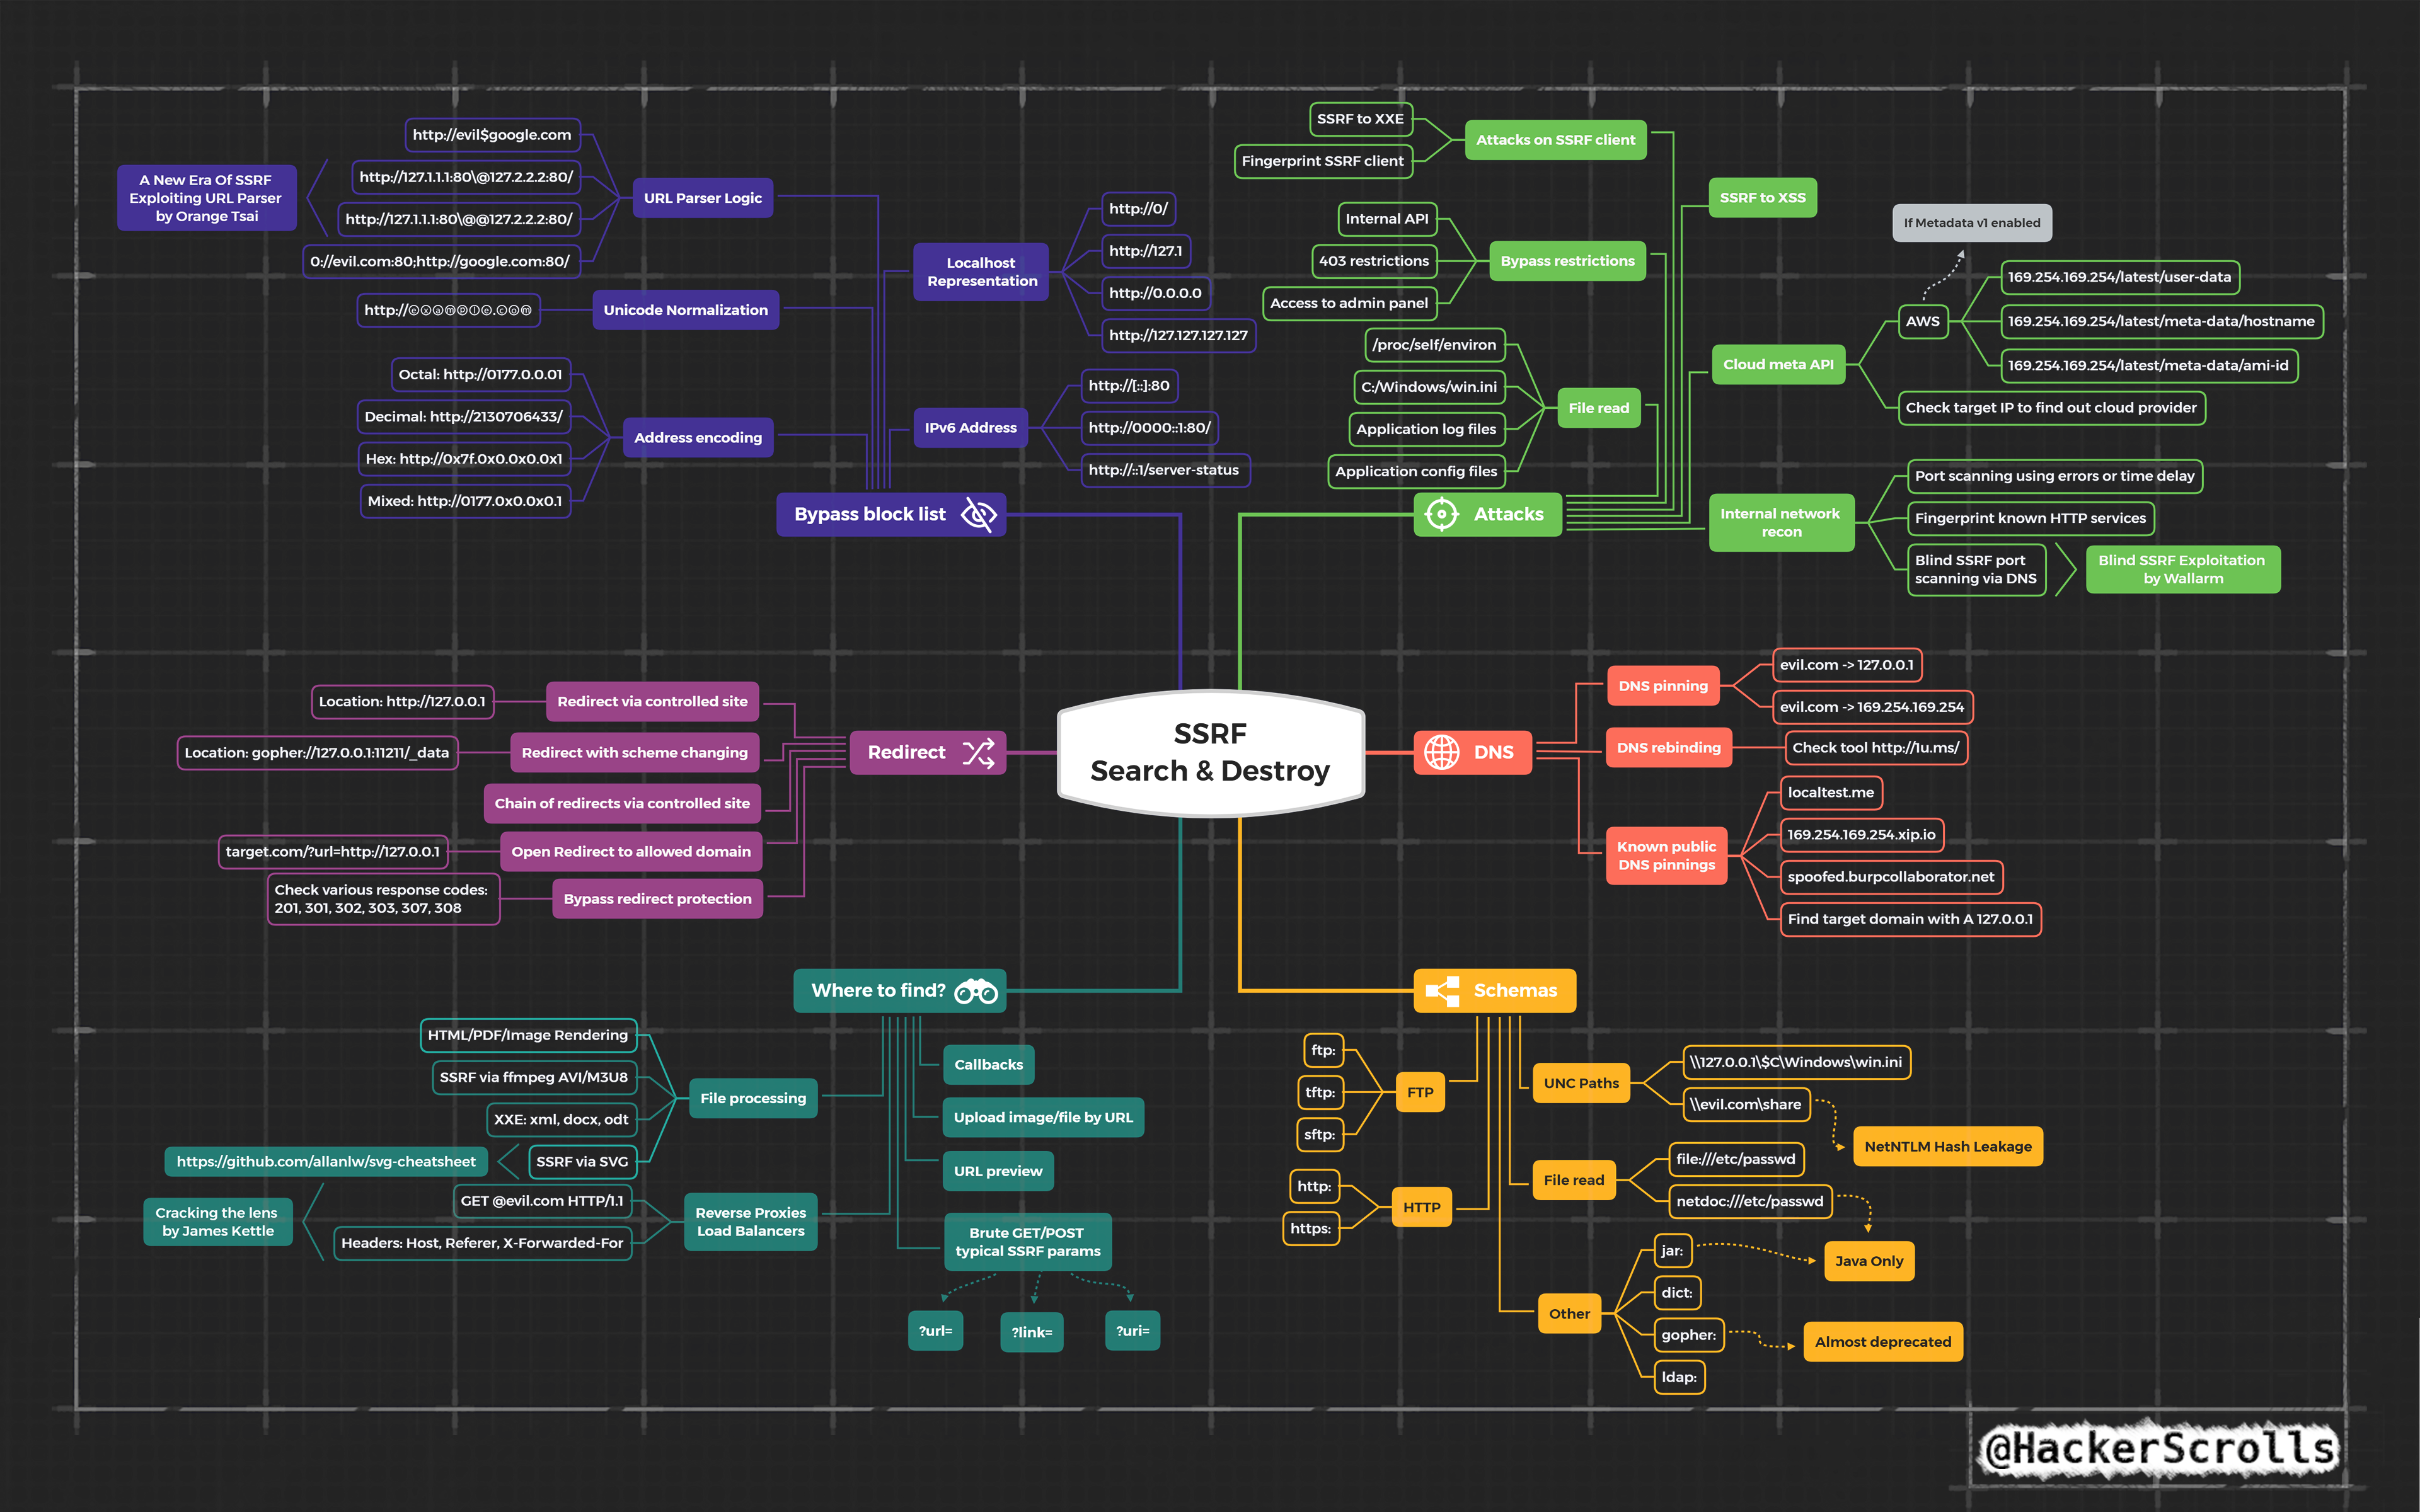
We have combined all the tricks we know about SSRF into a single mindmap.
If we missed something, write about it in the comments!
High resolution: raw.githubusercontent.com/ha…
XMind source: github.com/hackerscrolls/Sec…
#CyberSecurity #BugBountyTip #BugBounty

Ivan Chalykin retweeted

Вышел выпуск подкаста №4.
Наконец cобрались обсудить давно интересующу нас тему: менджмент и бизнес - особенности данных веток таланов для пентестера. Есть ли вобще другие?
Уже разлит по площадкам
soundcloud.com/m1mo-croc
music.yandex.ru/album/103216…
podcasts.apple.com/ru/podcas…
Ivan Chalykin retweeted

#bugbountytips
One more way to increase the impact of opening arbitrary URLs in a built-in WebView is Universal XSS. They are widespread on #android! Steps:
Ivan Chalykin retweeted
Have you ever wonder about fast and easy-to-use SOCKS proxy over DNS?
Here it is
github.com/fbkcs/ThunderDNS from @fbk_cs
You don't even need to compile it!
#CyberSecurity #RedTeam #Pentest

Ivan Chalykin retweeted
CSRF in 120 seconds!
As you remember Cookies without SameSite are treated as SameSite=LAX in Chrome.
But there is one exception that can be used as a temporary policy bypass.
More detailed examples: medium.com/@renwa/bypass-sam… by @RenwaX23
#CyberSecurity #BugBountyTip #BugBounty

Ivan Chalykin retweeted
Using other hosts as a gateway, sometimes, you can get access to other VLANs or bypass the firewall.
That is a task for gateway-finder!
Check the improved version by @whitel1st:
github.com/whitel1st/gateway…
#CyberSecurity #Pentest #RedTeam

Ivan Chalykin retweeted
Were you surprised when your cross-domain attack didn't work?
Meet the new reality with SameSite Cookies.
Now Chrome and Safari recognize Cookies without the SameSite attribute as SameSite=Lax by default.
#CyberSecurity #BugBounty #BugBountyTip

Ivan Chalykin retweeted

Meet JWT heartbreaker! A Burp extension that finds thousands of weak JWT secrets lab.wallarm.com/meet-jwt-hea…
Ivan Chalykin retweeted
Got root access to a server? Run 3snake and grab the attention to the server. Wait for admins and grab their ssh passwords!
github.com/blendin/3snake
Trick by @cherboff
#redteam #cybersecurity #Pentest

Ivan Chalykin retweeted
Yet another trick about CORS!
Do not forget to check Origin: null
#CyberSecurity #BugBountyTip #BugBounty

Ivan Chalykin retweeted
Incredible mindmap about hacking iOS applications by @hd_421
Pay attention, we have prepared two versions:
1. Full Security Assessments
2. Shorter BugBounty version
XMind source:
github.com/hackerscrolls/Sec…
#CyberSecurity #BugBountyTip #BugBounty #iOS

Ivan Chalykin retweeted
Found a Stored Self-XSS? Chain it with Login/Logout CSRF and increase the impact!
Few examples:
geekboy.ninja/blog/airbnb-bu…
medium.com/@ch3ckm4te/self-x…
hackerone.com/reports/314518
#BugBounty #CyberSecurity #BugBountyTip #XSS

Ivan Chalykin retweeted
There are a lot of known vulnerabilities in Cisco. But available Cisco Smart Install is our favorite. This one helped us in few red teams and even bug bounty.
Thanks to @sab0tag3d for an awesome exploit github.com/Sab0tag3d/SIET
#redteam #pentest #cybersecurity

Ivan Chalykin retweeted
We continue to talk about attacks on CORS.
This time, we have prepared a set of ideas for bypassing lists of allowed hosts.
#CyberSecurity #BugBountyTip #BugBounty

Ivan Chalykin retweeted
WebSocket is a widespread technology in modern Web. Incorrect implementation can lead to a simple but critical vulnerability – WebSocket Hijacking.
Example:
hackerone.com/reports/535436
Try it in the @PortSwigger Lab:
portswigger.net/web-security…
#BugBountyTip #CyberSecurity #BugBounty

Ivan Chalykin retweeted
There is a popular opinion: bad CORS like <Access-Control-Allow-Origin: *> is unexploitable. Browser won't send cookies in this case.
It is a delusion. You can exploit it with a Chrome cache feature!
For example:
hackerone.com/reports/761726
#BugBountyTip #CyberSecurity #BugBounty

Ivan Chalykin retweeted
Remember our tweet about JS static tracking?
It seems like a more powerful way has been found for this!
Look at this tool by @Abdulahhusam:
github.com/ahussam/url-track…
Old tweet:
teapawt.org/hackerscrolls/status/1…


Do you track changes in JS static? Not yet?
Tip by @igc_iv how to make it easier
github.com/cablej/FileChange…
[1/2]
#BugBountyTip #OSINT #Pentest
