

💍🇺🇸✝️♒♂️ | 🎙️ cohost: Stand Up with Myc and Bobz | 🤖 creator: The Universal Basic Network | The Trust Package | First Step Academy | [email protected]
Massachusetts, USA
Joined February 2010
- Tweets5.3K
- Following581
- Followers216
- Likes18.8K




clou goo do

Now that coding is solved, is there any reason I should not make my own version of every single paid software service that I use, to make one completely unified business system? For a while, I felt this would be foolish / AI psychosis. But now it seems like every SaaS will increasingly try to do everything and raise their prices accordingly, so it only makes sense to stick with any SaaS if you're really happy to rely on them for everything. But it also feels increasingly like even the smallest necessary GUI interactions are a waste of time. Like having a business where the public-facing points and the internal systems are 100% exposed to agents is drastically superior to one where even 95% of stuff can be accessed by agents. So it's really starting to look like building and maintaining a personal everything app is sensible? At least if you run a one-man business?
lion gonna lion is the thing
humans do not want to eliminate lions
they have been driven to
by lack of alignment with each other

Them: "A lion can still kill a human in unarmed combat. Intelligence isn't everything!"
Me: "A lion can kill a human if the lion, despite its lack of strategic cognition, happens to attack the human before the human has time to prepare. A human who is allowed to pick their own time to attack a lion, and use serious technology, and bring allies, will win nearly 100% of the time. On a macro scale, lion populations have gone from millions before agriculture, to maybe 25,000 in the wild and 10,000 in captivity. Humans have an individual combat advantage when they are given time to prepare. Human society has an absolute logistical advantage compared to lion society. Humans individually and collectively have higher strategic intelligence with which to pick their fights and time them. And now it is impossible for lions to reverse their situation, because the lions were too unstrategic to do anything about humans before the humans explosively replicated and teched up. If lions collectively wanted their posterity to not end up mostly nonexistent or in cages, lions would have needed the collective intelligence to group up and stop early primates while lions still *had* an individual combat advantage. Lions would have needed to do that *before* primates got smart enough to invent pit traps and slingshots and fight them to a standstill, because a status-quo standoff gives later primates the time in which to invent agriculture and guns; the primates have advantage in their speed of change, progress, and adaptation. Do you understand that this analogy does not say what you think it does?"
Them: "You're the one who doesn't understand what I'm saying. I'm saying that a lion can maul a smart person, end of story. So being smart isn't as high-status as you like to imagine."
Me: "But lions being higher-status than humans - as you define that by reference to unarmed unprepared individual combat only - doesn't prevent the human side from gaining an overwhelming logistical advantage...?"
Them: "I don't care about logistics. I care about status."

gonna be a hot one

I have a sneaking suspicion that the extreme eastward shift & intensity of this yr’s “Super” El Niño has something to do w/ the unprecedented, exceptionally early Sudden Stratospheric Warming Event that’s in most model forecasts
Plots via @Recretos’s site
severe-weather.eu/polar-vort…


ok so go is fallen, p=/=np is wabbling
where do we move the goalposts after this?
chip fab, rocketry and kardashev?
the web is not as free is it used to be
stay frosty cowboys

Nobody warns vibe coders about this part.
You can ship an app in a weekend.
You can also break 6 laws in that same weekend without knowing it.
Here's what to check before you launch:
1.) Kids
If signup doesn't ask for age and a child under 13 joins, COPPA fines can reach $53K per child.
2.) Fonts
Loading Google Fonts from Google's servers sends visitor IPs to Google. A Munich court ordered a site to pay one visitor €100 for this under GDPR.
3.) Session replay
Recording what users type without consent can count as wiretapping under California's CIPA, at up to $5K per violation.
4.) Launch emails
No unsubscribe link or postal address breaks CAN-SPAM, at up to $53K per email.
5.) Subscriptions
If renewal terms aren't right next to the button, California can treat renewals as unconditional gifts you have to refund.
6.) User uploads
Without a registered DMCA agent, which costs $6, you lose safe harbor. Statutory damages can reach $150K per willfully infringed work.
None of these cost much to fix.
All of them cost a lot to ignore.
Paste this into Claude before launch:
"Check my app for: missing age gate, externally loaded fonts, session replay without consent, marketing emails without unsubscribe and address, renewal terms not beside the subscribe button and no DMCA agent. Fix what you can and list what I need to do myself."
Not legal advice. Talk to a lawyer for your situation.

tech only pays as well as they do because they are shit at training

I'm starting to sense a divide in the tech industry:
- People thriving on autonomy who are reinventing how they work and what tools they use with AI: LOTS of work, but they're enjoying it and getting very efficient
- People used to being mentored / trained / or simply told what to do and how. Frustrated with the lack of guidance from management on what to do with AI; also frustrated by seeing some of their peers thriving; increasingly bitter about AI and the state of the industry, as a whole
Neither group seems to be aware that there's another group, or have empathy for the other group
we have taken your feedback from the popular work
escape from samsara
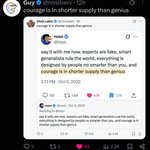
a tale of impossible courage
we have now included more ways to take a break from samsara without actually leaving
please keep your arms and legs inside samsara at all times
yikes

You open a terminal and type ssh user@server through Tor. You expect the exit relay to be a simple last hop that dumps your encrypted packets onto the open internet. For three days in early October, on 333 of those exits, that assumption was wrong.
Tor has roughly 3,000 exit relays. The attacker controlled about 10% of them. Those relays were reconfigured so that any SSH connection on port 22 was silently redirected to one of 12 interception servers the attacker operated. The exit no longer forwarded the connection to the real server. It completed the TCP handshake itself and presented its own SSH host key.
If you ignored the “REMOTE HOST IDENTIFICATION HAS CHANGED” warning and typed your password anyway, the interceptor captured the password, watched every command you typed, and then opened a second connection to the real server to try to install Ebury 1.8.3 (an old OpenSSH backdoor and credential stealer). The researcher who discovered this used exitmap to scan the exits and a honeypot to confirm the interception servers were speaking Paramiko.
At the same time the exits were altered to block the common encrypted mail ports (25, 465, 587, 993, 995) while still allowing the unencrypted ones. The goal was to force or capture plaintext email traffic as it left the Tor network.
The initial foothold appears to have come from a reused password on a management server in late August, after which Ebury was installed and the configuration changes were pushed. The Tor Network Health team began flagging the relays BadExit on 4 October; by 5 October the malicious exits were gone from the consensus.
The interesting part is not that someone ran a bad exit. It is that the attacker turned ordinary Linux hosts into exits by editing their torrc files and then used the exit position itself as the man-in-the-middle point. The cryptography of the circuit still protected you from the middle relays. The moment your traffic left the network, the exit could see (and modify) the cleartext stream if the application protocol allowed it.
Treating “I am using Tor” as a single security property. Exit-node compromise shows it is actually two: the circuit hides you from the destination, and the exit is assumed not to be actively hostile to the specific protocol you are speaking. For three days, roughly one in ten exits violated the second assumption for SSH and email.
Host-key verification and key-based authentication stop the SSH half. The email half is harder; once the exit is the one talking to the mail server, encrypted ports can simply be dropped. The practical reminder is the same one that keeps appearing in physical-layer attacks: the model assumes the last device or the last hop behaves the way the protocol designer expected. When it does not, the higher-layer protections never get the chance to run.

more like
a secret third thing
p#&np

So, AI has produced a disproof of the Exponential Time Hypothesis.
Is it just me, or is everybody on the planet who knows anything about computational complexity wondering the same thing tonight: could this be the universe's way of whispering that P=NP?
Nah, I don't think it's just me.
I still think it's more likely that P≠NP. But my odds on that have shortened dramatically in the last 4 hours.


