
panic oriented full heap groomer
Joined November 2021
- Tweets284
- Following191
- Followers30
- Likes529



great work!
and a comment: not excluding apple and anonymous reporters in the 'top reporters' chart would be more informative for statistics.
Your bad humor about the article cannot justify such a big-scale genocide and every single person took part in it - including the *cool-vibed* DFSec researchers. Shame on every single of them.
unavailable
Potato Soup 🇵🇸 retweeted

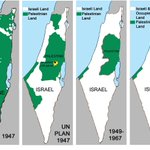
Google Maps has been updated to show Zionist-holocausted Gaza. This is part of Rafah.

Nice finding, but bro, you ought to publish a write-up, not a drama novel. 80% of the whole text tries to convince the reader how dramatic this is. C'mon bro, I was reading a memory corruption writeup and my emotions are unnecessarily triggered.
xitter.cf/_MrNiko/status/2103919…

iMessage EXR. zero click. heap overflow before the banner finishes.
CVE-2026-86869. libAppleEXR sizes the buffer for 3 channels. 12 bytes.
CompressedInterleave4 writes 4. 16 bytes. every pixel.
three of those four bytes come from the file.
BlastDoor never decodes EXR.
Spotlight and the photo indexer do, later, with SDR hardcoded on.
no tap. same ImageIO path on iPhone, iPad, and Mac.
fixed in the 27 releases. older fleet still sits on it.
credit: Niels Hofmans / ironPeak
ironpeak.be/blog/ex-arrr-sai…
#iOS #ExploitDev #InfoSec
Potato Soup 🇵🇸 retweeted

Her name is HIND RAJAB💐🌷
🤞🏾🪶♾❤️
And She was more brave than every single one of you at ESPN


Kyrie Irving has offered to pay Houston Texans linebacker Azeez Al-Shaair's $11,941 fine for having the name of a Palestinian girl killed in Gaza written on his eye black during Sunday's game against the Buffalo Bills. spr.ly/6012BGpQce

bro if you give playing your game to LLM, too, then what exactly are you going to in the saved time 😂
xitter.cf/wuyang_zhou/status/209…

> To prevent weaponization or malicious use, the post-exploitation phase will not be discussed.
Thanks for good intention but I think this won't change anything in the AI age 🙂
if an offensive security company employee has been thought to have a valid cyber use case, then who else wouldn't? 😅