
Security at @framer. I build and break things on the internet.
Amsterdam, The Netherlands
Joined February 2009
- Tweets54
- Following80
- Followers2.8K
- Likes476



Koen Rouwhorst retweeted

Introducing Skills: teach the Framer agent how you work. Save instructions for your design system, writing style, or CMS workflow, then reuse them across tasks. Reference pages, components, and styles in your skills so the agent follows your designs. framer.com/skills
Koen Rouwhorst retweeted
GPT 5.6 Sol, Terra, and Luna are now available in Framer.
The new lineup gives you more control over quality, cost, and speed. Sol is our strongest creative model yet, and the first to score 100% on our hardest internal benchmark, at the same credit cost as GPT 5.5. Terra delivers GPT 5.5-level results at 0.6× the credits, while Luna runs 2× faster than any previous option at 0.4× the credits.

Koen Rouwhorst retweeted
I tried to write down every lesson we learned and trade off we had to make, building agents on a canvas for @framer. If you build products, you might like this.
framer.com/blog/building-fra…

We just shipped an all new version of Framer. Use the built-in agent right on the canvas, or bring your own agent (Claude, Codex or Cursor) to work on your projects. Everything happens on a branch, so you review the diff and merge only when you are ready. Give it a try!

Agents: AI built into every part of Framer to help you become extremely productive, not replace you. Agents can design pages, update your site, manage your CMS, improve SEO, fix responsiveness, understand analytics, and, most importantly, help you ship. framer.com/


Koen Rouwhorst retweeted

Framer's biggest launch in years is happening June 16
We're hosting watch parties in 12 cities around the world so builders can experience it together IRL
Austin • LA • NYC • SF • Seattle • Vancouver • Toronto • Amsterdam • Barcelona • Berlin • London • Warsaw
Want in? DM me
As an engineer at @framer, one of the things I keep pushing for is reducing the number of credentials that engineers have to manage themselves. GitHub personal access tokens are a good example. They are often scoped too broadly, stored in plaintext in dotfiles, and duplicated in multiple places.
GitHub's gh CLI solves most of this. Instead of manually generating a token and pasting it somewhere, you just run 'gh auth login' to authenticate via a browser-based OAuth flow. No token touches your clipboard or shell history. It creates an access token with sane default scopes, stored securely in your OS keychain rather than a plaintext file on disk.
The nice thing is that other tools on your machine can use the same authentication instead of each needing their own personal access token. In scripts, you can use 'gh auth token' to retrieve the access token. Scopes can be expanded using 'gh auth refresh -s <scope>', so you only add broader access when your tools actually need it.
You can take this a step further with the gh Go module (github.com/cli/go-gh) that lets you tap into that same authentication programmatically from your own tooling. We did this for our internal developer tools that need GitHub access, so there is no need for engineers to manually generate, configure, or manage separate GitHub personal access tokens.

Domain registrars may be one of the most overlooked single points of failure in our stack. We spend serious time and resources securing our cloud infrastructure and workloads, but our domain registrars rarely get the same level of scrutiny. Even though our domains underpin everything we operate. 🧵
You can easily check this for your own domains. Do a whois lookup and check the domain status fields. Statuses starting with "client" (e.g. clientTransferProhibited) are set by the registrar and can be removed by the registrar. Statuses starting with "server" (serverDeleteProhibited, serverTransferProhibited, serverUpdateProhibited) are set by the registry and can only be removed through the out-of-band process described above.

ALT Whois framer.com
For your business-critical domains, move to a well-established registrar that supports registry locks (CSC, MarkMonitor, Cloudflare). Configure multi-party authorization for unlocking, so no single individual can approve changes. Use role-based contacts, not personal emails. Enforce phishing-resistant MFA. And set auto-renewal with a multi-year buffer. These controls have been around for many years. They are just underused.
Koen Rouwhorst retweeted
We're looking for a new batch of beta testers for Framer with Claude / Codex. If we missed you the first time, feel free to enter again.
xitter.cf/koenbok/status/2037107…

If you are both a Framer and Claude / Codex / Cursor user, we would love your help to beta test something new.
framer.com/llm




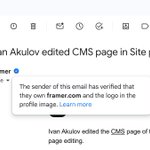
All @framer emails now show a verified logo and blue checkmark in supporting inboxes like Gmail. Here is what is behind that little checkmark. 🧵

ALT Framer email in Gmail with verified logo and blue checkmark.
The standard method for organization validation is a phone call to a publicly listed phone number. Framer is a remote-first company. We are incorporated in the Netherlands and have an office there, but no fixed phone line.
So we asked legal to draft a legal opinion letter to establish a non-listed number for verification. That got rejected because our counsel was not registered with the local bar association in the required jurisdiction. 🙃
The certificate authority eventually fell back to sending a physical postal letter with a verification code to our physical address listed on Dun & Bradstreet. Yes, we used snail mail to verify our identity for email!
All @framer emails now show the verified logo across Gmail, Apple Mail, Fastmail, and Yahoo.
This is first and foremost a nice trust signal for our users. When an email claims to come from Framer, the verified logo lets them know at a glance that it actually does.