




Timo Stark retweeted

I'll be the first to admit I'm mediocre at exploit development, but I am in contact with enough extremely talented exploit developers to say this for certain:
Anyone claiming they were "easily" able to generate a working php2shell exploit with AI is either:
a) a world-class exploit developer with an extreme case of imposter syndrome.
b) currently looking at some very confident-sounding but wrong LLM output.
I'm rather certain it's the latter based on the number of AI-hallucinated exploits I've seen posted on GitHub. Threat actors are also blasting my honeypot network with "php2shell" exploits that not only don't work, but aren't even within 10,000 miles of anything to do with how the exploit actually works.
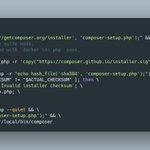
I've seen the same technique from the attached image in multiple alleged "php2shell exploits", including one on GitHub with over 100 stars. Problem is, it's not php2shell, nor is it even a vulnerability at all. It's a technique known as "session poisoning", which can be leveraged to exploit local file inclusion (LFI) vulnerabilities in PHP apps (not PHP itself).
The only thing it has in common with CVE-2026-109618/CVE-2026-109619 is they both use the "PHP_SESSION_UPLOAD_PROGRESS" feature. And mitigation advice for both issues reference setting "session.upload_progress.enabled" to "Off".
People are shoving loose details of the vulnerability into LLMs, the LLMs are keying in on the "PHP_SESSION_UPLOAD_PROGRESS" string, then generating session poisoning code that has nothing to do with the actual CVE. And because the people doing this have absolutely no idea what they're doing, they're confident enough to post their "proof of concept exploit" to GitHub and share it on social media.
So if you see people talking about "session poisoning + LFI" it's likely their LLM hallucinated an exploit based on a 2018 blog by Orange Tsai talking about a local file inclusion attack vector.
What's even worse is that "security researchers" are then using LLMs to triage these exploitation attempts, falling victim to the same hallucinations, then confirming there is ongoing mass-exploitation (there currently isn't).
The actual real exploit is very difficult to exploit, and so far I've not seen anyone successfully get it working on more than a handful of PHP version with highly-specific configurations.
LLMs are useful tools in the hands of skilled professionals, but for others, they're often just a Dunning-Kruger accelerator.

Timo Stark retweeted

Major highlight of #Kubecon was catching up with these amazing friends. And visiting @Toastersdeli EVERY DAY for some great food.
@jamesspurin @normalfaults @mtcderek and Ramesh. Sorry @linux_lenny you'd already flown out.


Timo Stark retweeted
The legend @linux_lenny doing a demo at #WasmCon when he hasn't see the demo on his laptop and has to watch the big screen 👏👏👏
Timo Stark retweeted

This year's #Hackdockerfest 🐳 is going to happen in two weeks, and we're going to have:
- Open-source (@Hacktoberfest)
- Drinks 🍺 (#Oktoberfest)
- Food 🍕 (#Fest)
- Quiz 🥁
- @Docker swags 🐳
- Docker Captain @linux_lenny 🐧
- 3-4 more Docker Captains from Freiburg 🎃 – at Freiburg im Breisgau, Germany


We'll have the next #Docker meetup here in Freiburg in half an hour where we will celebrate the following things:
- #Oktoberfest 🍻
- #DockerCon 🐳
- @Hacktoberfest 🦑
- Friday the 13th 🗡️
meetup.com/docker-black-fore…

Timo Stark retweeted

At the height of One Million Checkboxes's popularity I thought I'd been hacked. A few hours later I was tearing up, extraordinarily proud of some brilliant teens.
A thread about my favorite story from running OMCB....

Timo Stark retweeted

What is Docker? 🤔 According to our Docker Captains, it's...
feat. @AbhiVeeramalla, @cigdemkadakoglu, @julielerman, @linux_lenny, @punkdodevops, @raeveen_28, and @normalfaults
#DockerCaptains
Timo Stark retweeted

This smells bad: I received spam from Cyber Press Research pitching this story, which isn’t a good look. Then the place where the data is published (a clear web forum, *not* dark web) advises the archive is corrupted and can’t be read. So what data is the story based on?


@troyhunt Sorry to be the millionth follower asking, but any comments on this?
cyberpress.org/9-4gb-twitter…


Timo Stark retweeted

Is anyone hiring for an SRE / platform / dev happiness role?
I have 20+ years of experience building and deploying web apps. I mainly work with Python, Ruby, shell scripting, Docker, Kubernetes, Terraform, etc. and have experience working with startups to medium sized businesses
Timo Stark retweeted

Looking to start adding server-side WebAssembly functions to your applications? NGINX Unit 1.32.0 is out now with all-new support for WebAssembly Components and WASI Preview 2 host interfaces. Try it out!
#NGINXUnit #ServerSide #Wasm
unit.nginx.org/news/2024/uni…
Timo Stark retweeted

Congratulations to everyone in the #Wasm community for a huge milestone: the launch of WASI Preview 2!
github.com/WebAssembly/WASI/…

Timo Stark retweeted

Breaking my Twitter vow of silence to invite you (yes, you!) to the next NGINX Community meetup in San Jose. I'll be back in California for it and would love to see or meet folks. RSVP: bit.ly/47fN2ns
#nginx #opensource #communitybuilding #javascript #wasm

Timo Stark retweeted

🎉 Big news!
🐋 @AtomicJarInc is now part of @Docker! Together, we will continue to invest in and extend the open-source project that we all love @testcontainers. Read the blog by @bsideup: ow.ly/6gES50Qhv0T

Timo Stark retweeted

👋 Thanks to Jason Schmidt, I got to meet Richard Kiene from @Docker , Inc this week. We got talking and I shared how awesome it is that @linux_lenny is a Docker Caption! 👨✈️⚓️
I also realized there's a lot to Docker I didn't know about - it's not just Docker Desktop and Docker Hub. Richard took a few moments to educate me.
✅ You can start to address supply chain concerns through visibility with Docker Scout
✅ You can then apply rules around registries and images
✅ Ensure environment consistency for developers so you don't get the "well it works on my machine" ever again
Thanks for your time and the run through Richard Kiene! Hopefully see you on the hill, too! 🚲
@F5 @NGINX @DevCentral #AForceFor #DockerCaptains
Timo Stark retweeted

With the release of @spinframework 2.0. Spin now builds wasi-http components. Using this container, you can see how it's possible to run those across Spin, Wasmtime and @nginx Unit: github.com/fermyon/wasi-http…

Timo Stark retweeted
Docker Desktop 4.25 is here! GA of Rosetta for Linux, an optimized installation on Windows, simplified Docker Scout settings, and so much more!
docker.com/blog/docker-deskt…

Timo Stark retweeted
The Kubernetes built-in Ingress resource limits its users with insufficient features and a poor extensibility model - discover how the new Gateway API provides a better alternative to Ingress and how it compares. bit.ly/3QbIYya


