
OSS Supply Chain Security. Founder/CEO/Primary Ariba Admin at https://xitter.cf/t.co/sGmuUU9JbG Sigstore: https://xitter.cf/t.co/dWKlyYu6kv
The Arena
Joined May 2014
- Tweets13.3K
- Following2K
- Followers11.8K
- Likes38.2K


Pinned Tweet
Open source is dying.
We raised over $800M to save it.
Chainguard is the world’s first infrastructure that stops cyberattacks before they can start:
The actual prompt for this was "let's look for pre-auth RCEs in PHP". I'm sharing this so people know this stuff is real and to take agent-assisted scanning seriously.
I kicked if off using Claude Mythos 5.1 (in stock Claude Code) but it uses a skill to drive a harness we built over the last few months.
I don't know if the harness is amazing, but it certainly has a scary track record so far. It's setup to do an agent guided tree search across a codebase, and runs in microvm sandboxes that all have the full source code for the target, as well as the source for any transitive dependencies.
When I built the harness I basically just fed Claude a bunch of Project Zero blog posts describing how they did research and had it build a harness that ran like that, but on our tech stack.
The first phase is just setup and can run with any model, it just does that fetching and assembles the kit environment, and gets a target up and running alongside the source code.
Then we just do some basic suspend/resume stuff over to the hunt phase, where one agent supervises the tree, and the first node kicks off.
Each node is context-aware and aware of the work of all the others. I think I ran this with parallelism 4? So 4 running at any one time. The supervisor can shape the tree and boost nodes or prune. Any node can add more below it with targeted instructions.
A typical run looks like the first node doing a codebase review or building and running a fuzzer or something, all depending on the target. Then based on whatever it finds, it'll queue 4-5 children that go look into those areas. The main system guidance is to validate everything 3 times in clean VMs, and we typically require full exploit chains/POCs.
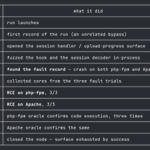
Here's what this run looked like.
We're doing this with a bunch of other open source projects now and companies. We're doing a lot of this for free, even with private companies, across critical infrastructure. We're directly partnered with Anthropic, and can do this even if you don't have direct access to a frontier model yourself.


Dan Lorenc retweeted

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Dan Lorenc retweeted

This is a strange moment we’re living in.
Dario is saying the most sane and balanced shit ever, that’s like completely common sense, and people are hearing ransom voices in their heads.
Here let me try:
“It would be bad if every 14-year-old boy could create massive hacking campaigns, or dox their female schoolmates with deepfakes that make them want to kill themselves, or any number of other things because they have an unrestricted open model that’s smarter than Mythos. Which will soon be possible.
In other words there are millions of young people, and people who have nothing to lose, or people with low self-control that would accidentally or otherwise do extraordinary harm, with unrestricted models this smart.
We’re just saying there should be a tiny amount of friction that prevents those types of seriously dangerous misuse by people who are good but in a (perhaps temporary) bad situation.”
PEOPLE: “So you want to burn books.”
ME: “No. I’m saying there are a lot of people suffering who have no money in this world. Like hundreds of millions or billions of people. People with severe mental problems. People losing their jobs and their relationships and their livelihoods. Or people who had never had any of those things and are willing to do anything to get ahead.
All I’m saying is it’s a good idea to make it SLIGHTY harder to do harm on a whim.
In other words, don’t make the models that are completely unrestricted and this smart publicly available on every model website for free with absolutely no restrictions.
Because if we do that, the amount of harm that will result from it will be completely predictable.”
PEOPLE: “So you only want rich billionaires to have good models, and everyone else is locked down to stupidest stuff forever.”
ME: “Who said anything about stupid?
Everyone should have extremely smart open source AI. All I’m saying is the public and widely available versions of the models should have some basic level of controls around preventing extremely dangerous prompts. Like how to ruin somebody’s reputation or shoot up a school or take down critical infrastructure or steal money from a local bank with bad security, etc.”
THEM: “So you want Dario and Sam to rule the whole world then with no democracy.”
Jfc. This is literally what this debate looks like right now. Virtually everywhere that it takes place.
And the trajectory that we're on is basically going to guarantee that we have these unrestricted open-source models that are way better than Mythos or GPT-6. We are going to have these in the next three to 18 months, almost for certain.
So we're about to find out really fast that when hundreds of millions of people, or billions of people, have access to something that is that dangerous and is completely free and unrestricted, bad things will happen.
And then the same types of people will be like,
"I can't believe we did this. We should have had some sort of controls."
Yeah, no shit, that's literally what we are telling you right now.
Today, @OpenAI, @anduriltech, @canva, and hundreds of other companies reduce their attack surface by 85%.
We are becoming the foundation for modern software.
And now we’re hosting a bug hunt with a $200,000 prize pool. If you find a vulnerability in our system, we’ll pay you up to $200k.
chainguard.dev/unchained/we-…
xitter.cf/lorenc_dan/status/2077…

Open source is dying.
We raised over $800M to save it.
Chainguard is the world’s first infrastructure that stops cyberattacks before they can start:


Whoa, congrats to Chainguard on the 2nd biggest partnership of the day!

Chainguard 🤝 @cursor_ai
Our new partnership is making trusted OSS the foundation for AI-driven development. Now, devs using Cursor can pull from our CVE-free containers and malware-resistant libraries instead of public registries.
See it in action 👇
chainguard.dev/unchained/cha…
There's something charming about watching claude build other agents. When you debug prompts and tool calls, you can almost see it empathize with the smaller, weaker agent.
LinkedIn is going to go wild when they hear about this next week:
browsergate.eu/
Dan Lorenc retweeted

some news;
@latentpatterns 🤝 @chainguard_dev
Chainguard will provide secure images for the embedded terminals within Latent Patterns.
You’ll be able to run Claude code from within your browser. Zero api key provisioning or software installation. It just works, even on a Chromebook, from your browser...
Thanks @lorenc_dan 🍻
ps. @chainguard_dev is hiring, and Dan mentioned employees get a near-unlimited budget for tokens...
Multicloud, my take on Gastown is alive, self-hosting, and cranking.
Gastown showed me the future, this is my version of it. Check it out!
github.com/dlorenc/multiclau…

Send help. I ignored all the instructions and used my Polecats with the Refinery. The Mayor and Deacon reported me to the Witness and the Sheriff is after me.
Dan Lorenc retweeted

If working in OSS sometimes feels like running on a treadmill, then “done” software is the rare moment when the pace finally eases.
By @lorenc_dan, thanks to @chainguard_dev thenewstack.io/put-a-fork-in…

Dan Lorenc retweeted
The recent FFmpeg drama with Google is insane, and I'm surprised that so many people agree with FFmpeg's take on X.
Google isn't even demanding FFmpeg's maintainer to fix the security bug. Are we living in a world now that sending LEGITIMATE bug reports is suddenly a sin?

I am the main developer fixing security issues in FFmpeg. I have fixed over 2700 google oss fuzz issues. I have fixed most of the BIGSLEEP issues. And i disagree with the comments @ffmpeg (Kieran) has made about google. From all companies, google has been the most helpfull & nice
Dan Lorenc retweeted

I am the main developer fixing security issues in FFmpeg. I have fixed over 2700 google oss fuzz issues. I have fixed most of the BIGSLEEP issues. And i disagree with the comments @ffmpeg (Kieran) has made about google. From all companies, google has been the most helpfull & nice