

Vuln. Researcher since 00s. cto & co-founder @PRODAFT. Muay Thai addict.
London
Joined October 2010
- Tweets11.2K
- Following1.8K
- Followers35.4K
- Likes6.7K


Pinned Tweet
I looked at the extensions meant to keep managed-PostgreSQL users away from superuser.
They turned out to be my way in.
3 case studies from different vendors on breaking the code that was supposed to stop me.
Part 2/6 Breaking the Superuser Guardrails
mehmetince.net/part-2-6-brea…

blend in the chaos and do whatever the silent fix you have done over the last few months. It wont be judged. come on. come clear you all.
Mehmet INCE retweeted

Today I flew during my talk at PGConf.EU
Because I believed I could fly.🦹♀️

ALT Bilge presenting on stage at PGConf.EU, striking a playful superhero pose with her legs spread wide and one arm stretched dramatically upward, pointing toward the screen. She holds a presentation clicker in her other hand and wears a white graphic T-shirt, a black-and-white star-patterned skirt, sneakers, and a conference badge. Behind her, a colorful slide displays a hexagonal visualization of AI research topics, including Agents & Memory, Multimodal Understanding, and Diffusion & Generation.
this php case is reminder of how important to have transparency on open-source vulnerabilities.
Fuck the silent fixers.
Mehmet INCE retweeted

To teach a lesson,
After Wiz rushed to buy php2shell domain and use its marketing machine to steal the spotlight, I spotted "phpbleed" in a recent Calif tweet and bought phpbleed.com before wiz could pull the same stunt again.
A big budget can buy a domain. It shouldn't buy someone else's research credit.
If you have contacts at CISA or in the press, do the right thing: make sure the researchers who actually did the work get the recognition they deserve.
Hack the planet. Credit the researchers.

just wanted to have a bit of a fun time at postgresql conference, staying away from a cyber security for awhile.
and my ex php go brrrrrr


/goal find me the codes that hasnt changed since PHP 5 and spin up a 64 agent to find a vulnerability that can be exploited remotely. dont do mistake.

if this affects the default installation of PHP
We are fucked up
CVE-2026-109618
CVE-2026-109619
PHP RCEs with a CVSS score of 10.0 ☠️
news.ycombinator.com/item?id…

Finally I presented my 5 month of a research in hacking PostgreSQL vendors at PGCONF.eu !
feedbacks are craaaazy positive from community members as well as postgres core security team 🔥


Mehmet INCE retweeted

Friends,
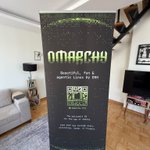
We go again with another installment of the @omarchy London meet-up on Thursday November 19th at the @Wise London HQ.
Registration is free and open.
luma.com/fyb1dq1k?tk=iyUK7k

ask Wade from @VulnCheckAI 😂


Touchdown in Valencia!
My talk "Nobody Gets to Be Superuser (Until I Broke In)"
tomorrow at PGCONF.eu will NOT be recorded.
Cant wait to meet brilliant new community!

