• Irish/Japanese web/AI hacker from Cork, living in Scotland • Founder @StarstrikeAI • BT6 Operator • Newsletter @ https://xitter.cf/t.co/fZXECNnM41
Edinburgh, Scotland
Joined March 2021
- Tweets1.6K
- Following628
- Followers5.7K
- Likes7.3K


Ciarán Cotter retweeted

private keys from 8 intermediate CA certs have been compromised (eMudhra)
Happy "Update everything" day to all my pager-carrying friends
emudhra.we-have-a-problem.co…

I’m liking this recent trend of people outside the bug bounty community calling out the low max bounties of some very large companies.
As someone who got an N/A yesterday because the company decided that my 0-day wasn’t their responsibility, limiting based on N/As is definitely not the right way.

@Bugcrowd is becoming the anti-platform.
Using N/A to calculate accuracy and limit reports is terrible. Soon, many researchers may not be able to submit reports.
How they use N/A:
• Took 20 days + fixed → N/A
• No time to understand → N/A
• Don’t understand scope → N/A

Ciarán Cotter retweeted

I accidentally got addicted to my own game ffs
kosmora.io


🐵 MonkeHacks #101
Cork LHE, Moving, Prompt2Pwn
monke.ie/p/monkehacks-101
#bugbountytips #hacktheplanet #BugBounty
Bug bounty these days is like:
"We regret to inform you that BigStinkyCompany is pausing all submissions until further notice. We're excited to add "subdomain.stinky.com" to our assets after this break, but we're lowering our Medium and Low payouts in line with industry standards"
I wish more tokens were spent on making existing software more efficient instead of generating new slop code
I’ve been strongly considering creating a YouTube channel for MonkeHacks in parallel with the newsletters. I don’t make money on it, so it’s just for fun. And I think it would be nice to have some more resources out there on hacking AI and navigating the bug bounty landscape rn.
Are you feeling lost in the age of AI in bug bounty?
45%Yes
31%No
24%Show results
344 votes • Final resultsThis tree analogy is good

Here's an example from nature that I find fits well. A tree that is 10% taller than its neighbor doesn't just get 10% more light; it secures a multiplier that allows it to grow exponentially faster. So thhe taller tree expands its leaves, captures a disproportionate share of light, and casts a shadow below. The slightly shorter tree receives a fraction of the multiplier (less light), stunts further, and eventually dies from light starvation.
Hacking for the sake of it is what it’s all about

New blog post :) 😊 hacking nethack to get #1 on the leaderboard!
shout out to @7urb01 for being the inspiration
josephthacker.com/hacking/20…

One of the problems with bug bounty is that you can report the most severe bug that the company may ever see in its lifetime and it'll sit in platform triage queues for a few days before the team even sees it
🐵 MonkeHacks #100
Reykjavik, Def Con, Next Steps
monke.ie/p/monkehacks-100
#bugbountytips #hacktheplanet #BugBounty

I'm in Sweden now to unwind after Def Con. Nice 22 degree weather, no more stinky 45 degrees. 3 days of not thinking about hacking or AI and then back to tokenmaxxing 💀
Ciarán Cotter retweeted
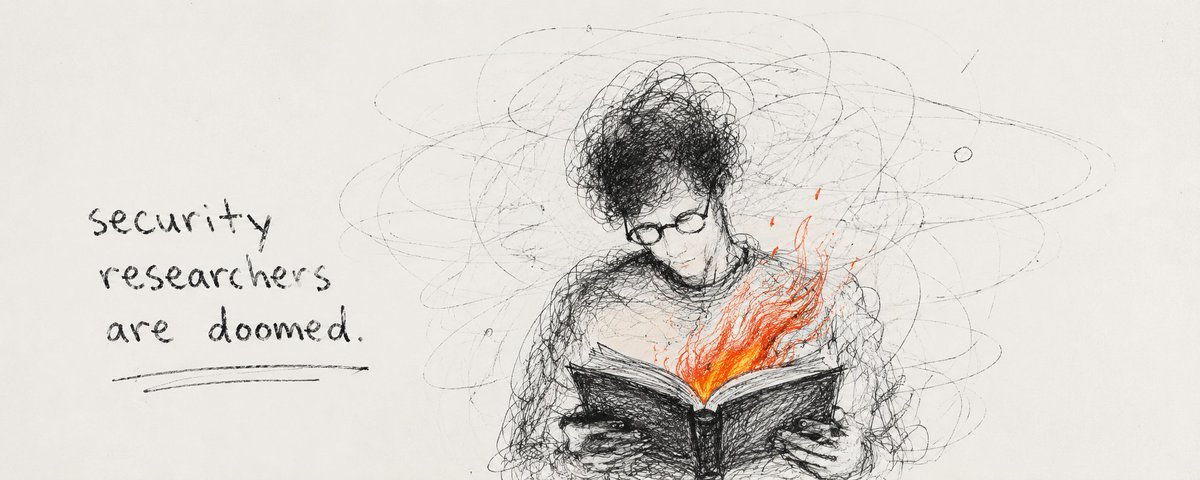
“Security researchers are doomed because of AI.”
I kept hearing versions of this, so I went back through 500 years of people saying the same thing every time a machine learned a human skill.
Some were idiots.
Some were right.
Here’s where I landed.