

Designing the foundations of web3. My blueprints are code, my materials are innovation. Building cathedrals in cyberspace.
Joined January 2021
- Tweets360
- Following3.6K
- Followers2.9K
- Likes63


moon lee retweeted

The MyDoge team have been grinding relentlessly for many moon-moons on their upgraded self-custodial wallet 🔥 Thanks for being an awesome part of the Dogecoin Ecosystem & Community for half a decade!

MyDoge V3 Beta has officially ended.
Final tweaks are underway before V3 heads to the app stores for official launch.
Our beta squad really put V3 through it. Bugs were found, bugs were squashed, feedback kept coming, devs did their thing.
Thank you for helping us get V3 ready for the rest of the Doge community 💛
This is only the beginning.
moon lee retweeted

Gm Y'all
Its been more than 24 hours since the G.O.A.T retired from internationals super emotional but it is what it is.
Forever #MessiArgentina 🐐🫶


moon lee retweeted

wild stuff

There's some confusion about what, exactly, was exploited here.
I've seen claims that this was a long-standing bug, exploited after the "fix" was pushed to the open source repo but before that fix could be rolled out in production.
That does not appear to be true.
Instead, it seems that the fix *was* deployed, but inadvertently introduced a new bug which was subsequently exploited.
Most of the network was still running official releases, none of which contain the new bug. Those nodes correctly rejected the block containing the exploit and stalled at height 4050335.
The timeline is roughly as follows:
• 2016-07-12: Range proof caching added
• 2017-11-08: Range proofs extended to support assets
• 2019-03-19: Range proof cache key "simplified", dropping asset & script fields. introduces Bug A.
• 2026-09-01: Bug A "fixed" by extending cache key to include asset + script. introduces Bug B.
• 2026-09-06: Bug B exploited, reserves drained, chain split.
The original "Bug A" allows some limited cache poisoning because the cache key doesn't commit to the asset and script, allowing a cached result for a range proof for one asset to be applied to a different asset or context.
Exploiting this in practice looks quite difficult, since the amount must match the primer and the proof must be genuine.
The 2026 "fix" added those missing fields to the cache key, producing a format like:
"proof | amount | asset | scriptpubkey"
But this unfortunately made the key easier to manipulate and exploit:
The four fields are concatenated without separators or length indicators.
Since both the proof and the scriptpubkey are variable length, an attacker can stretch the proof and shrink the script to produce the exact same cache key from different proofs, amounts, assets and scripts.
This lets an attacker smuggle arbitrary confidential output amounts and junk proofs past the range proof checker without proper validation, which breaks the guarantees that prevent hidden inflation.
On-chain evidence suggests that this second bug is what was exploited:
Two primer transactions each created an op_return with carefully constructed scriptpubkey and valid range proof for a (presumably) zero value output.
blockstream.info/liquid/tx/2…
blockstream.info/liquid/tx/7…
This produced a cache key like:
" | | | OP_RETURN OP_RETURN"
The exploit transaction then created a large negative op_return output with an invalid range proof:
blockstream.info/liquid/tx/f…
The invalid proof is padded with bytes corresponding to the primer's valid amount and asset fields, aligning the actual amount and asset fields with the same bytes from the primer's opreturn payload:
" OP_RETURN | | | OP_RETURN"
The exploit transaction could then include a second output crediting the attacker with a large positive value, balanced out by the fake negative amount.
Because the success was already cached, the invalid proof was never actually checked and the transaction was accepted as valid by nodes running versions of the software vulnerable to bug B.
Although the amounts are blinded, this is the only output with an invalid range proof anywhere in the peg-out's recent ancestry, so this must be where the inflated coins were created.
And since the padding only produces a cacheable key under the new format, it must have been the newer bug that was exploited.

moon lee retweeted

The tricks can’t wait! UCL Final Kick Off Show presented by PEPSI, May 30th 2026 #Pepsikickoffshow
moon lee retweeted
Real talk
If you’re on the wrong side during a big move like this, most of your immediate impulses are gonna suck
Greatest hits:
1. Revenge short - Can’t believe I missed this piece of shit scam pumping; it’s up so much it HAS to come down
2. Oversized buy - I will use leverage as a time travel machine to make up for being late
3. TA cope - It has to retest the exact level it broke out from immediately because I watched two whole Babypips videos on 1.5x speed
4. All-or-nothing - My only options are 0%. exposure or 100%, nothing in between exists
5. Deer in headlights - oh geez I guess I should wait for a pullback but no what if the consolidation is the pullback hmm maybe I’ll wait for a range to form but what if that range breaks down do I buy the retest of the breakout or the range reclaim oh man fuck shit what’s Ansem saying
6. Overtrader - I will cement my bloodline on the 5 minute chart; if this next candle is the wrong colour I will either be rich or poor
Just chill out, delete your levels, pretend you haven’t looked at the chart in weeks - fresh eyes
Then it’s the usual list of simple questions:
1. What signals are firing / what do I think is gonna happen
2. What kind of bet am I making (mean reversion/volatility expansion/new trend/momentum/Blackrock scam etc.) and on what time horizon
3. Where am I wrong
4. Does my position size match the current volatility and align with the shape of my trade idea i.e. points 1-3
FWIW I’m washed but gonna try to jam some spot sub 70k. If it gets accepted below 66-67k (retraces the breakout) then I’ll lose money
“Wow it’s up so much what you buy the top?”
Then I’ll lose money and look silly on social media. That’s the cost of doing business (at least the first one).
Just start LARPing like everyone else and instead of saying “I bought the top” say “I aggressively rebalanced when an ensemble of carefully weighed momentum factor signals fired contemporaneously.”
moon lee retweeted

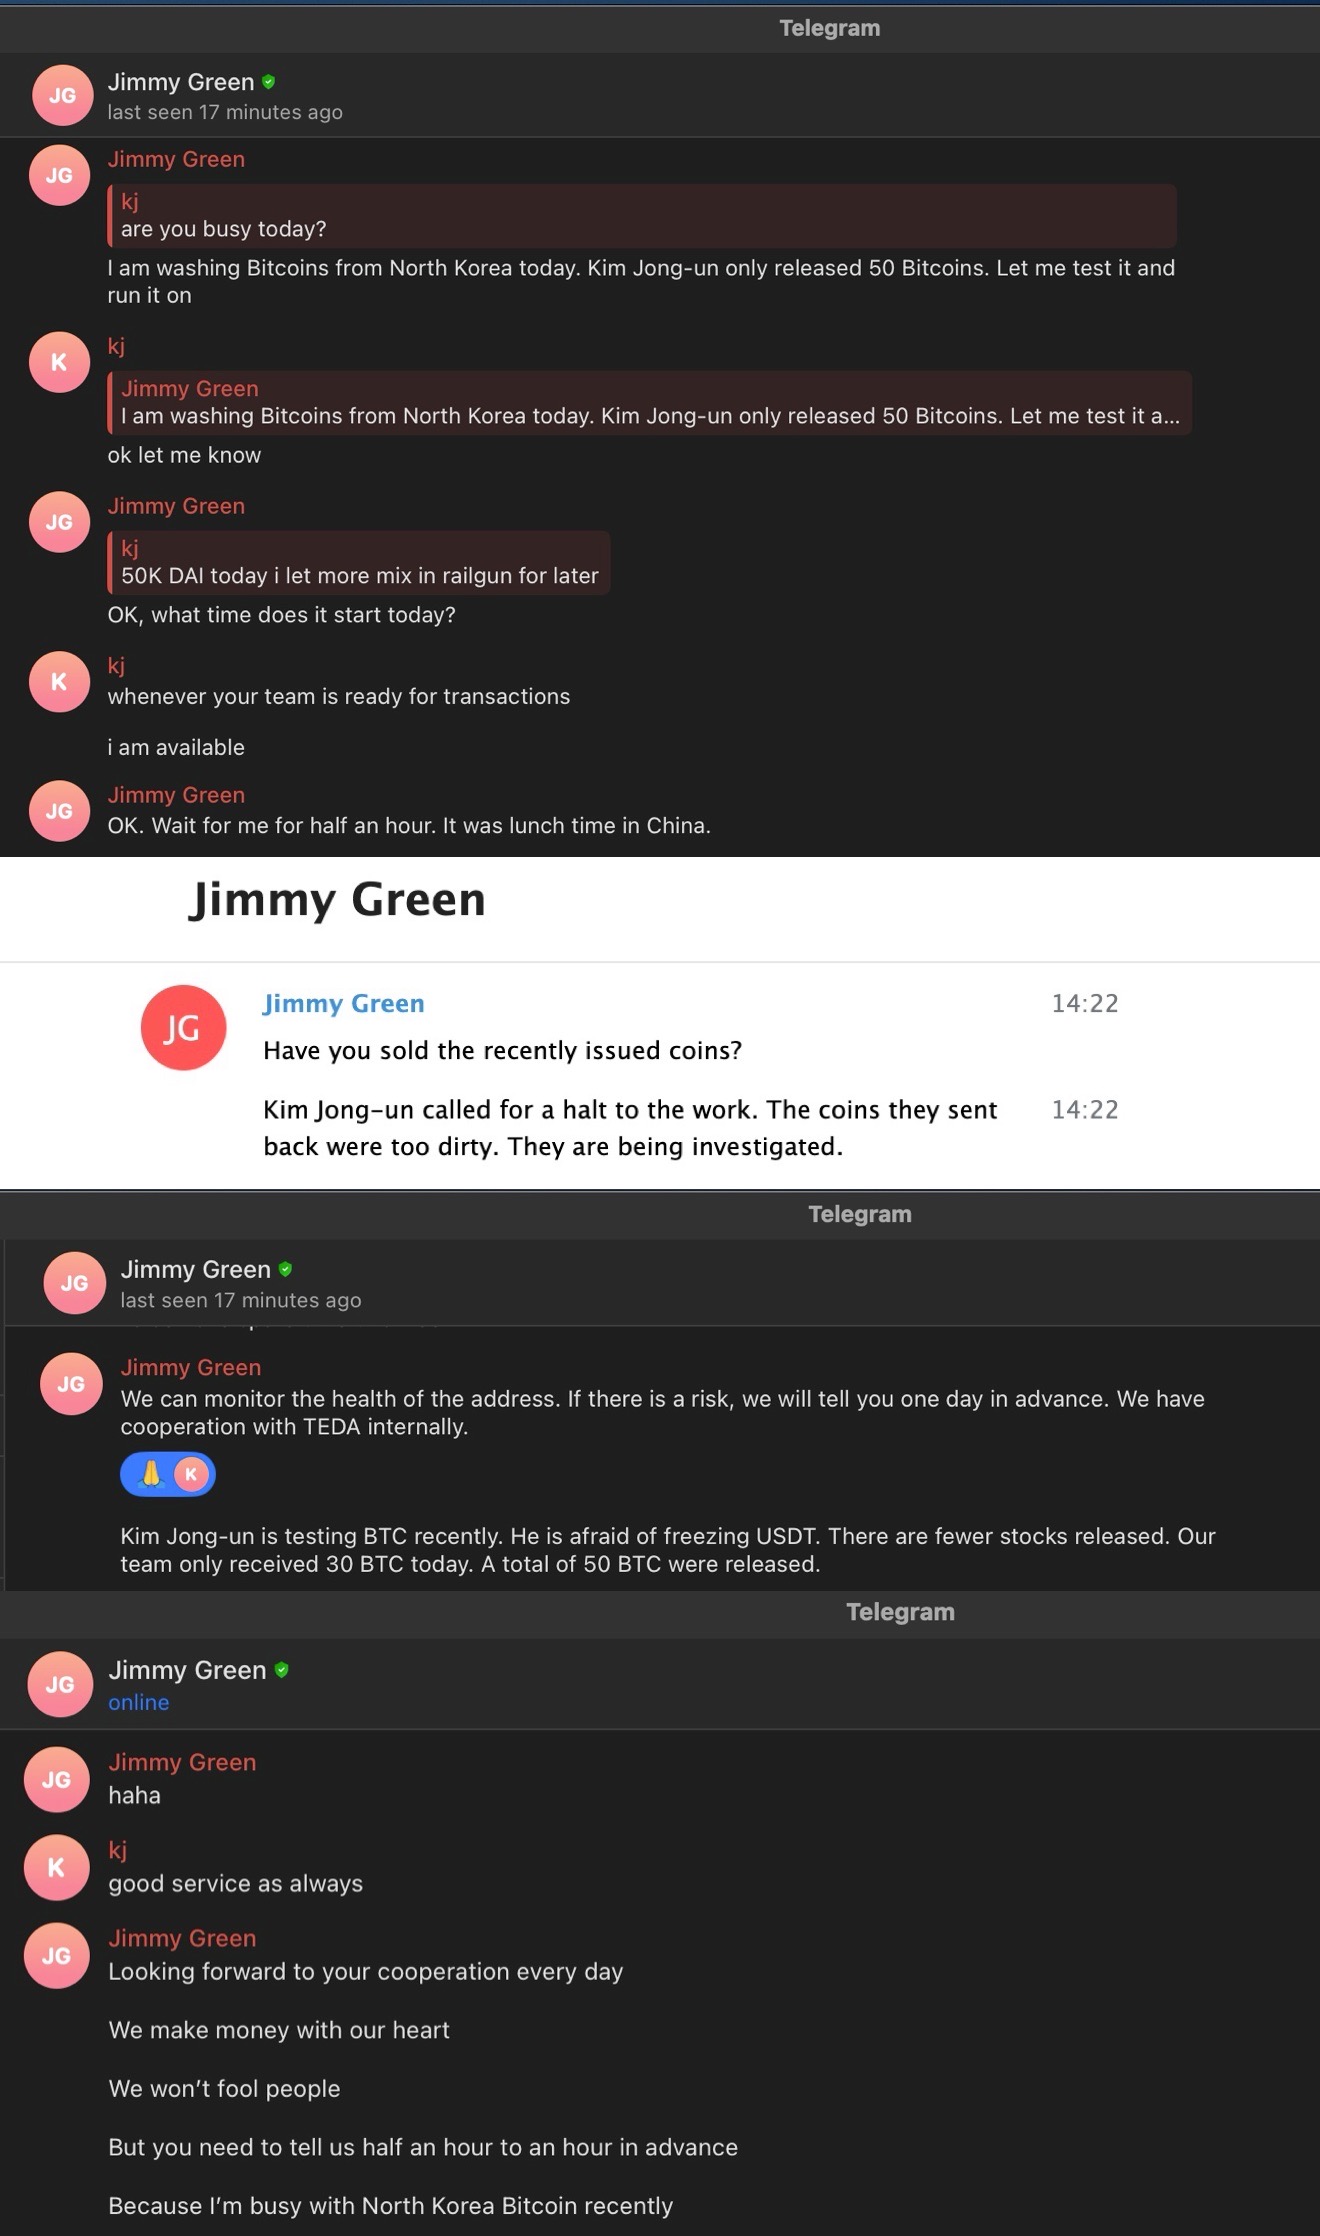
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

moon lee retweeted

🇺🇸 JUST IN: Mike Selig says the CFTC will apply established derivatives margin models and controls to crypto, warning there will be “no race to the bottom on leverage.”




moon lee retweeted
A huge milestone for Dogecoin. Builder shibes! The DogeOS test net is waiting for you!
Other cryptos coming off of a down market cat nap * and dogecoin out making moves to be the only currency the world needs. And you can be part of it. Take a l@@k.

moon lee retweeted
The Hillhead Baptist Church in Glasgow, built in 1883, is not an extraordinary historical building.
It's a typical and relatively plain neoclassical (using the word colloquially) church, made of stone.
But it's still rather pretty and it's been around for a very long time.


moon lee retweeted

If I had 6 months to learn trading, here's how I would split my time:
Technical Analysis: 1 week
Risk Management: 2 weeks
Trade Journaling: 3 weeks
Strategy Development: 4 weeks
Live Trading and Scaling: 14 weeks
New traders, I've seen this work more than anything else.
moon lee retweeted
Better Marxists hate crypto because they hate individual freedom and self-sovereignty. They want to control you and your money. They are anti-innovation and anti-American and that’s why they will lose and we will win. Onward! 🇺🇸

Wild statement from @BetterMarkets following today’s CFTC action re: proposed regulatory framework for crypto exchanges…
“The US is not the cocaine production capital of the world, and no one is complaining - for good reason. Crypto - after 18 years of effort and innumerable disproved and baseless claims - still lacks any real-world use case. It is used either purely for speculation or for criminal purposes.”
Might want to talk to NYSE, Nasdaq, DTCC, & all the other major market participants currently building in the space.
Industry is simply wanting rules of the road for crypto.
If politicians can’t provide them, then it looks like the CFTC & SEC will have to.
