

Author of #PingCastle, contributor to #mimikatz (DCSync, setntlm, DCShadow) and #OpenSC. Wrote GIDS applet, OpenPGP card driver on Windows and OpenSC stuff.
France
Joined July 2016
- Tweets1.4K
- Following58
- Followers11.5K
- Likes910





Pinned Tweet
I just released EIDVirtual v2! 🚀
Get a virtual smart card reader that uses a real USB drive for free. It automatically simulates a GIDS applet to manage your certificates—a perfect alternative to TPM-based MS Virtual Smart Cards.
Check it out here 👇 mysmartlogon.com/download#EI…

Looks simple. It really isn't.
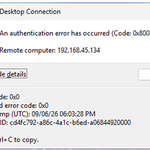
Non-domain joined + latest Win11 build. Negoex + Kernel SSP.
Pretty proud of this result ⬇️


It's when NegoEx keys are queried and not ready yet. Error code must be STATUS_NOT_FOUND. Any other error is reported to the client. STATUS_OK with an empty key force the recomputation of the key, triggering MIC mismatch in credSSP paquet.

Spent 2 days solving: AES256+RSAES_OAEP(RSA:CNG) test FAILED: Cannot find the certificate and
private key to use for decryption. 0x8009200c (-2146885620 CRYPT_E_NO_DECRYPT_CERT)
Full story here: mysmartlogon.com/knowledge-b…
In short: a problem with the serial number of the certificate

J’ai loué un Airbnb pendant mes travaux. Je suis tombé sur un propriétaire qui comptait remettre à neuf son bien. Il réclamait 10.000€ et Airbnb l’a payé 7500€. Puis Airbnb s’est retourné contre nous.
Demande finalement annulée en appel mais il a toujours l’argent


My daughter just invented a universal power plug with this usb cable.
She tried to power on a computer and a printer
(Spoiler: it doesn’t work)

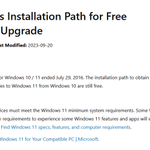
I just discovered that Microsoft is a $#!@ after having to reinstall my Windows after the "free" Windows 10 & Windows 11 upgrade from my Windows 7 box license:
devicepartner.microsoft.com/…
Beware that the "free upgrade" from Windows 10 to Windows 11 is just the same mirage.

Vincent Le Toux (Paris, France) retweeted
Join me on Tuesday, September 16th at 5PM Paris time (11AM New York / 8AM Los Angeles) for a special Ask Me Anything session!
Topics: PingCastle, Incident response, ...
The event will be hosted on the Netwrix Community.
Link: community.netwrix.com/t/ama-…

Join me on Tuesday, September 16th at 5PM Paris time (11AM New York / 8AM Los Angeles) for a special Ask Me Anything session!
Topics: PingCastle, Incident response, ...
The event will be hosted on the Netwrix Community.
Link: community.netwrix.com/t/ama-…
Big change at #PingCastle !
The release cycle is changing from "every 6 months" to a "new features" based cycle.
No more rush to issue a release with limited tests just to stick to the schedule.
See below for the full message, available at github.com/netwrix/pingcastl…

Vincent Le Toux (Paris, France) retweeted

New blog post: Tear Down The Castle - Part 2
dfir.ch/posts/tear_down_cast…
I analyzed 250 PingCastle Reports, grouping the findings along the categories I used for my 10 AD Commandments series.
The number of affected domains is stated within each finding, i.e., in how many domains we found the misconfiguration or the vulnerability.


I’m thrilled to be part of the Netwrix webinar series, Securing Active Directory: From Risk Mitigation to Incident Response.
I’ll make a live demo & you get the opportunity to ask me questions.
November 20 & 21
Registration link: netwrix.com/securing-active-…

Vincent Le Toux (Paris, France) retweeted

In our search for new forensic artifacts at @ExaTrack, we sometimes deep dive into Windows Internals.
This one is about COM and interacting with remote objects using a custom python LRPC Client.
STUBborn: Activate and call DCOM objects without proxy: blog.exatrack.com/STUBborn/
Vincent Le Toux (Paris, France) retweeted
FortiManager cases are incoming. We see the exact same TTPs as outlined by Mandiant in their blog post [1].
"Once the threat actor successfully exploited the FortiManager, their unknown Fortinet device appeared in the FortiManager console."
And, most importantly:
"Organizations that may have their FortiManager exposed to the internet should conduct a forensic investigation immediately."
Do it now! ⏰
[1] cloud.google.com/blog/topics…

I’m banned from @Apple for no reason. Just spent 10 minutes on apple support with a human robot just repeating to me “use another email”. Astonishing.


15 days to get ‘please open a support ticket.’ Does Apple hire robots? 🤖
My response: formal GDPR request via registered letter. 📬
Note: You practically need a law degree to figure out who handles your private data. 🕵️♂️


