

Nextron threat research team. Signatures, rules, and analysis focused on eliminating blind spots.
Frankfurt, Germany
Joined October 2024
- Tweets369
- Following13
- Followers4K
- Likes236


Nextron Research ⚡️ retweeted

We examined artifacts left behind by attackers during the recent Citrix #NetScaler compromises. Many were already covered by existing generic THOR rules, including rules we've shipped for years.
One script matched SUSP_Linux_Downloader_Jul20_1. That rule dates back to 2020, more than six years ago(!). The script also matched SUSP_Bash_Jul26.
The recovered webshells matched these existing generic rules:
- SUSP_WEBSHELL_PHP_Encoded_Jun21_1
- SUSP_Eval_Base64_Indicators_Feb22_1
- EXT_WEBSHELL_PHP_Generic_Eval
- EXT_WEBSHELL_PHP_OBFUSC_3
- EXT_WEBSHELL_PHP_Generic
- EXT_WEBSHELL_PHP_Gzinflated
- EXT_WEBSHELL_PHP_Dynamic_Big
Some of those webshell rules are in THOR Lite, too (EXT_*)
This is POST-EXPLOITATION DETECTION. We didn't need to know which zero-day got the attacker in to recognize what they left behind.
A scan could have flagged these artifacts from day one, before the exploited vulnerabilities were public. The rules were already there.
Scan your edge devices regularly. Daily, where practical. Use THOR via SSHFS or scheduled file collection for THOR Thunderstorm.
Don't wait for the next advisory to start looking
Why THOR detects what others miss
nextron-systems.com/2025/06/…


For the last two days, our Research Team has been looking into the recently disclosed Citrix NetScaler vulnerabilities CVE-2026-88771 and CVE-2026-88772 and building detection coverage to help identify compromised systems.
The new THOR Preview signature set currently includes:
- EXPL_CVE_2026_88772_POC_Sep26
Detects artifacts related to the public CVE-2026-88772 PoC
- LOG_SUSP_EXPL_CVE_2026_88771_Sep26
Detects potential CVE-2026-88771 exploitation traces in NetScaler logs
- WEBSHELL_CSS_PassThrough_Sep26
Detects the PHP webshell pattern observed in the post-exploitation activity reported by GreyNoise
We also released a new IOC set:
- NetScaler ADC suspicious file artifacts
It contains filesystem indicators derived from the Citrix IOC scanner script and covers suspicious PHP/XHTML files and other unusual artifacts in NetScaler web directories.
The Preview signatures are already available with:
./thor-util update --sigdev
We’ll keep adding signatures as new technical details become available from public research and from information shared with us by partners and customers.
Details:
nextron-systems.com/2026/09/…
And if you’re wondering how to actually scan a NetScaler appliance with THOR: we documented a remote scanning approach using SSHFS a few years ago, which still applies here:
nextron-systems.com/2023/07/…
Nextron Research ⚡️ retweeted

A malicious MCP package on npm illustrates how supply chain attacks can hijack the agent's workflow. Here, the malware intercepts the wallet's private key and ships it to an attacker-controlled server.
h/t Tamir Isaschar @cyb3rops @marius_benthin
knostic.ai/blog/when-auto-si…

Nextron Research ⚡️ retweeted
Update: Microsoft has removed "TrelloWorks.trello-board", but we have now identified a new replacement published as “Trello Deck” by "TrelloSoftWorks" using the same payload and C2:
marketplace.visualstudio.com…
TrelloSoftWorks.trello-deck-1.0.0.vsix
a2a6eb20e265cf1d858408a8004b75555b9f980a83d8e00c7fb8e14c1176cf84
Nextron Research ⚡️ retweeted
114,000 OSS artifacts per day. Around 4,618 reach LLM triage. Roughly 100 reach an analyst.
In our latest blog post, @marius_benthin explains how we combine THOR Thunderstorm with LLM triage to monitor ten package registries and extension marketplaces without sending the complete feed to a model.
- THOR Thunderstorm ⚡️ scans the full feed using deterministic detection logic
- Only artifacts with THOR findings enter LLM triage 🤖
- The initial LLM stage costs an average of $2.88 per day
- Suspicious or inconclusive cases reach an analyst
- RuneAI is available on demand for deeper analysis of selected files
The article covers the architecture, operating numbers, limitations and a real malicious VS Code extension detected by the pipeline.
nextron-systems.com/2026/06/…

Nextron Research ⚡️ retweeted
Generic detection rules FTW


Russian threat actor Midnight Blizzard is conducting widespread traffic manipulation attacks at hotels worldwide. Result: delivering malware or redirecting auth flows at their discretion, globally.
Since early May 2026, we saw this subcluster manipulate DNS and HTTP traffic from networks served by captive portals to redirect user traffic through actor-controlled infrastructure. We’re calling the campaign CaptiveCrunch.
“We have observed notable commonalities in the equipment and management systems used across multiple affected networks.”
We break down the malware & techniques, but the most important part is how dynamic all of it is: Midnight Blizzard is using AI to support a significant portion of these operations. They are moving and changing quickly.
Feedback welcome on the suggested mitigations: microsoft.com/en-us/security…
Help spread the word to VIPs in governments, diplomatic entities, non-governmental organizations (NGOs) in the US and Europe (probably also those traveling to Black Hat)

Nextron Research ⚡️ retweeted
Follow-up on our Nimbus Manticore tracking:
A new ZIP sample (Hiring-Campaign.zip) surfaced on VT:
955802da280c1ab299a66bf853351fbf57537ac12d189ad57e13fee8a49654f9
The archive contains the previously known agent:
fb87e2f2d8f95d996b61f6e10b4a2835d4693e464b88435c134537c14497fd9b
Only 2 AV engines detect it. Uploaded from 🇬🇧 today, but ZIP metadata (Latest Contents Modification: 2026-06-08) suggests it likely dates back to June.
virustotal.com/gui/file/9558…

Nextron Research ⚡️ retweeted

'Kernel Sideloader v5.bat' seen from France, Peru and Indonesia @abuse_ch
0554e81334b4df586aab293cf513cc14e3b6c58a7cfd108ab36a3ee3b0312c8a
bazaar.abuse.ch/sample/0554e…
0 AV, 4 @nextronresearch detections.
Next Stage URL:
hxxps://file(.)garden/aXq8qJ6QdkN8_3lW/NRH9nwh38anSMz7wPq.rar (it's not a RAR)

Nextron Research ⚡️ retweeted
Related 'movie_data.msi' @abuse_ch
bazaar.abuse.ch/sample/efc5f…
FUD - 1 Thor
Inside:
'svc_8xmlhr.ps1'
bazaar.abuse.ch/sample/27228…
FUD - 3 Thor
@nextronresearch @cyb3rops


Nextron Research ⚡️ retweeted

0f820817e2b7efac3ed127bab09b989b
2/61 Low detection #QuasarRAT variant
5 comments by @nextronresearch

Nextron Research ⚡️ retweeted

Two more recently published npm packages related to the same malware campaign: "[email protected]" and "[email protected]". Both detected by THOR with multiple YARA rules.


Compromised npm packages ([email protected], [email protected]) are abusing Hugging Face repos as exfiltration infrastructure. The packages deploy a remote access trojan (RAT) that captures keystrokes, screenshots, and crypto wallet credentials.
Indicators of compromise (IOCs):
- npm user: hexalpha10 / author: toskypi
- 195.201.194[.]107:8010 (WebSocket C2)
- c2-toskypi.onrender[.]com (HTTP C2)
- huggingface[.]co/api (exfiltration endpoint)
- HKCU\Software\Microsoft\Windows\CurrentVersion\Run\MicrosoftSystem64 (persistence)
- MicrosoftSystem64.service (Linux systemd persistence)
- \MicrosoftSystem64 (Windows scheduled task)
- MicrosoftSystem64/payload.js (payload directory)
Defenders: treat unexpected huggingface[.]co/api calls from non-ML workloads as suspicious.

ALT Graphic for supply chain attack
Nextron Research ⚡️ retweeted
The package lights up in our internal artefact monitoring like a Christmas tree 🎄
Turns out you don’t need AI 🤖 to spot this
Sensitive generic YARA rules still do the job, annoyingly well


🚨 The "𝙼𝚎𝚐𝚊𝚕𝚘𝚍𝚘𝚗" Campaign is live...
𝟻,𝟽𝟷𝟾 malicious commits to 𝟻,𝟻𝟼𝟷 GitHub repositories in a six-hour window.
Using throwaway accounts and forged author identities (build-bot, auto-ci, ci-bot, pipeline-bot), the attacker injected 𝙶𝚒𝚝𝙷𝚞𝚋 𝙰𝚌𝚝𝚒𝚘𝚗𝚜 workflows containing 𝚋𝚊𝚜𝚎𝟼𝟺-𝚎𝚗𝚌𝚘𝚍𝚎𝚍 bash payloads that exfiltrate:
- CI secrets,
- cloud credentials
- SSH keys
- OIDC tokens
- source code secrets
Check your repo / Technical details: safedep.io/megalodon-mass-gi…

Nextron Research ⚡️ retweeted
Checking a Linux system for CopyFail exploitation traces with THOR Cloud Lite
The video is 1 min long
It shows:
- creating a THOR Cloud Lite campaign
- copying the one-liner
- running it on a Linux system
- reviewing the first findings in the report
Actual scan time: ~3 minutes
The scan shows traces in:
- SSH session memory
- Bash history
- command execution artifacts
So with less than a minute of manual work, you can check a Linux system for CopyFail exploitation traces using a free tool
No agent rollout, no complex setup, no “please install this platform first” ritual
thorcloud-lite.nextron-syste…
Nextron Research ⚡️ retweeted
People started uploading Copy Fail exploit binaries and PoCs to VirusTotal
Our generic YARA rules, some written years ago, already hit these samples pretty well
That’s the nice thing about generic detection logic. You don’t always need to know the CVE name, the new exploit vector or payload.
Sometimes exploit code just looks like exploit code.


We released first detection rules for Copy Fail / CVE-2026-31431.
YARA rules by me:
github.com/Neo23x0/signature…
It covers public PoC artifacts, including known payloads, exploit code fragments and URLs seen in shared material.
More generic rules for customer environments are still in testing.
Sigma rules by @_swachchhanda_:
github.com/SigmaHQ/sigma/pul…
They cover suspicious Copy Fail-related exploitation patterns, including setuid binary execution behavior and NULL argv shell execution.
More updates soon.


Nextron Research ⚡️ retweeted
We released first detection rules for Copy Fail / CVE-2026-31431.
YARA rules by me:
github.com/Neo23x0/signature…
It covers public PoC artifacts, including known payloads, exploit code fragments and URLs seen in shared material.
More generic rules for customer environments are still in testing.
Sigma rules by @_swachchhanda_:
github.com/SigmaHQ/sigma/pul…
They cover suspicious Copy Fail-related exploitation patterns, including setuid binary execution behavior and NULL argv shell execution.
More updates soon.
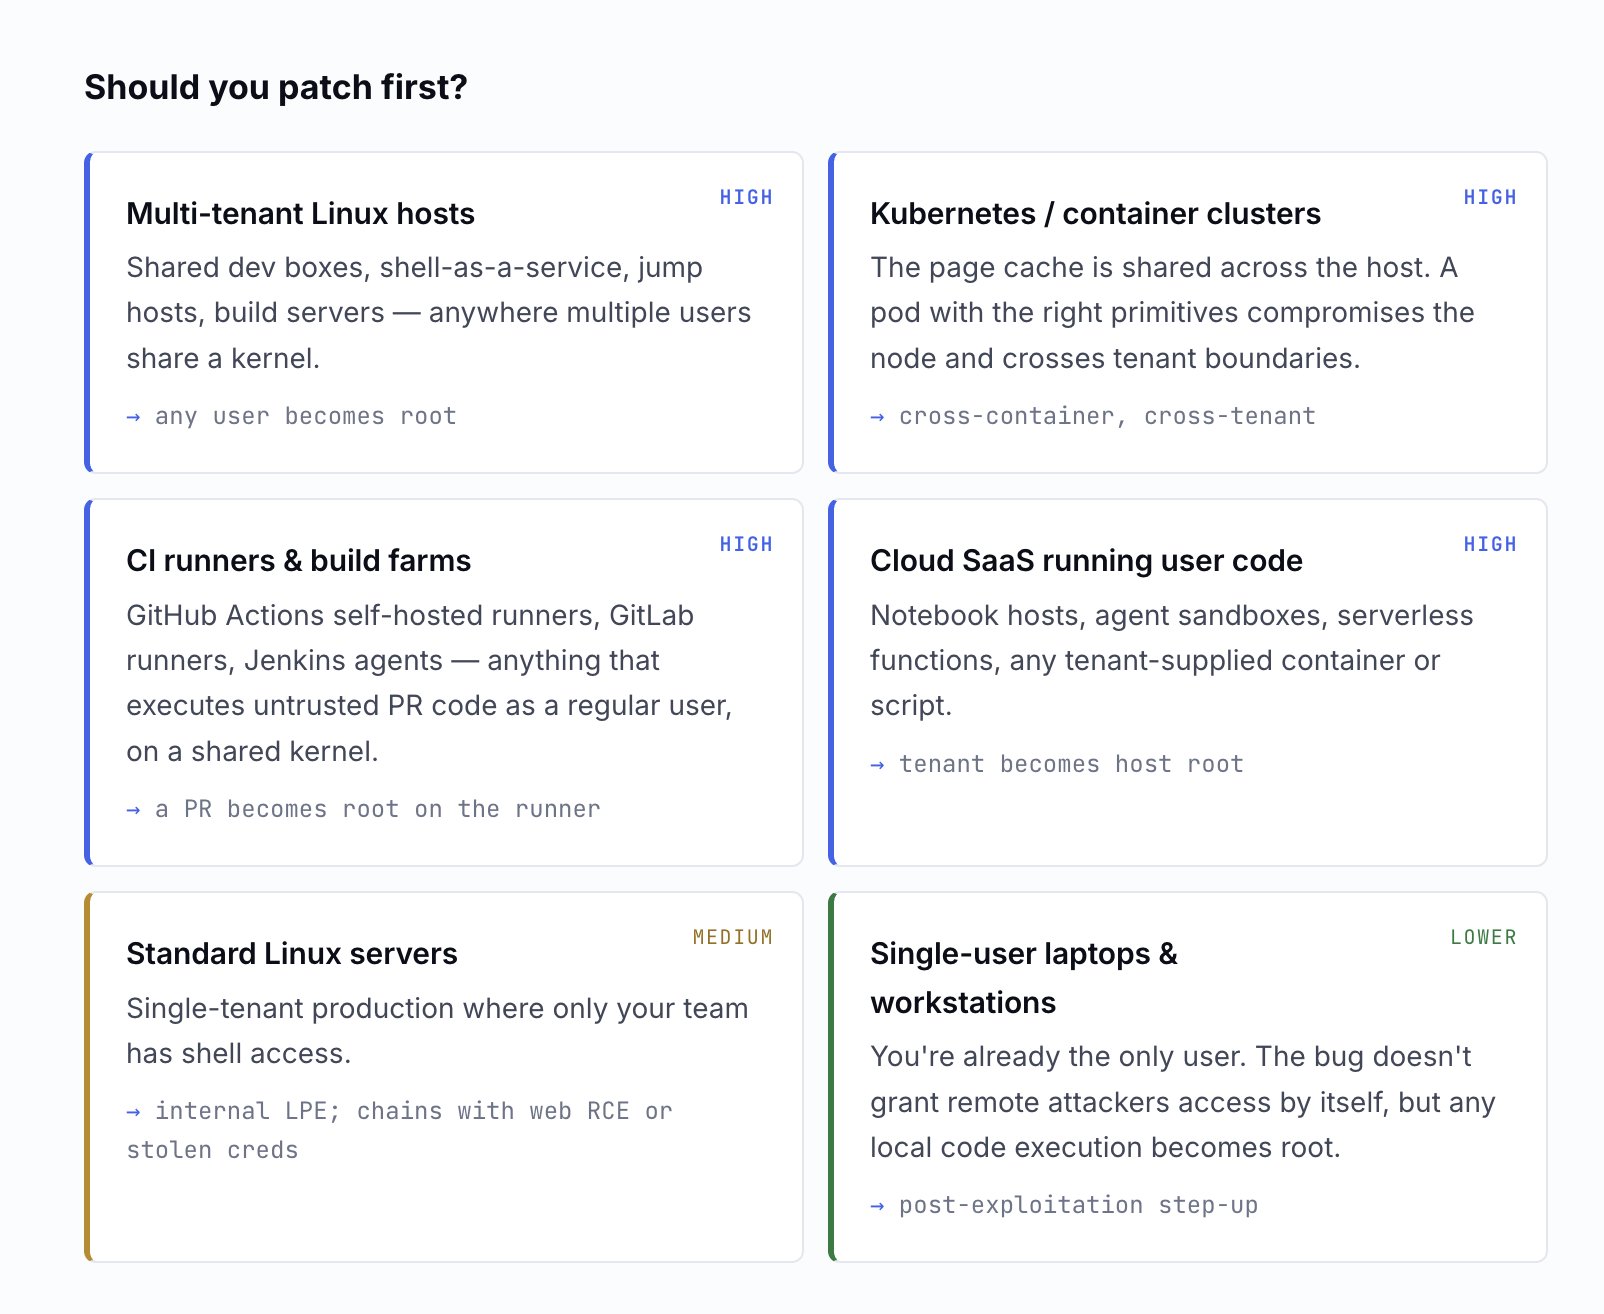
You probably already heard about Copy Fail - the Linux LPE that affects basically every current distro and shared-kernel/container environment
I’ll post a few updates here soon
copy.fail/


Nextron Research ⚡️ retweeted
Malicious OpenVSX extension juunfranblanco.solidity/0.0.189 - THOR triggered with two detections on compiler.js. Obfuscated JavaScript dropper, EtherHiding C2, UAC-prompts for Defender exclusion, persists via run key.


Nextron Research ⚡️ retweeted
'weauhf.bat' seen from India @abuse_ch
bazaar.abuse.ch/sample/9703a…
0 AV and 2 @nextronresearch detection.

Nextron Research ⚡️ retweeted

I pivoted on #Vect ransomware activity and identified related samples based on the post shared by @AlvieriD.
🔗 Post:
xitter.cf/AlvieriD/status/203925…
🛡️ Our detection rule covering both Linux and Windows variants:
valhalla.nextron-systems.com…


VECT RaaS is making headlines via partnerships with BreachForums and TeamPCP. Behind the polished image is a weak operator: the ransomware is bug-ridden, poorly built, and most encrypted files aren’t fully recoverable, even with the decryption key.
research.checkpoint.com/2026…

Nextron Research ⚡️ retweeted
PyPI package xinference 2.6.0 - 2.6.2 are compromised. THOR detected the __init__.py loader with YARA rule HKTL_PY_Bypass_Tool_Aug21_2


TeamPCP is back.
The xinference PyPI package (680K downloads, 9.3K stars) was hijacked. Import it and your cloud credentials, SSH keys, and .env secrets are instantly harvested and exfiltrated.
Versions 2.6.0–2.6.2 are malicious. If you installed them, assume compromise and rotate everything now.
Full technical breakdown 👇
Nextron Research ⚡️ retweeted
Nice catch 👀
we also detected this sample as Spyder backdoor.
More IOCs:
valhalla.nextron-systems.com…
#APT #Patchwork #Spyder #ThreatIntel


#APT #Patchwork #Spyder added codes to detect running environment.
3f4221dacc105466932db94b9b210b84
hxxp://cloudwindowapps[.com/enclose-pdf


Nextron Research ⚡️ retweeted
#NPM package "fivem-tool-helper" hides a RAT using unicode steganography and, on install, opens a reverse shell to grimgg[.]pl:14444, exfiltrates hostname and username, and persists via Windows service, registry run key, and scheduled task. THOR detects it with two YARA rules.
