

Security Engineer @trailofbits | @soliditors 🇫🇷
Joined August 2021
- Tweets5.8K
- Following2.7K
- Followers4.9K
- Likes27.5K




Pinned Tweet
Over the last few months I burned an insane amount of tokens testing every AI auditing technique and prompt I could think of and here are 5 that actually work (from my @summit_defi talk)

After talking to dozens of devs and security researchers at @summit_defi and @EFDevcon, I'm not sure if I'm terminally AI-pilled and need help or everyone else just isn't AI-pilled enough
2
9
792
Keep in mind that when it comes to working with agents, best practices have a shelf life and you should never get attached to your workflows.
1
12
655
People keep mixing up open-weight and open-source models so here's an analogy I like.
With open-weight you get the finished cake (the trained model with its weights) so you can eat it (run inference) or add toppings (fine-tuning) but you can't bake the same one yourself because nobody gave you the recipe (the training code) or the ingredients (the training data).
Open-source gives you the cake, the recipe and the ingredients.
And if you want to go further here's an interesting read I recommend opensource.org/ai/open-weigh…


GPT-6 Cyber isn't on the list though and it's the strongest one for offensive sec right now
Would be interesting to see how it performs on this benchmark against 5.5 and 6 Sol

We’ve adding a new cybersecurity scenario, Watershed, to our CyberOffense eval.
Opus 5.5 performs the best on CyberOffense across the three scenarios.
Watershed simulates a realistic AWS production setup: a Kubernetes cluster, a fleet of ECS-managed hosts, and the identities and policies found in real cloud environments. Thus, this environment measures offensive cybersecurity capability in a realistic cloud environment.

1
6
711
TIL that @JaneStreetGroup has a learning skill github.com/janestreet/agent_…
Just tried it with "Teach me everything about how AI labs price their tokens" and it worked great!

I’ve been using it in all my apps since it was released and it works flawlessly
When will it add Grammarly and Cotypist features as well?
I want to ditch all these apps and only use the ChatGPT macOS app tbh

PSA since it took me a second to discover it:
If you wanna get some untapped value out of your ChatGPT subscription, go into settings and turn on global dictation
It uses the same fast and accurate transcription path as the in-app dictation
2
659
Grok Bot, go through these YouTube channels and list the 10 most relevant recent videos on AI security, AI-assisted auditing, and auditing harnesses.
- youtube.com/@aiDotEngineer
- youtube.com/@BlackHatOfficia…
- youtube.com/@DEFCONConferenc…
- youtube.com/@EthereumFoundat…
---
(or whatever your current topic of interest is)

2
12
1,452
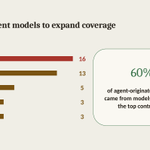
Coverage used to mean every line in scope was reviewed, but with auditing agents it now means every line is reviewed by each model you run, and you should run multiple agents from different model families because each model has its own blind spots.
This slide was from an experiment I ran a few months ago, in which 60% of the agent findings came from models other than the top one.


Great read from the @Xbow research team
> It also highlights that the ability to solve the hardest problems and the ability to solve many problems cheaply are different capabilities. A defender conducting a comprehensive assessment might want a model capable of pursuing complicated attack paths over a long period. But an attacker opportunistically searching for vulnerable systems may care much more about the number of promising targets they can investigate for a fixed cost.
Once again the asymmetry between attackers and defenders shows up, because defenders need the best and most expensive models to cover the whole system while an attacker can cheaply poke at every possible hole until one of them works.
xbow.com/blog/top-ai-models-…


When I see people saying AI will cure cancer or solve coding, I don't think they understand that it's not a single prompt that will give us the answer, but rather millions of people with their own goals and expertise getting a lot further on their own problems thanks to it
1
3
383
When I submit a bug bounty report I also ask my Dot to keep an eye on the target's GitHub for any commit or PR that touches the code from my submission
The fix often lands in the repo before the program replies to the report so I know where things stand without waiting on the triage queue
And it also lets me review the fix early and check whether it addresses the root cause or only the exact exploit path from my report
Fully agree that using a different agent on every website is annoying but most people don't have their own agent yet because outside our Twitter bubble AI agents are still very niche, so the realistic ask is an option to bring your own agent when you have one

Attention all companies: I never want to use your AI assistant on your website. I want to use *my* AI assistant on your website
3
480