

Helping security teams optimize vulnerability management workflows through orchestration and automation.
Sarasota, FL
Joined December 2018
- Tweets2.3K
- Following348
- Followers586
- Likes2K




“Let AI write code. Don’t let it pick dependencies alone.”
In Forbes, Nucleus CEO Steve Carter shares why dependency review still matters as AI takes on more of the development process.
Read more: hubs.la/Q04BWFKL0

What are agencies underestimating about BOD 26-04?
Former CISA CIO Bob Costello shares his take in this clip.
On October 27, Bob and Scott Kuffer will break down what BOD 26-04 implementation looks like in practice.
Register: hubs.la/Q04BQyt20
BOD 26-04 may be even more critical today than when it was released.
Bob Costello explains why AI-driven vulnerability discovery is putting pressure on teams to understand where they’re vulnerable and what to prioritize.
Join Bob and Scott on Oct 27: hubs.la/Q04Bj4Fp0
What questions should agencies be asking about BOD 26-04?
Bob Costello previews a few he’ll be asking Scott Kuffer live on October 27.
Register for the webinar: hubs.ly/Q04B7lMH0
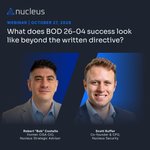
What does BOD 26-04 success look like beyond the written directive?
Join former CISA CIO Robert "Bob" Costello and Nucleus CPO & Co-founder Scott Kuffer on October 27 for a practical discussion on what BOD 26-04 compliance actually takes.
Register today: hubs.la/Q04z8yfz0

One recommendation from the FBI's Operation Winter SHIELD guidance deserves a second look: vulnerability management.
The guidance is clear. The hard part is execution. Steve Carter explains why it remains one of cybersecurity's toughest challenges.
hubs.la/Q04z84qY0

What would a former CISA CIO ask about your BOD 26-04 program?
Join former CISA CIO Robert "Bob" Costello and Nucleus CPO & Co-founder Scott Kuffer on October 27 for a discussion on what BOD 26-04 implementation looks like in practice.
Register today: hubs.la/Q04yDY_b0

The vulnerability was fixed months ago.
The challenge is proving what happened between discovery and remediation.
Doug Drew explains how security teams are automating audit evidence so the timeline is already there when auditors ask for it.
Read more: hubs.la/Q04yqCFf0

BOD 26-04 is here. The hard part is operationalizing it.
Join former CISA CIO Bob Costello and Nucleus CPO & Co-founder Scott Kuffer on Oct. 27 for a practical discussion on implementing BOD 26-04 in the real world.
Register here: hubs.la/Q04y6G8f0

eBook launch: It's here: "From Mandate to Operating Model. A Federal Leader's Guide to CISA BOD 26-04."
The four decision variables explained, what changes at 3/14/60 days, and how to turn a directive into a program you can defend at audit.
hubs.la/Q04xv9m90

AI is accelerating vulnerability discovery. The bottleneck is no longer finding issues, it's fixing them.
Scott Kuffer shares why exposure management must scale beyond manual processes and the thinking behind Nucleus Helix:
hubs.la/Q04x4NDB0
Nucleus Security is heading to Fal.Con 2026.
Join Scott Kuffer on Sept. 2 at 11:15 AM for From Findings to Fixes: Why AI Alone Isn’t Enough, then visit Nucleus at Booth #1513.
Aug. 31–Sept. 2 | Las Vegas
hubs.la/Q04vJKXw0

Trend Micro projects nearly 66,000 CVEs in 2026.
As disclosure volume grows, security teams spend more time deciding which findings matter, who owns them, and how hey move through remediation. Those decisions increasingly define how exposure management programs perform.

Black Kite's latest report narrowed 48,000 published CVEs to 58 genuine supply chain threats.
Prioritization became much more precise by combining exploitability, supply chain context, and threat intelligence rather than relying on a single signal.

For the third consecutive year, Nucleus Security has been named to the Inc. 5000 on the 2026 list of America's fastest growing private companies.
Grateful to our customers and our team for making this possible. Still building.

Nucleus Security has been named in three Gartner Hype Cycles for 2026.
The environments may be different, but the operational work is increasingly the same: understanding exposures, assigning ownership, and moving remediation forward across IT, OT, and industrial networks.

Mythos changed the pace of discovery. It did not change where VM programs break down. Scott Kuffer on why the pressure lands on remediation infrastructure, and what that means for teams already managing six-figure backlogs.
hubs.la/Q04rKf1r0

Scott Kuffer in Last Watchdog's Black Hat roundtable on the Hugging Face breach: the real change is sophistication. A machine discovering new exploitation chains without a pre-programmed path accelerates an existing problem. It doesn't create a new one.
hubs.la/Q04r_0Lv0

Steve Carter in AI Risk Summit: Mythos makes attackers faster. It doesn't change the blast radius of a bad remediation decision. The line between what you automate and what you gate was drawn on reversibility. Mythos raises the stakes on getting it right.
hubs.la/Q04rt_C30

