




nullt3r retweeted

udpx
Fast and lightweight, UDPX is a single-packet UDP scanner written in Go that supports the discovery of over 45 services with the ability to add custom ones. It is easy to use and portable, and can be run on Linux, Mac OS, and Windows. Unlike inte… t.me/hackgit/8399


nullt3r retweeted

EDR or SIEM flagging your Linux commands when reading sensitive files like /etc/shadow? Read the file from the raw disk to avoid simple detections. #redteamtips #hacking

nullt3r retweeted

No amount of melatonin can save you from the hyper-stimulation and afterglow of a 12 hour reversing session.
Laying in bed staring at the back of your eyelids and seeing the IDA Pro GUI burned into your retina for hours as you mumble belligerently about stack pointers.
nullt3r retweeted

Happy to announce the release of swSIM and swICC by Tomasz Lisowski, two open source repositories to enable SIM card emulation: github.com/tomasz-lisowski/s…, github.com/tomasz-lisowski/s…. Among others, we attached the emulator to a real phone via SIMTrace2 and interact with test networks!

ALT Experimental setup containing of a desktop computer, two phones, a Simtrace2, a raspberry Pi, and a nuand BladeRF. One of the phones is connected to the Simtrace2.




nullt3r retweeted

(JFSscan - Super-Fast Port Scanner) - skynettools.com/jfsscan-supe… #infosec #netsec #pentest #cybersecurity #bugbounty

nullt3r retweeted

Did they tell you "This function is included only in Windows XP." at docs.microsoft.com/en-us/win… ?
They lied :P
Feel free to try it at home: rundll32 keymgr,KRShowKeyMgr

nullt3r retweeted

#HuntingTipOfTheDay
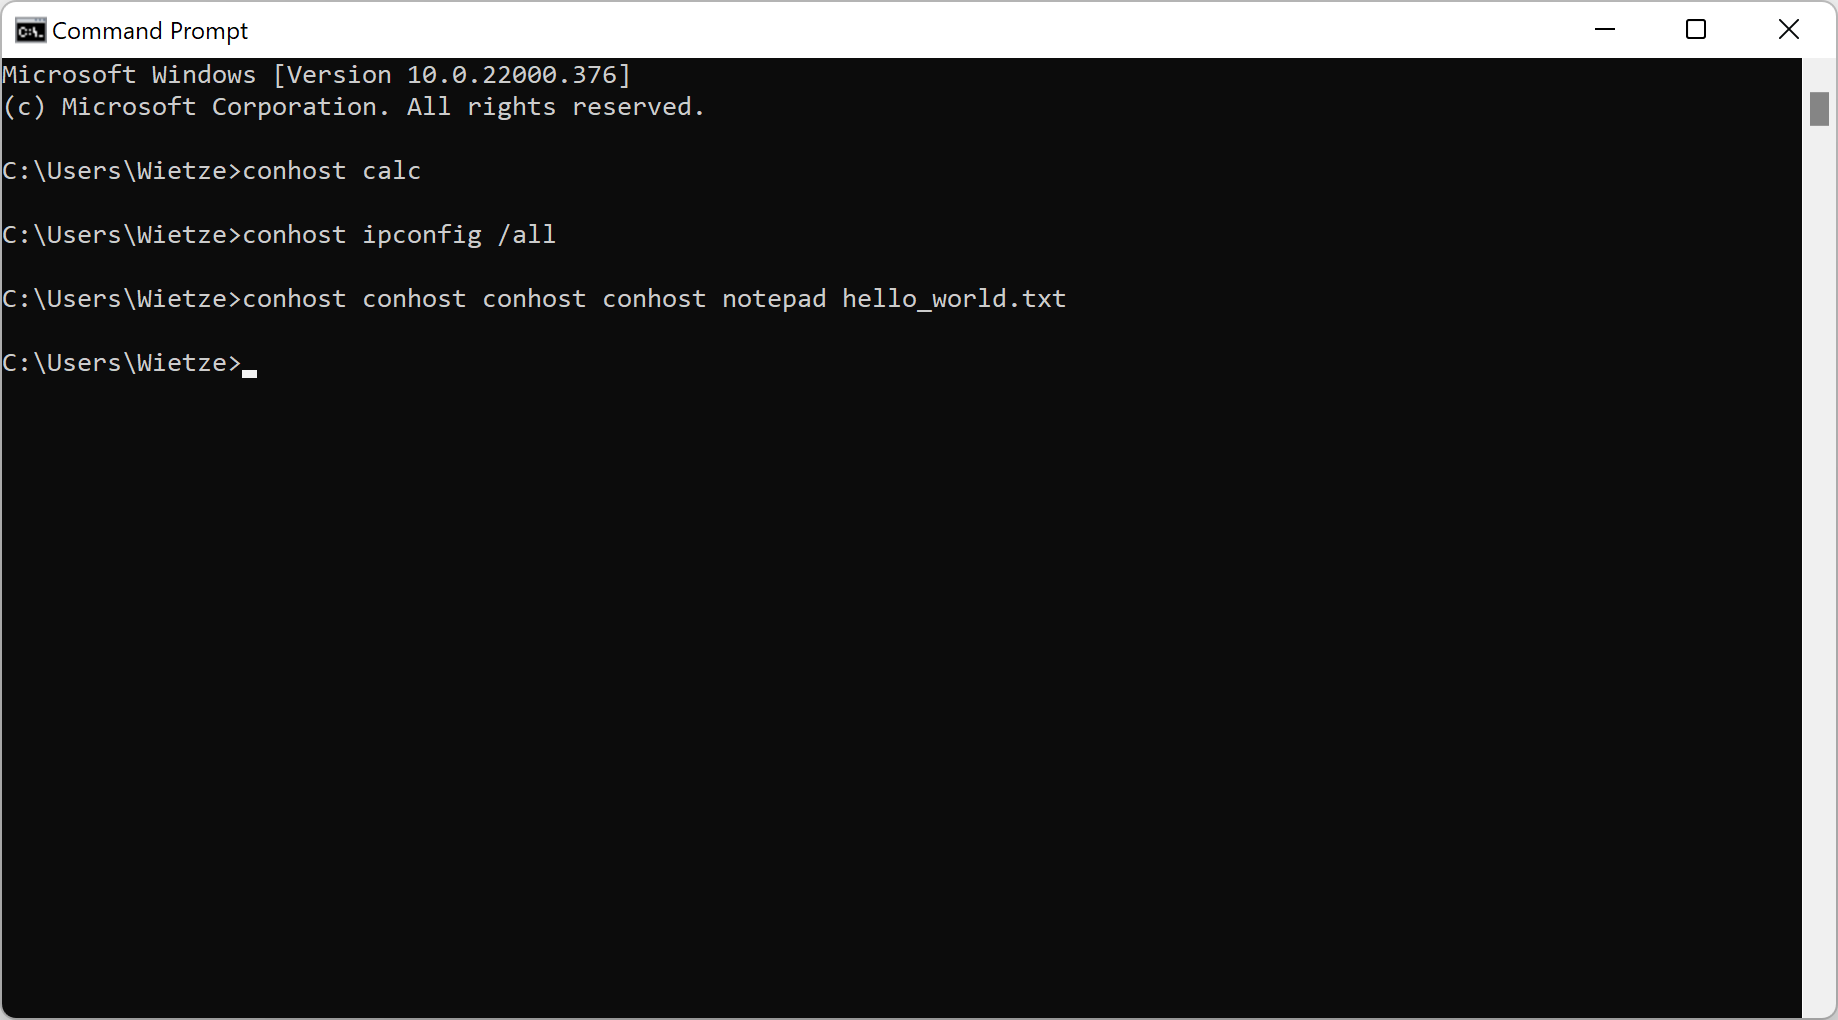
conhost.exe can be used to proxy the execution of arbitrary commands
⚔️ All you have to do is put 'conhost ' before your command. Simple yet effective way to frustrate parent-child relationships
🛡️ Hunting for rare children of conhost may find malicious use!

nullt3r retweeted

Melody - A Transparent Internet Sensor Built For Threat Intelligence ift.tt/kxJXqn8 #cybersecurity #bugbountytips #hacking #tools

nullt3r retweeted

Squalr - Game Hacking Tool Written in C# hakin9.org/squalr-game-hacki…
#infosec #cybersecurity #redteam #pentest #pentesting #hacking #hackers #coding #opensource #windows #network #programming #cyberattack


nullt3r retweeted
ppmap - a scanner/exploitation tool written in GO, which leverages Prototype Pollution to XSS by exploiting known gadgets hakin9.org/ppmap-a-scanner-e…
#infosec #cybersecurity #redteam #pentest #pentesting #hacking #hackers #coding #opensource #Linux #windows #uav #drones #webapp
nullt3r retweeted
JF is a very fast port scanning & service discovery using Masscan and Nmap github.com/nullt3r/jfscan
#infosec #cybersecurity #redteam #pentest #pentesting #hacking #hackers #coding #opensource #Linux #windows #DFIR #nmap #vulnerability #webapp

nullt3r retweeted

The JFScan (Just Fu*king Scan) is a wrapper around a super-fast port scanner Masscan By @nullt3r
github.com/nullt3r/jfscan
#infosec #bugbounty #thesecureedge