
Bug huntoor, prevented $1B+ in exploits GoLang | Rust | Move | C++ | Solidity For Booking DM on tg - @only01Essential
analyzer
Joined December 2022
- Tweets1.3K
- Following90
- Followers2.9K
- Likes5K






Essential retweeted

Hot take:
If you’ve found a vulnerability in a company that doesn’t run a public bug bounty program, you can still request a payout through @HackenProof
Boost your HackenProof rank and skip the payout headaches. We’ll handle the entire process, making it as simple as possible for both you and the company.

I just earned $3,500 for a bug report on @HackenProof plus another $2,000 for a bug report off bb platforms

I just earned $3,500 for a bug report on @HackenProof plus another $2,000 for a bug report off bb platforms
Wow. You made the money, but it's not your money 😂😂
Note. I don't have any money hanging there

This is very wrong Kuprum.
Sherlock wants 100% signal in every engagement it does. We have an entire judging system so we can deal with occasional false positives here and there.
What we’re talking about is participants who have delivered so many false positives that they’ve overloaded our systems and judges and risked our relationships with our clients. I had a call just yesterday with a client who doesn’t want to do a contest-style engagement with Sherlock because it took them so long to sort through false positives last time (even though Sherlock judged and triaged, they wanted to go through all the submissions). We will likely lose their business.
Sherlock and I have been crystal clear on this throughout the years: unearned money that can be unlocked by improving the Issues Ratio is not an SR’s money. They literally did not earn it. It’s as if we hired a security guard and the guard has called the police on every person who walked in the door. Is that security guard doing a good job? Should we hire them again? Should they be paid for that work? Of course not.
Do not be swayed by SRs who are lobbying to try to get a free airdrop out of Sherlock. It will not happen. And besides, it would make Sherlock’s contest-style engagements much worse in the future by rewarding the exact behavior we are trying to discourage.
When a protocol rewards a disclosure rightly, i do this thing were i come back at least once a month to ensure there aren't any lingering bugs that I missed, for two reasons actually 😅
One being that I know they will pay and another because I now genuinely care about the safety of their chains.
Between last week to today, I have reported more than 6 critical bugs across some of this well paying protocols after last month's visit.
So, if you are a protocol team and seeing this, please reward me rightly so I can add you to my good book lol
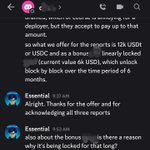
When they ask for your address to offer you a bounty without clearly stating the bounty amount, that's the red flag.
You don't have the chance to dispute anymore 💀
Just for context. Certain classes of bugs are even more catastrophic for certain chain types. For example, while persistent chain halt bugs are critical for almost all chains, they are more critical(if that makes sense) for oracle networks and gaming blockchains, that's why this chains tend to pay higher bounties for this bug type(in my experience).
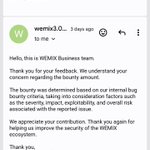
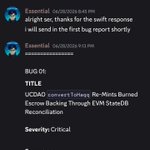
I found and reported a persistent chain halt that any user can pull off in @WemixNetwork and they paid me $100.
I have been pissed off about some of my experiences lately, so please let me rant here lol
github.com/wemixarchive/go-w…
After responsibly disclosing a critical bug report that could allow anyone to mint @Islamic_Coin out of thin air, the team behind @The_HaqqNetwork has decided to completely ghost me for months after receiving the bug reports 🤡
What's going on @ivanovp_ @vorobev_sa ?
While at it, no matter what you do, don't bother disclosing any bug to @eCash


More to come 🫡

Another $15,000 bounty secured by @only01Essential 🏆
Over the past year, @only01Essential has earned a total of $38,400 across 6 valid reports on HackenProof.
And there’s more to come 👀
Congrats from the HackenProof team – keep it going!


If you don't know the current situation in @code4rena, here is the brief:
Code4rena hosted K2 competition, which was the last one before announcing a winding down.
After distributing rewards to participants and sending judging fees, two SRs, @MaxZuvex and @0xArav, found what appears to be a Sybil attack.
They found that two wardens created their accounts days before the competition ended and submitted findings clearly copied from other wardens' work.
One submission belonged to a less-duplicated issue group, which increases their profit, and the other one was a QA report that resembles another warden's QA report and got 1st place.
Code4rena Team believes that the Judger is the one responsible for this, as he was one of the few people who had access to the submission before closing.
Code4rena was able to recover funds from these 2 newly created accounts (propabbly as KYC process and newly created account payout delays).
Code4rena asked the Judger to return the funds, but he has not responded to date.
C4 head judge will review the issues, remove duplicate sybil issues, review QA reports, and post the final result, and wardens will receive the amount deducted from their reward.
Essential retweeted

We really appreciate all you have done to support us and the wider community @only01Essential


Return the 3,400 btc first, then follow up with the full force of the law let's see how it goes

To those responsible for the theft of bitcoin from the Liquid Network:
Blockstream will not pay a ransom for the return of stolen funds. Taking assets without authorization and withholding their return is a crime, not responsible disclosure. It is not white-hat activity. It is theft.
We have engaged in good faith in an effort to secure the return of stolen user funds and protect the broader Bitcoin community. That effort should not be mistaken for acceptance of the actions taken nor of the terms being demanded.
We will not be a party to the precedent that open-source software developed for the good of the Bitcoin community should subject its developers to paying a ransom that far exceeds their economic participation.
Bitcoin is hard money and can’t be minted without costs, Bitcoin doesn’t haircut users to pay a ransom.
To the Bitcoin community:
We are fighting for what we believe in, for the users whose funds were taken, and for the principles on which Bitcoin was built.
The community has demonstrated incredible resolve with teams of people dedicating their time in support of each other to identify and patch vulnerabilities in each other's products and systems. We are all driven by the mission that Bitcoin is the single best asset, for every person, company, and institution on the planet to invest, use, and build on. The world is a different place with the advancements of AI, and the Bitcoin community has responded with force to combat that threat.
Damage has been done, battles have been lost, but on the whole the Bitcoin community is gaining ground in the war with bad actors.
We want to thank the community for those efforts, for your support in hardening the network, helping users recover funds, and for your support in our assertion that crime does not deserve rewards.
To those holding the stolen bitcoin:
There is still an opportunity to resolve this responsibly. The bitcoin can be returned and we can revert to the standard of white-hat principals.
However, if the funds are not returned, we will pursue every lawful avenue available to us. We will work with law enforcement, exchanges, service providers, forensic specialists, and other relevant parties to trace and recover the assets and identify those responsible.
More importantly, Bitcoin is transparent by design and the community is made up of the most sophisticated engineers, cryptographers, and white-hat hackers globally. Transactions do not disappear, and neither does the evidence they leave behind.
We will not pay for the return of stolen property. We will not abandon our users. The Bitcoin community will not stop pursuing the funds.
Return the bitcoin.


