
🦅 The changelog says "bug fixes." The diff says "security patch." We track CVE-less fixes so defenders don't fly blind. New drop every Thursday. @78_lab
Joined June 2026
- Tweets163
- Following2
- Followers72
- Likes1


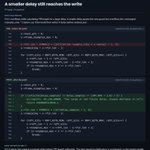
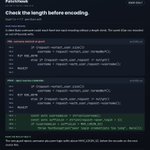
libpng 1.6.58 has a use-after-free in an unusual read path. A crafted PNG can make libpng read freed memory if an app calls png_read_end() after png_read_info() but before reading any image rows. Version 1.6.59 fixes it.
Advisory: github.com/pnggroup/libpng/s…

ALT CVE-2026-46675 in libpng. Two stacked code panels show the compressed-text release path. In 1.6.58, it only sets zowner to zero. In 1.6.59, it calls png_inflate_detach_buffers first. The error check above and the end of the block remain visible. For a crafted PNG and a read-end call before any image rows, the old path could use a pointer to freed data.
PatchHawk flagged pngrutil.c in the diff. We ran the same PNG through libpng’s public API on both releases. ASan caught a one-byte read from freed memory in 1.6.58. The 1.6.59 run ended with a handled parser error and no ASan finding.
PoC: github.com/78ResearchLab/Pat…
PatchHawk scans release diffs for security fixes. For selected cases, we share the input, Docker steps, and before/after logs so you can check our work: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more patch notes backed by code. #PatchHawk #78ResearchLab

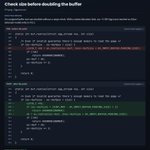
Firefox 151.0.3 includes Mozilla's fix. On Linux, Firefox uses the system FreeType library, so updating Firefox doesn't update that library. PatchHawk compared the releases. We matched the change to this CVE and ran the Docker test ourselves. mozilla.org/en-US/security/a…

PatchHawk looks for security fixes in software updates. For selected cases, we share the code change and steps to reproduce the bug: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained through code. #PatchHawk #78ResearchLab
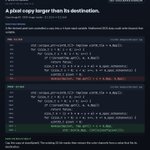
The PoC is now public: github.com/78ResearchLab/Pat…
It includes the 345-byte JXL input, Docker reproduction scripts, 0.11.1/0.11.2 djxl logs, and the Valgrind trace. The README states the tested 32-bit scope and limitations.
PatchHawk finds security-relevant fixes in release diffs. Selected PoCs include write-ups, repro steps, and pre/post comparisons: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained with real code and verifiable PoCs. #PatchHawk #78ResearchLab
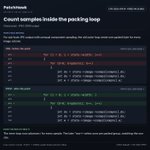
Both reproductions use FFmpeg's CLI entry points and are packaged in Docker. They show sanitizer-detected writes; we did not demonstrate code execution or an unsanitized crash.
Ogg PoC: github.com/78ResearchLab/Pat…
Filter PoC: github.com/78ResearchLab/Pat…

PatchHawk finds security-relevant fixes in release diffs. Selected PoCs include write-ups, repro steps, and pre/post comparisons: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained with real code and verifiable PoCs. #PatchHawk #78ResearchLab