IT-Security Consultant and musician
Bochum, Germany
Joined March 2020
- Tweets17
- Following56
- Followers62
- Likes27
Daniel Teuchert retweeted

After the log4shell vulnerability was patched with version 2.15, another CVE was assigned. Let's have a closer look at the localhost JNDI connections bypass and learn about fuzzing Java applications.
youtube.com/watch?v=kvREvOvS…
Daniel Teuchert retweeted

An excellent example of differential fuzzing using jazzer!

After the log4shell vulnerability was patched with version 2.15, another CVE was assigned. Let's have a closer look at the localhost JNDI connections bypass and learn about fuzzing Java applications.
youtube.com/watch?v=kvREvOvS…
Daniel Teuchert retweeted

+++ FuzzCon Europe 2021 Thread +++
We will keep you updated in the thread below.
Stay tuned✌️
Starting at 4:00 PM (CET)
Join the stream: fuzzcon.eu/2021/#registratio…
#security #applicationsecurity #conference
Daniel Teuchert retweeted

Multiple PLCs by Altus S.A. (rebranded by Beijer Electronics) are prone to different vulnerabilities. r.sec-consult.com/altus An attacker can gain full system level access on the PLCs without prior authentication @BeijerTR @pnolsec #infosec #iiot

Daniel Teuchert retweeted

Super cool to see more work building on top of kAFL! We will soon present very similar research (though with snapshots): usenix.org/conference/usenix…

Our @BlackHatEvents talk is over (and went great!) and now's a good time to share everything about our research!
Our research process is detailed in this blog post, go give it a read and let @peleghd and I know if you have any questions & thoughts!
guardicore.com/labs/hafl1-ou…
Daniel Teuchert retweeted
Join our live coding session:
@pnolsec will demonstrate an automated mocking approach that will instantly improve your code coverage and protect your embedded software against unexpected edge cases.
page.code-intelligence.com/m…
Daniel Teuchert retweeted
Last chance to sign up for today's live hacking session!
You cannot attend? No problem. Make sure to get the recordings: code-intelligence.com/automo…
Daniel Teuchert retweeted
Blog post by @pnolsec on fuzzing embedded software. Daniel also presents an approach to automatically generate fuzz tests in these scenarios.

What are the challenges in fuzzing embedded systems with hardware dependencies, and how can we overcome them with fuzzing and mock data?
Read: blog.code-intelligence.com/a…
#embedded #security #securitytesting #ISO21434

Daniel Teuchert retweeted
Live hacking session:
Testing embedded systems with dependencies.
This Thursday (29.04.), @pnolsec will demonstrate how to automate and improve security testing for #automotive systems.
Interested?
code-intelligence.com/automo…
#fuzzing #embedded #cpp
Daniel Teuchert retweeted
Join our live-coding session:
@pnolsec will demonstrate a new #fuzzing approach, that will instantly improve your code coverage.
code-intelligence.com/webina…

Daniel Teuchert retweeted

Testing: Google integriert deutschen Jazzer in OSS-Fuzz heise.de/news/Testing-Google… #CodeIntelligence #Codeanalyse
Daniel Teuchert retweeted
Multiple Confluence Plugins are affected by stored #XSS vulnerabilities r.sec-consult.com/con allowing to inject malicious JavaScript code into #Confluence pages. #atlassian #infosec @avono_ag @RefinedSoftware @ServiceRocket @akeles_cs @AptisGmbh via @pnolsec @rferdigg

Daniel Teuchert retweeted
Together with @pnolsec and @ms_s3c we just published version 2.0 of Nautilus, our grammar fuzzer. It's now compatible w AFL++, can fuzz binary only targets, supports binary formats and scripting for non context free grammars & much more.
Get it at:
github.com/nautilus-fuzz/nau…

Daniel Teuchert retweeted

After a decade of fuzzing, we just launched FuzzBench, a fuzzer benchmarking platform to bridge the gap between academic fuzzing research and industry fuzzing engines (e.g libFuzzer, AFL, Honggfuzz). github.com/google/fuzzbench

Daniel Teuchert retweeted
Blackhat uploaded @ms_s3c and my talk "What the Fuzz" youtu.be/Wy7qY5ms3qY
Daniel Teuchert retweeted

I gave the Nautilus fuzzer a spin on QuickJS for fun. Super easy to run. Also effective compared to AFL (unsurprising, and admittedly my seeds probably weren't great).
Many of these appear to be memory leaks (forgot to set detect_leaks=0, a la AFL), but some are more interesting

Daniel Teuchert retweeted

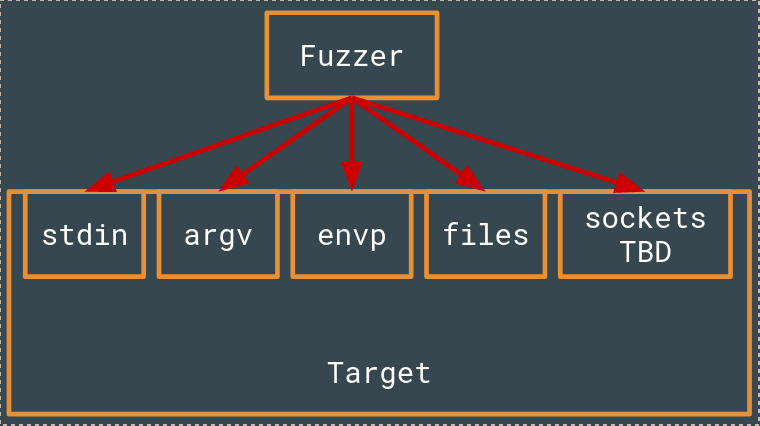
@HushCon con this Saturday Patrick and I will be talking about our new fuzzer! We build a fuzzer that can detect new inputs to a target and automatically fuzz them, all without any manual harnessing required. We also have tons of cool data to show off. Here is a sample: 1/n