

Canberra, Australia
Joined November 2008
- Tweets820
- Following1.1K
- Followers333
- Likes1.6K


Rick Oates retweeted

Our full 2021 training agenda is now ready. In-person classes only, with respect for health & safety! Quality > quantity! :) facebook.com/corelanconsulti… // linkedin.com/feed/update/urn… - Seats are limited, grab yours now! Sharing=caring <3
Rick Oates retweeted

Reinstalled my OS yesterday. Apologies to anyone who lost their persistence, and congratulations to anyone who kept theirs 💪
Rick Oates retweeted
An S3 bucket takeover and PGP signature bypass in fwupd (CVE-2020-10759) put me between a whooole bunch of Linux computers and their firmware updates. github.com/justinsteven/advi…

Rick Oates retweeted

Need to traverse security zones?
In this new post, I share a trick for establishing peer-to-peer C2 over DNS with ADIDNS.
shenaniganslabs.io/2020/04/1…

Rick Oates retweeted

#BloodHound 3.0 is here!
BloodHound: https://teapawt.org/t.co/LOlhrNILYB
Blog: https://teapawt.org/t.co/FGyF2jSBCP
Webinar deck: https://teapawt.org/t.co/h49EE4azyh
Webinar recording coming soon
#BloodHound 3.0 shirt: (all profits go to @MDAorg)
customink.com/fundraising/th…

Rick Oates retweeted

RAW timelapse footage of the last few hours - Orroral Valley fire -Out of control #canberra #australia #AustraliaBurning #AustralianFires
Rick Oates retweeted

according to all known laws of aviation, there is no way that a spider should be able to fly,
theatlantic.com/science/arch…
Rick Oates retweeted

The world's largest military budgets:
🇯🇵 $50 billion
🇬🇧 $53 billion
🇫🇷 $56 billion
🇮🇳 $58 billion
🇷🇺 $63 billion
🇸🇦 $83 billion
🇨🇳 $168 billion
🇺🇸 $700 billion
What if—just maybe—we led the world not in weapons and war, but in fighting humanity's common enemy: climate change?
Rick Oates retweeted

Today we released a community-developed exploit module PR for #BlueKeep (CVE-2019-0708). We expect to continue refining the exploit over time in collaboration with contributors. Some important notes on exploitation and detection from @busterbcook: blog.rapid7.com/2019/09/06/i…
Rick Oates retweeted
Did you know:
1. Computer objects in AD can be added to the local admins group on other computers.
2. NT AUTHORITY\SYSTEM authenticates to other systems as the AD computer principal
3. Privileged computer accounts are VERY common, and typically overlooked.
#BloodHound basics

Rick Oates retweeted

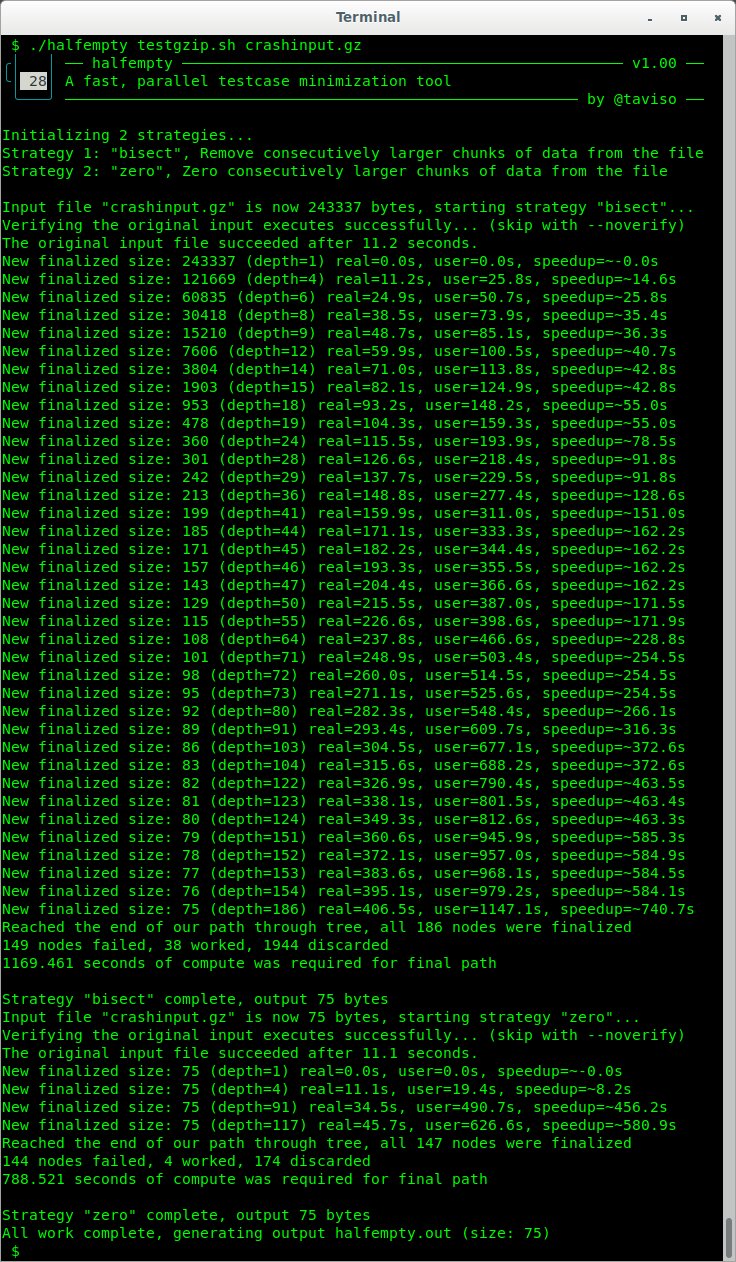
I finally wrote a small tool I've wanted for a long time: A parallel testcase minimizer. It's called halfempty, and I'm already finding it useful as part of my fuzzing workflow. /cc @lcamtuf github.com/googleprojectzero…

Rick Oates retweeted

WE FOUND HIM!! A thread 👇👇
After 3000 RTs, 3 news articles, 1 video and thousands of wonderful messages from around the world, @Arjen78 made contact with the family!
Guys, I knew the internet was great but this is something else.
teapawt.org/MeAndVan/status/116092…


Rick Oates retweeted

De weldoener die de Koerdische Mevan Babakar -destijds 5 jaar- een rode fiets gaf in het Zwolse azc, lijkt gevonden, mogelijk volgt later vandaag een ontmoeting. destentor.nl/zwolle/zwolse-w…
Rick Oates retweeted
Copy your payload into %userprofile%\AppData\Local\Microsoft\Teams\current\
Then
%userprofile%\AppData\Local\Microsoft\Teams\Update.exe --processStart payload.exe --process-start-args "whatever args"
Trusted signed binary will run the payload for you 😊
#RedTeam #Pentesting
Rick Oates retweeted

WSL 2 lives up to the hype. @Microsoft hit it out of the park. The improved system call functionality means low-level network tools that people like me rely on will actually work. Starts faster than any VM.

Verifying myself: I am rickoates on Keybase.io. ZchlCZKfAFbRzi1D70I_BVMrgw5dFTi_GZ4A / keybase.io/rickoates/sigs/Zc…
Rick Oates retweeted

Gotta say, I think I've found the perfect coffee roast to fuel my DFIR R&D responsibilities ☕️

Rick Oates retweeted

Glad you enjoyed WAHH but please do check out the Web Security Academy. We’re building this instead of a third edition of WAHH: portswigger.net/web-security

hats off and thanks to @PortSwigger and his team for writing The Web Application Hacker's Handbook - I can't imagine the dedication, research, and amount of creativity required to pack all the astonishing information and tricks into this book. Your work is greatly appreciated!