

We had our own Path =))
Joined July 2012
- Tweets81.2K
- Following1.8K
- Followers2.7K
- Likes12.1K




kris retweeted
Get ready for the biggest Rabbit Hole of the year (and quite possibly your life).
Notifications on.
discord.gg/aztec
I'm taking a stand for privacy.
Privacy is the missing key that will unlock new dimensions, expand opportunities, and finally bring the world onchain.
View my @aztecnetwork privacy glyph & create your own: glyph.aztec.network/risk22_

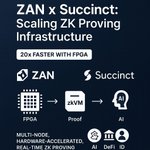
📣 ZAN Joins the Succinct Prover Network as a Multi-Node Prover!
ZAN is now live on the @SuccinctLabs Prover Network 🚀
Their FPGA-accelerated proving setup delivers 20× performance gains over CPUs 🔥
From hardware to high-availability clusters, ZAN is scaling real-time ZK proving for identity, AI, DeFi & more.
The proving layer is going global—and ZAN is helping power it. ⚡

🚀 Big move in ZK infrastructure!
@SuccinctLabs has teamed up with @cysic_xyz and it's a game-changer. Cysic is now a multi-node prover in the Succinct Prover Network, bringing blazing-fast hardware (1.33M Keccak/sec!) into the mix. 🔥
Together, they're scaling real-time ZK proofs for identity, AI, DeFi & beyond without compromising decentralization.
This is what the future of zero-knowledge looks like: fast, modular, decentralized. ⚡
Let’s build.
kris retweeted
1/5 Aztec just entered a critical phase: Adversarial Testnet.
The network is designed to be private and decentralized from day one.
This phase is a key step toward launching the first fully decentralized privacy-preserving L2 network on Ethereum. aztec.network/blog/aztec-ent…

.@cysic_xyz tackling two key ZK bottlenecks:
1. Decentralized provers to avoid single points of failure.
2. Lowering cost and latency through proof aggregation, settling once on Ethereum, with optional off-chain pre-verification for speed.
Smart, scalable approach to ZK infra.

Learn about cysic
From the @cysic_xyz white paper, it's already known that cysic plan to provide hardware for zk infras for faster processing of zkp
How cysic plan to achieve this is by tackling two challenges;
> Prover decentralization
The idea behind decentralized provers is that it prevents single points of failure in Zk projects
> Latency and cost in Zk proof verification
This involves reducing the fees in settling proofs by aggregating proofs and then settling it all at once on Ethereum. This reduces the gas fees for verification but wait time increases
But the wait time can be bypassed if the user verifies off chain first before settling on Ethereum

.@SuccinctLabs x @cysic_xyz is a game-changer for ZK.
🔹 SP1 makes generating proofs easy (no deep math needed).
🔹 Cysic hardware makes them blazing fast and cheap.
Think $5 → $0.10 per tx.
Think hours → milliseconds.
Think dev-friendly + energy-efficient.
ZK infra just got a major upgrade.
This duo is pushing real-world ZKP adoption into overdrive. ⚡
SP1-CC is a game-changer for Ethereum.
Built by @SuccinctLabs, it lets smart contracts run heavy computations off-chain and verify them on-chain via ZK proofs, no L1 code changes needed.
Dev superpowers unlocked:
• Access historical state
• Run gas-free complex logic
• Upgrade without redeploying
From trustless airdrops to proof-of-exploit, SP1-CC makes Ethereum smarter, cheaper, and more powerful.

Capzz Random @SuccinctLabs Yap - Day 19
TOPIC: Introducing SP1-CC: Unleashing the Full Power of the EVM
Succinct launched something new called SP1-Contract-Call (SP1-CC).
SP1-Contract-Call (SP1-CC) is a ZK coprocessor built by. Think of it as a “sidekick computer” for Ethereum smart contracts.
It lets smart contracts on Ethereum run massive computations off-chain (using SP1 zkVM) and verify the result on-chain with a ZK proof.
That is basically doing heavy lifting off-chain and then prove to Ethereum that the work was done correctly, using zero-knowledge proofs (ZK proofs).
It's like giving your smart contract a powerful computer friend.
Ethereum is great, but it has limitations:
→ Gas is expensive
→ Smart contracts can’t do complex tasks
→ Historical data isn’t easily accessible
→ Immutable contracts can’t evolve
SP1-CC breaks these limitations without modifying Ethereum itself.
How It Works
SP1-CC introduces a new way to compute:
Read → Compute → Verify
Read
Grab any past data on Ethereum, balances, transactions, smart contract storage, etc.
Compute
Run your logic (like filters, math, simulations) off-chain, where it’s fast and cheap.
Verify
Send a tiny ZK proof to Ethereum that confirms everything was done honestly.
What This Unlocks
Before SP1-CC:
You couldn't access old data easily.
You were limited by gas fees.
You couldn’t upgrade contracts without big headaches.
Now, with SP1-CC:
You can access any past block or data on Ethereum.
Run super heavy logic without worrying about gas.
Simulate contract logic, upgrade functionality, and prove it all back on-chain.
The SP1-CC Tools (Primitives)
To do all this magic, SP1-CC gives devs 3 powerful tools:
call()
Emulates a contract call at any past block. Useful for reading old data or simulating behavior.
create()
Spins up a fake contract off-chain just to test or simulate what it would do.
get_logs()
Search logs/events across history, something Ethereum doesn’t easily allow.
Here's how the EVM changes for developers
What’s Possible Now? Real-World Use Cases
1. On-chain Governance Without Migrating Tokens
- Normally, to add governance to an old token, you’d need to upgrade or redeploy.
- With SP1-CC, you can track holders, votes, and DeFi positions, all off-chain, and prove it works, without touching the original token contract.
2. Airdrops You Can Actually Trust
- No more sketchy off-chain lists.
- With SP1-CC, you can prove that only users who did X, Y, Z got included, and everyone can verify it.
3. DeFi Oracles Without Complicated Tricks
- Normally, getting a token’s historical price (like TWAP/VWAP) is messy and costly.
- SP1-CC lets you read price data from any past block and calculate anything you want off-chain.
4. Whitehat Security Proofs (Proof of Exploit)
- Instead of sharing private bugs, security researchers can simulate the bug with SP1-CC and prove the vulnerability without revealing the actual exploit logic.
Real Projects Are Already Using This
@eigencloud EigenDA
They use SP1-CC to verify that each blob of data is backed by staked votes.
Without SP1-CC? Doing that directly on Ethereum would be way too expensive.
With SP1-CC? They do it off-chain, then just prove it to Ethereum cheaply.
It’s faster, more secure, and scalable
Why This Matters for the Future
SP1-CC gives developers and protocols new powers without needing to change Ethereum itself. That’s huge.
With it:
Ethereum gets smarter, faster, and more flexible.
Devs can dream bigger without being scared of gas limits or history access.
Web3 gets more trustless, transparent, and user-friendly.
It’s like plugging a super-brain into Ethereum, and letting it prove everything it thinks with math.
Shoutout to the team and everyone working behind the scenes to give us the future of Ethereum.
@0xCRASHOUT @SaiMoo_n @Zahar0n_


Rollups are solo—Espresso makes them a team.
@EspressoSys syncs rollups without replacing them, turning fragmentation into flow.
Seamless UX, coordinated chains.
gBrew gEspresso ☕
Espresso started quiet—now it’s storming Web3.
From 100 nodes to cross-chain bridges to scaling for thousands.
Low latency, high impact.
This is modular dominance. ☕⚡
Ethereum is going ZK-native.
No more re-execution just math-based block proving at L1.
SP1 Hypercube by @SuccinctLabs is already proving 94% of blocks in ~10s, pushing zk from theory to production.
This shift means:
• Faster L1
• Trustless light clients
• Native zk-rollups
• Secure rollup composability
Ethereum isn’t just a blockchain anymore. It’s becoming a global proving machine.

Ethereum’s Leap into ZK: Real-Time Proving at the Base Layer
The Ethereum Foundation recently unveiled a bold new direction that marks a foundational shift for Ethereum: Zero-Knowledge (ZK) proofs are moving from Layer 2 rollups to the base protocol layer.
Eventually, zkEVM clients at Layer 1 could eliminate re-execution entirely, transforming Ethereum into the world’s largest zero-knowledge application.
What Is Real-Time ZK Proving?
Ethereum’s new execution model is centered on zk clients; validators that prove blocks using cryptographic proofs instead of replaying every transaction. The idea is to verify state transitions with math, not trust.
These zk clients must meet strict real-time benchmarks:
> Proof Latency (P99): ≤ 10s
> Security: ≥ 128-bit (≥ 100-bit initially acceptable)
> Proof Size: ≤ 300 KiB
> Hardware Cost: ≤ $100K (on-prem)
> Power Usage: ≤ 10 kW
> Codebase: Fully open source
This “real-time proving” goal ensures proofs can be generated within Ethereum’s 12-second block time making full-node proving at home viable.
SP1 Hypercube: A Working Example
Leading this charge is SP1 Hypercube from @SuccinctLabs:
> Proves 94% of blocks in under 12s (avg ~10.3s)
> Operates on ~160 - 200 RTX 4090 GPUs
> Cost: ~$300 - $400K for production setup
> Uses transparent STARKs, with optional SNARK wrapping
SP1’s performance comes from innovations like multilinear polynomial proof systems and its Jagged PCS scheme, enabling massive parallelism and prover efficiency. The stack will be open-sourced post-audit, opening the door to community proving.
Why This Changes Everything:
Real-time ZK at Layer-1 unlocks more than scalability:
> Layer-1 Throughput Boost: Proofs remove redundant re-execution
> Native zk-Rollups: Finality becomes cryptographic
> Universal Light Clients: Phones can verify blocks in milliseconds
> Rollup Composability: Synchronous, secure multi-rollup interaction
Ethereum’s model flips from trusting honest validators to verifying every block cryptographically. This is decentralization through verifiability.
The zkVM Race
Ethereum isn’t betting on just one proving system. zk diversity is key:
> RISC Zero: A RISC-V zkVM under $120K proving setups
> ZKM, Valida, Snarkify: Each exploring new ISAs and circuit design
> EthProofs: Public dashboard tracking zkVM performance against EF targets
Multiple zkVMs per block = resilience and antifragility.
What’s Next:
Ethereum’s proving roadmap includes:
> Devconnect Argentina (Nov 2025): Home proving milestone
> Pipelining (Glamsterdam): Extends proving window beyond single blocks
> zkVM Client Diversity: Verifying 3 zk proofs per block
Challenges Remain:
> Tail latency and worst-case block proving.
> Hardware accessibility and prover decentralization.
> Formal verification, client specs, and gas incentive alignment.
Ethereum Is Becoming a Proving System
The Ethereum Foundation, led by engineers like Sophia Gold, is building more than a blockchain. It’s creating a global proving system; a decentralized layer of programmable trust. Succinct Labs, RISC Zero, and other zkVM builders are already proving live mainnet blocks. With SP1 hitting 10.3s latency and 94% real-time coverage, the Ethereum Foundation's benchmarks are not aspirational, they're operational.


.@anoma flips the script on blockchains—no order books, just pure intent.
• Private by default
• Peer-to-peer coordination
• Multi-asset native
• Built for complex, trustless use
It’s not just a chain—it’s a new paradigm for how value moves.

GM CT it’s another beautiful day to study Anoma.🧙♂️
Anoma is a next generation blockchain protocol designed for privacy preserving, decentralized applications and intent based trading. Unlike traditional blockchains that rely on order books or centralized coordination, @anoma introduces a novel intent centric architecture, allowing users to express what they want (intents), rather than how to get it.
Key Features:
• Intent Centric Design: Enables peer to peer coordination without needing trusted intermediaries or centralized marketplaces.
• Full Privacy: Built with advanced cryptography (like zero-knowledge proofs) to ensure transaction privacy across assets, data, and identities.
• Composability: Supports complex logic and multi party transactions, suitable for use cases like private bartering, DAO coordination, and decentralized finance (DeFi).
• Multi Asset Support: Designed to handle any kind of asset or value representation natively, not just tokens.
Anoma reimagines the way value is exchanged and coordinated across decentralized networks, prioritizing autonomy, privacy, and interoperability.

SP1 isn’t just a zkVM — it’s a full ZK powerhouse by @SuccinctLabs:
• Hypercube: Blazing-fast block proving
• SP1-CC: ZK coprocessor for smart contracts
• Turbo: GPU-accelerated prover
• 2FA: ZK-based WebAuthn for trustless auth
Modular. Open-source. Production-ready.
SP1 is the ZK stack Ethereum’s been waiting for.

Let's talk about the one of the most talked about tech stack at the moment (SP1). Walk with me ⬇️
---
🧵 The SP1 Stack by @SuccinctLabs is wild 🤯
It’s not just a zkVM.
It’s a modular suite of ZK components—each unlocking new powers for Ethereum builders.
Let’s break down:
—> SP1 Hypercube
—> SP1-CC
—> SP1 Turbo
—> SP1 2FA
And how they all fit together 👇
---
1/ SP1 is the zkVM core.
Built by Succinct Labs, SP1 is a fast, Rust-native, RISC-V zkVM optimized for proving real-world logic with recursion, STARKs, SNARKs, and GPU acceleration.
But what makes SP1 powerful is not just the VM...
It's the ecosystem around it.
---
🔷 2/ SP1 Hypercube
> High-throughput zkVM execution layer
What it is:
A parallelized proof system for SP1 programs, designed to handle massive workloads like full Ethereum block validation.
Workflow:
Compile Rust/LLVM → SP1
Prove 600M+ RISC-V cycles
Parallelized on GPU clusters (e.g., 200x RTX 4090)
Get STARK proof → SNARK for on-chain
Use Cases:
🌐 Rollups, Shared Sequencing, L1 Proving, Full Nodes
---
🛠 3/ SP1-CC (Contract Call)
> The ZK coprocessor for Ethereum smart contracts
What it is:
A dev-friendly library that lets you simulate and prove smart contract calls off-chain, then verify them on-chain (≈280k gas flat).
Workflow:
Define Solidity call in Rust
Run cargo prove
Submit proof to on-chain verifier
Use Cases:
💸 ZK Airdrops, DeFi logic off-chain, Extend immutable contracts
---
⚡ 4/ SP1 Turbo
> Blazing-fast prover for any SP1 program
What it is:
A GPU-accelerated proving backend optimized for SP1 workloads—used by both Hypercube and CC under the hood.
Workflow:
Runs proofs 10x faster than most zkVMs
Supports recursion, STARK-to-SNARK pipelines
Integrated with real-time proving (sub-12s for full blocks)
Use Cases:
🏎️ Scaling any SP1-based application, real-time zk infra
---
🔐 5/ SP1 2FA
> Verifiable WebAuthn-based 2FA via ZK
What it is:
A proof system that lets you generate ZKPs of hardware-backed authentications (WebAuthn/FIDO) for trustless verification.
Workflow:
User authenticates via WebAuthn (YubiKey, FaceID, etc.)
Generate proof that it happened (off-chain)
Verify on-chain (EVM or elsewhere)
Use Cases:
🔐 Onchain identity, ZK logins, passwordless auth, DAO security
---
🧠 6/ Why this matters:
Component|Role|Main Use Case
⬇️ ⬇️ ⬇️
SP1 Hypercube|Infra-grade zkVM engine|Rollups, Sequencers, L1 Proving
SP1-CC|Dev toolkit for EVM contract calls|Coprocessors, ZK airdrops, L3s
SP1 Turbo|GPU prover backend|Acceleration for SP1 proofs
SP1 2FA|ZK proof of WebAuthn identity|Trustless Auth, zkLogin, DeFi UX
Together, they’re turning Ethereum into a fully programmable ZK machine.
---
7/ TL;DR: SP1 is not just a zkVM for those of you who do not understand it yet.
It’s a stack:
Hypercube = enterprise-grade proving
CC = dev-grade zk coprocessing
Turbo = gas pedal for proofs
2FA = decentralized identity w/ ZK
This is what modular, programmable ZK looks like 🔥
---
✨ Bonus: Every component is open-source, developer-first, and production-ready.
SP1 is quietly becoming the Linux kernel of ZK computing. Are you paying attention?
Huge news for the ZK space! 🚀
@SuccinctLabs 🤝 @cysic_xyz
Succinct is expanding its decentralized prover network — and now, ZK hardware powerhouse Cysic is joining in with multi-node provers and plans to onboard their specialized ASICs.
Top-tier zk proving meets cutting-edge hardware acceleration. This partnership is a game-changer.

Massive leap for Bitcoin! 🔥
The Alpen Labs x @SuccinctLabs partnership is a game-changer — bringing ZK programmability to Bitcoin without compromising its core values.
Succinct’s SP1 enables scalable, verifiable proofs, while Alpen builds trustless infra for high-throughput apps. This unlocks complex use cases and real financial innovation on BTC.
Bullish on ZK tech finally empowering Bitcoin beyond store-of-value.

Succinct ZK Revolution in Bitcoin
Today i want to talk about the strategic partnership between Alpen Labs and Succinct, which aims to enhance Bitcoin's programmability through zero knowledge proofs (ZKPs).
Alpen Labs focuses on expanding global financial access via ZK-enabled infrastructure on Bitcoin leveraging Succinct's expertise in succinct proofs. The core of this collaboration is the integration of Succinct's SP1 technology which enables efficient and verifiable proofs for large-scale transactions.
This allows Alpen Labs to process tens of thousands of transactions with succinct proofs verifiable on the Bitcoin network improving scalability and privacy.
-------------------
The technical synergy lies in Succinct's ability to generate compact proofs that maintain Bitcoin's security and decentralization while supporting complex financial applications.
Alpen Labs' infrastructure benefits by building trust in minimized Layer 2 solutions crucial for handling high transaction volumes without compromising programmability.
This partnership marks a significant advancement in making Bitcoin a more versatile platform for financial innovation, combining Alpen Labs' vision with Succinct's cutting-edge technology.
The result is a robust framework that pushes Bitcoin's capabilities ensuring both security and efficiency in a decentralized environment.
-------------------
This development is quite exciting for the future of blockchain technology. Bitcoin's programmability could fundamentally change how financial systems operate.
Alpen Labs and Succinct's collaboration is not just a technical advancement but also the realization of a vision. Such innovations push the boundaries of the digital world while taking important steps towards providing trust and access.
Therefore closely following and understanding this agreement is quite important for technology enthusiasts.

a41 isn’t just joining the Succinct Prover Network — they’re leveling it up.
With industrial-grade GPU clusters, a custom SP1 backend, and plans to open-source their infra, this is real zk infra firepower. 🔥
This means faster proofs, lower costs, and a smoother dev experience for anyone building on SP1 — especially for CLOBs, L3s, and high-throughput apps.
a41 x @SuccinctLabs is more than partnership. It’s infrastructure evolution.

Who is @a41_allforone and Why Does It Matter for @SuccinctLabs ?
If you’re deep in crypto infra, you’ve probably heard of a41.
They’re not just validators they’re one of Ethereum’s top 10 by staked ETH, and they secure networks like Cosmos, Aptos, and EigenLayer too.
So when a heavyweight like a41 joins a proving network, it’s worth paying attention.
a41 x Succinct: What Just Happened?
a41 officially joined the Succinct Prover Network, bringing with them:
• a multi-node orchestration layer built for SP1
• access to hundreds of GPUs
• new compiler backend to reduce proving costs
• plans to open-source their SP1 infrastructure
This isn’t just participation. This is contribution.
Why It’s a Big Deal (For Succinct + the Ecosystem)
• Production Grade Firepower
a41 is scaling proofs with GPU clusters that can actually support real world apps like CLOBs, gaming, and L3s. Succinct now has industrial-strength proving to back up its zk ambitions.
• Network decentralization
The Prover Network just got more resilient. With a41 onboard, proving power is no longer concentrated it’s distributed. That’s good for censorship resistance and trust minimization.
• Lower cost, better UX
a41’s compiler work means developers won’t have to be ZK experts to generate proofs. Write in Python. Compile. Prove.
This dramatically reduces friction for anyone building on SP1.
Why It Matters for CLOBs on Blobs
Let’s not forget:
CLOBs on Blobs need fast, verifiable execution at scale.
That means:
• fast proofs
• low latency
• massive throughput
• decentralized fallback (for escape hatches)
🧵 TL;DR
a41 is one of the most trusted infra providers in Web3
They’ve joined Succinct’s Prover Network with serious scale
Their involvement means better performance, cheaper proofs, and a dev friendly zk future
This is the zk infra moment we’ve been waiting for and it’s already running.


.@SuccinctLabs is at the forefront of Zero-Knowledge (ZK) technology, making blockchain more secure and scalable.
Their ecosystem includes diverse projects applying ZK:
-Security & Performance: Automata, Fiamma, Mynt, Termina
-Scalability: Caldera, Scalerize, Polygon, Celestia
-Privacy & Cross-chain: Babylon, Solarize, Cosmos
-Specialized: ZeroSync (Bitcoin proofs), Avail (platform features)
-Talent: Cander (fintech talent)
Succinct Labs' ZK innovations are transforming everything from DeFi to renewable energy, driving the blockchain revolution.

🌟 Exploring the @SuccinctLabs ecosystem!
Zero-Knowledge (ZK) tech powers secure, scalable blockchain innovation, connecting Ethereum, Solana, and beyond.
🔥 Key projects:
🔶 Automata: Boosts security & performance with ZK for DeFi/dApps.
🔶 Babylon: Enhances privacy & cross-chain links with ZK.
🔶 Caldera: Scales apps & networks using ZK tech.
🔶 Fiamma: Lifts privacy & security with ZK solutions.
🔶 Termina: Powers fast, secure off-chain computation with ZK.
🔶 Mynt: Secures stablecoin minting (USDm) with ZK.
🔶 Cander: Fuels growth with fintech talent for Succinct.
🔶 Scalerize: Optimizes rollups with ZK for scalability.
🔶 Solarize: Manages energy transactions with ZK privacy.
🔶 Ethereum: Gains scalability & security from ZK.
🔶 Cosmos: Improves interoperability with ZK tech.
🔶 Polygon: Scales Ethereum with ZK-powered apps.
🔶 Celestia: Builds modular ZK solutions for innovation.
🔶 ZeroSync: Develops Bitcoin proofs with ZK.
🔶 Avail: Enhances platform features with ZK.
This ecosystem is buzzing!
From DeFi to renewable energy, SuccinctLabs’ ZK vision is breaking barriers. They’re leading the blockchain revolution! 🚀 #SuccinctLabs #ZKTech
