

learning, breaking🔁 | bug bounty hunter in my free time
void
Joined March 2010
- Tweets33.1K
- Following1.6K
- Followers2.3K
- Likes2.5K





Pinned Tweet
I'm going to explain how I found two OS command injection vulnerabilities a few days ago.
The vulnerabilities were quite easy to exploit once the injection points were identified.
manuel valdez⛩️ retweeted

Getting pretty damn sick of these 'CVSS 10' AI slop half-assed RCE drops tbh.


manuel valdez⛩️ retweeted
Hot areas, I think I heard @Jhaddix talking about this, mapping these hot spots to prioritize them in your testing is where sometimes bugs might show up in < 1h of using the app

That's the hard part.
There's a reason why almost anyone can solve "find-the-bug" challenges, but very few people can find live vulnerabilities in the wild.
CTFs have bounded domains and usually one clear, proven solution. Live exploits, on the other hand, are unbounded -- we don’t know where they are, or even if they exist at all.
That said, there are hot zones in codebases -- areas where developers are more likely to make mistakes.
There are also danger zones -- places where even a small error would be fatal.
Once you’ve worked with many similar codebases, languages, patterns, and technologies, you start to see those hot spots instinctively.
Hunting is like reading a heatmap.

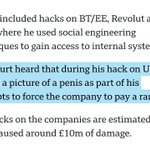
Social engineered his way to flash his wiener😭


🚨🇬🇧 Grand Theft Auto hacker pleads guilty to Rockstar Games breach and multiple cyberattacks that caused millions in damages
Arion Kurtaj, 21, a member of the LAPSUS$ hacking group, has pleaded guilty at Woolwich Crown Court to hacking Rockstar Games in 2022 and stealing 90 clips of unreleased Grand Theft Auto gameplay.
Kurtaj also admitted involvement in cyberattacks targeting Uber, Revolut, and BT/EE, with prosecutors estimating approximately £10 million in damages across the attacks.
Previously held indefinitely in a secure hospital, Kurtaj was transferred to prison in January after doctors deemed him fit to stand trial. He will be sentenced at a later date.

2
411
*Sends AI slop without verifying it and with no security implications whatsoever*
Bg: *Rightfully calls out on his bs*
*Proceeds to rant on X*
I see this cycle every week
AI agentic is amazing, but not every bug it spits out is a vulnerability with a *clear* sec impact

@Bugcrowd I'm convinced you disrespect research, and your analysts don't read. I think I'm done hunting anything bugcrowd!


6
17
3,217


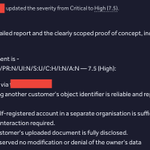
Some PDFs that were not mine ended up in my account.
A short writeup from a bug bounty finding I got rewarded for this year.
saurinn.github.io/blog/every…


People that talk like this either have tested their stuff in a vm using wep or are watching too many Hollywood movies.
I mean I know there are some holes in modern protocols but hacking a wifi net externally without phishing it's hard

wifi hacking shouldn’t be this vulnerable in this era, aircrack, wireshark, kismet are sitting right there in kali linux bypassing with free will
272
manuel valdez⛩️ retweeted

Many of the CVEs you see coming out these days are actually not very weaponizable against real production systems, for one reason or another
Example: Anthropic’s recently reported Linux network RCE, which takes almost an hour to run, causes a kernel panic on any system that has even the default level Linux Firewall, in our testing
Often, the reason why you have even of these these bugs is because firms put them in the throwaway conference-talk category
Important to keep this in mind
manuel valdez⛩️ retweeted
good morning slop enjoyers, ready to post non-functional php2shell exploits and good morning everyone who tries to steal the spotlight of those who deserve the credit


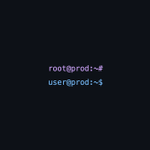
I pressed a test button and got two shells: ~#, ~$.
The connectivity check was handing my input to curl inside a shell, and so was a second feature. One was graded Exceptional at got a max payout for it,
via @intigriti.


