

Helping teams build secure applications, APIs, and AI systems.
Earth
Joined October 2019
- Tweets3.1K
- Following111
- Followers550
- Likes1.3K




#n0n gave Visa & JPMorgan Chase a 48-hour deadline.
That is about half the group's usual window.
Visa blames a third party provider in Asia Pacific. JPMorgan blames a software bug.
Neither confirms a breach. n0n has shown zero proof.
Details: secureblink.com/threat-feeds…
#Ransomware #Exploit #Cyberattack #Dataleak #Fintech #Visa #JPMorgan #ChaseBank #Threatfeed #SecureBlink

149
Optimizely's own trusted CDN served the malware.
178 organisations were hit, including BBC, Zoom, HSBC, and Ledger.
The attacker rebuilt the payload 26 times in one day.
Details: secureblink.com/threat-feeds…
#Optimizely #Exploit #CryptoTrading #Blockchain #Hack #Threatfeed #SecureBlink

1
94
4,837 #GitHub accounts.
61,764 repositories probed. #wfxloot's real move: rewriting the #AWS and #Azure trust policies underneath the cloud sessions it steals, so rotating the leaked secret changes nothing.
Details: secureblink.com/threat-feeds…
#GitHubCopilot #AppSec #CloudSecurity #malwareamy #exploited #Threatfeed #SecureBlink

1
43
Microsoft 365 went down on Nov 12: Exchange Online, Teams, #SharePoint , Copilot and Defender XDR all hit together.
Not a traffic spike. Servers failed their own health checks. 🔁
Two days earlier, a CVSS 6.5 Outlook #zeroday was patched. 🔍
Details: secureblink.com/threat-feeds…
#Microsoft365 #CybersecurityNews #outlookoutage #Microsoft #Appsec #Threatfeed #SecureBlink

1
187
#Maersk's early findings suggest no sensitive data was disclosed.
#WhiteArmor claims 16,093 plaintext driver passwords and 33 superadmin accounts.
Its $5M ask reportedly matches a 19 GB victim's. Maersk: 100 GB claimed.
Data or brand: what sets the price? 🔍
Details: secureblink.com/threat-feeds…
#accessmanagement #Exploit #Hack #databreach #cyberleak #Threatfeed #SecureBlink

163
Two 2026 N-central flaws sit on the KEV list. The headline's "dozens" of #Able2Shell zero-days is unconfirmed.
Details: secureblink.com/threat-feeds…
#ThreatIntel #ZeroDay #Vulnerability #RemoteAccess #Threatfeed #SecureBlink

26
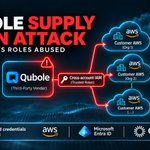
The #Qubole supply chain attack did not need an #AWS flaw.
Every assumed role carried a valid External ID, and every attempt succeeded.
Wiz says one control alone would have blocked them all. It was not the External ID. 🔍
Details:secureblink.com/threat-feeds…
#CloudSecurity #SupplyChainAttack #Hack #Threatfeed #SecureBlink

1
48
One password inside Wyndham’s Android app opened a Salesforce hosted database.
Names, emails, member numbers. And login tokens.
Wyndham says no evidence of unauthorized access.
It hasn’t said whether it has the logs to check. 🔍
Details: secureblink.com/threat-feeds…
#Databreach #Salesforce #Android #Hack #Wyndham #Threatfeed #SecureBlink

43
DreamHost had an attacker in its File Manager for ~10 weeks (Aug to Oct 23).
Stolen: FTP/SFTP passwords and webmail session tokens.
A stolen session skips login, so MFA never gets a say.
On DreamHost? Rotate creds and file secrets, check for planted files and mail forwarding rules.
#DataBreach #InfoSec

Full breakdown and remediation checklist 👇
secureblink.com/threat-feeds…
19
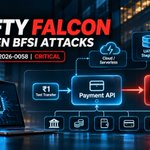
🦅 CERT-In just named a new AI-assisted threat actor: CRAFTY FALCON.
It doesn't break payment systems. It asks them to pay.
4 AI tools. 9 behaviors. One ₹1 transaction gives it away.
The part nobody is talking about 🧵
#CERTIn #CyberSecurity

1
1
62
🛠️ Four public AI tools are named. Seeing them on a network tells you the method, not the operator. Attribution stays open.
1
6
🔁 Some victims were hit again after they thought they had fixed it. That detail says more than the tool list.
Full #ThreatResearch from the #SecureBlink Threat Intel Lab 👇 secureblink.com/threat-resea…
#CraftyFalcon #AI #API #Fintech #payments

9
An external actor used offensive agentic techniques to reach internal tools this October. The exposed data is limited. The open questions are not.
Exposed: user IDs, full names, email addresses, organization role labels. Not reported as accessed: clear-text passwords, MFA secrets, session tokens, investigation content. The scope is “based on evidence to date.”
Who is behind it, and how many customers were hit?
Details: secureblink.com/threat-feeds…
#Exploit #Chainalysis #Hack #ArtificialIntelligence #AgenticWallet #Threatfeed #SecureBlink

Binance says no private key leaked.
It lost about $6.3B in roughly 20 minutes anyway.
Wallets on 10+ chains signed for the attacker. Binance hasn't said how. 🔍
Details: secureblink.com/threat-feeds…
#Binance #NorthKorea #CryptoSecurity #Blockchain #buyingcontent #Hack #Bitcoin #Threatfeed #SecureBlink

Sony says no passwords leaked in the So-net breach.
It also says 54,401 mailbox passwords did.
Customers who left by February 2026 aren't in the data. Customers who left in March are.
Sony hasn't said why. 🔍
Details: secureblink.com/threat-feeds…
#Japan #databreaches #hack #exploit #NTT #CyberAttack
🤖 Made with AI

1
81
Warp: ~1% of users, an unnamed vendor, "agent traces." Its docs list two very different data types under that label.
Warp has not said which. secureblink.com/threat-feeds…
#AIAgent #Exploits #Coding #ArtificialIntelligence #Threatfeed #SecureBlink
🤖 Made with AI

1
2
69