

Faculty @uutah. My lab hunts bugs: https://teapawt.org/t.co/R74Wl128A9. Mastodon: [email protected] Bluesky: https://teapawt.org/t.co/6sKvEYpXMF
Salt Lake City, UT
Joined August 2018
- Tweets1.3K
- Following1.6K
- Followers1.3K
- Likes6.3K





Pinned Tweet
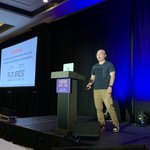
Super proud of the FuTURES³ Lab and everything we accomplished in 2025, and excited for what’s ahead in 2026! Check out our work at futures.cs.utah.edu. 😃

Stefan Nagy retweeted

haha, so apparently OpenAI are about to start training on your Daybreak Blue sessions, with no way to opt out.
Literally stealing people's private work, as they do it, is cartoonishly evil.
It also will presumably kill Daybreak usage by security researchers. Or at least, it should. The thing OAI have had to swear they are not doing to math researchers, they are now explicitly about to start doing to security researchers.
Yet another reminder of the importance of open models.
Stefan Nagy retweeted
very excited for mythos to tell the sysadmins that exposing the PLCs to the internet is bad

EXCLUSIVE: Sam Altman met with top power utilities to discuss ways to secure the electrical grid.
He also offered one possible solution to the cybersecurity risks: OpenAI’s own cyber services.
politico.com/news/2026/09/10…

Stefan Nagy retweeted

ELI5 why corporate AI companies get to run cyber attacks on real-world systems with zero consequences


En route to Montreal 🇨🇦 @FSEconf!
On Wednesday, FuTURES³ Lab researchers @yeaseen_, @yangzaocn, and @gabe_sherman6 will present their three papers on invariant-guided binary fuzzing, LLM-driven transpiler testing, and Python auto-harnessing.
Papers/code: futures.cs.utah.edu


Stefan Nagy retweeted

Dyn Taintflow Analysis (DTA) - one of the main components of VUzzer (NDSS 2017) - finally got the re-engineering I'd been postponing for years.
Several ideas had been stuck in my notebook ever since. 1/n
Stefan Nagy retweeted

The fuzzer that found project-zero.issues.chromium… (and a number of issues prior to that as well) is now open-source: crrev.com/c/7580844
It uses pkeys, trap-handling and single-stepping to intercept and mutate in-sandbox reads (see trap-fuzzer.h). Definitely had fun writing it!
Stefan Nagy retweeted

I have a job opening on my team. If you're interested in incident response & software security across a wide range of industries (Laptops, Auto, Mobile, Datacenter) while working with very talented people please apply. DMs are open for questions*.
careers.qualcomm.com/careers…
Stefan Nagy retweeted
ZeroDayBench: Evaluating LLM Agents on Unseen Zero-Day Vulnerabilities for Cyberdefense
arxiv.org/pdf/2603.02297


Awesome to see @yeaseen_'s work on transpiler testing recognized by the Go2Hx dev community! community.haxe.org/t/go2hx-w… 😁
Interested in improving transpilers? Check out our fuzzer TeTRIS!
Paper: futures.cs.utah.edu/papers/2…
Slides: futures.cs.utah.edu/papers/2…
Code: github.com/FuturesLab/TeTRIS

Stefan Nagy retweeted

TeTRIS uncovered 16 translation bugs across real-world transpilers—12 of them completely new!

Stefan Nagy retweeted
Transcompiler lost in translation? Let TeTRIS uncover all its syntax frustrations!
Happy to share my @ACSAC_Conf paper w/ @snagycs: "TeTRIS: General-purpose Fuzzing for Translation Bugs in Source-to-Source Transpilers"!
PDF:futures.cs.utah.edu/papers/2…
Code:github.com/FuturesLab/TeTRIS

Crashing calculators and CAD editors? GUIFuzz++ is finally here to help make them better! 🔥
Come see my undergraduate student @trowlett0's very first paper "GUIFuzz++" at #ASE25 this Wednesday.
Also now integrated in AFL++! 😃
github.com/AFLplusplus/AFLpl…


Stefan Nagy retweeted
This is an excellent history of LLMs, doesn't miss seminal papers I know. Reminds you we're standing on the shoulders of giants, and giants are still being born today. gregorygundersen.com/blog/20…
Stefan Nagy retweeted

#FUZZING'26 CALL FOR PAPERS
──────
✨After 5 years, we will be again co-located with NDSS!
🔗 fuzzing-workshop.github.io
📅 11. Dec (Submission)
//cc Marcel Böhme (@mboehme_; MPI-SWS), @RuijieMeng (CISPA), Rohan Padhye (@moarbugs; CMU), László Szekeres (@lszekeres; Google)

Super psyched to unveil GUIFuzz++: our grey-box fuzzer for desktop GUI applications, led by FuTURES³ Lab undergraduate researchers Dillon Otto and @trowlett0.
Coming soon to @ASE_conf'25!
futures.cs.utah.edu/papers/2…
github.com/FuturesLab/GUIFuz…

Stefan Nagy retweeted

GUIFuzz++ is the first general-purpose fuzzer for desktop GUI software! Fuzzing by translating AFL++ random input into user interaction with GUIs, leading to the discovery of 23 new bugs!
Paper: futures.cs.utah.edu/papers/2…
Source: github.com/FuturesLab/GUIFuz…
Go test some GUIs!
