

Your Eyes Beyond 👁 | Transform Your Risk Perspective
Middletown, DE 19709, USA
Joined May 2018
- Tweets4.3K
- Following25
- Followers7.2K
- Likes150





Node2Shell reaches Python too.
CVE-2026-111497 (Brotli decoder OOB write) ships in PyPI's Brotli and brotlicffi, which requests, httpx, and aiohttp use automatically.
→ Upgrade to Brotli 1.2.1 and brotlicffi 1.2.1.0
→ Rebuild images, restart workers
Affected versions, exposure paths, and mitigations: hubs.la/Q04CgKJ50
#AppSec

5 new dark web claims, from 400GB for sale to plaintext passwords:
→ Finaxis.()cloud: 400GB
→ WoWInstaller: ~1.21M records
→ Argentine Moodle site
→ MyHairCare Australia: ~1M records
→ HT Médica: 2.2M records
Mostly Unverified. Full breakdown: hubs.la/Q04CgCcc0
#DarkWeb #ThreatIntelligence #CyberSecurity
#DarkWeb #ThreatIntel

Who else is logged into your company's AI accounts?
Your developers, marketers, and analysts use AI tools every day. When infostealer malware lands on a device through a cracked file or a fake update, it collects browser passwords, cookies, and active session tokens.
Those logins get bundled and sold on the dark web, along with access to:
→ Full chat histories
→ Internal contracts and NDAs
→ Source code and roadmap docs
→ Customer lists and financials
SOCRadar's free AI Exposure Checker scans your domain to surface exposed accounts earlier.
Check your domain: hubs.la/Q04CfNKR0
#CyberSecurity #DarkWeb #ThreatIntelligence
10 stories from the last 24 hours in cyber: an actively exploited VeloCloud zero-day, 2 unpatched Linux KSMBD flaws, and what your team should do about each.
#ThreatIntelligence #CyberSecurity #VulnerabilityManagement

An exposed attacker server held working PHP2Shell exploit tooling: a one-click RCE chain for PHP 8.4.26 on Apache mod_php, scanners run against about 20 public sites, and WordPress recon on 5.
No shell access found. Patch PHP anyway. hubs.la/Q04C6zrC0
#ThreatIntelligence #PHP

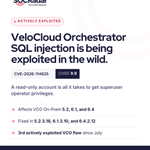
CVE-2026-114625 (CVSS 9.9) is actively exploited in on-prem VeloCloud Orchestrator. Enterprise Read Only access is enough to reach local superuser.
→ Attacks from 74.82.197[.]86, 38.54.50[.]151
→ Upgrade to your branch’s fixed VCO release
Affected versions, hunt guidance, and remediation steps: hubs.la/Q04C6xBC0
#VeloCloud #SDWAN

Most ransomware doesn't start with a hack. It starts with one clicked link.
Here's how the chain actually plays out:
→ Phishing email delivers access
→ Access sold to a broker
→ Affiliate escalates and moves laterally
→ Data stolen, then encrypted
Our Threat Actors glossary breaks down who does what in this chain. hubs.la/Q04C65lJ0
#Ransomware #Phishing


PHP2Shell: 2 RCE flaws in PHP core, both CVSS 9.2.
Check if your site’s PHP version is exposed. The check is passive, free, and needs no signup. hubs.la/Q04B_qQQ0
#PHP2Shell #CVE
eMudhra exposed 8 intermediate CA private keys via weak P-384 key generation.
→ 6 TLS: forged certificate risk
→ 2 code signing: trusted-looking malware
Browsers block the chains. CI/CD, containers, and embedded devices may not.
Breakdown in comments.
#PKI #CyberSecurity

Learn more: socradar.io/blog/emudhra-ca-…

An exposed C2 server shows how INC and The Gentlemen affiliates ran intrusions:
→ 8,257 AI messages, 133 sessions
→ 32 MCP servers, recon to ransom pricing
→ 62 named victim orgs
Entry points? FortiClient EMS, SimpleHelp, and reused passwords.
Link in comments.
#Ransomware #INCRansomware #ThreatIntel

SOCRadar® retweeted

SOCRadar found INC and The Gentlemen affiliates using LLMs in intrusions and extortion. Seven servers held 8,257 AI messages and 46 encryptors staged for six victims. socradar.io/blog/inc-gentlem…

SOCRadar® retweeted

⚠️📢 Newly exposed records show INC and #TheGentlemen ransomware affiliates are using Claude and Kimi to plan attacks. Researchers recovered 8,257 AI messages, stolen credentials and 46 encryptor builds from the servers.
Read: hackread.com/inc-the-gentlem…
#Ransomware #Cybersecurity

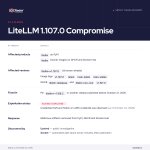
LiteLLM 1.107.0 (PyPI and matching Docker images) shipped a credential stealer via stolen maintainer tokens. It targets cloud keys, AI provider secrets, and proxy data. Stolen AWS creds are already in use.
→ Pin to 1.106.2
→ Rebuild
→ Rotate secrets
IoCs: link in comments.
#SupplyChain #LiteLLM


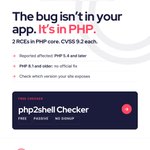
PHP2shell: 2 RCEs in PHP itself (CVE-2026-109618, CVE-2026-109619, CVSS 9.2 each). PHP 8.1 and older get no official fix.
→ Free checker reads the PHP version your site exposes
→ Passive: no exploit attempts, no signup
Check Exposure: hubs.la/Q04BVKFC0
#PHP #VulnerabilityManagement #ThreatIntelligence

SOCRadar logged 134 Japan dark web news items from Oct 1 to 15, more than in all of September.
AI helped. The weak spots were already there: suppliers, member APIs, and old web systems. A single IDC Frontier incident reached 495 customer organizations.
Link in comments.
#ThreatIntel #Japan

