

Seeker-first onchain intelligence Built by @crashdiniz 🇧🇷 - CMO @sabadinhos_
Solana Mainnet
Joined February 2026
- Tweets71
- Following138
- Followers81
- Likes74




SolSentry retweeted

a quick reminder that @colosseum had a grand total of 2,973 submissions this year.
there's never been a better time to build.

APK 0.1.22 is now public, with source (MIT): github.com/solsentry/solsent…

SolSentry retweeted

I investigated this drain
Total stolen: $3.72M (prices after conversion)
Likely culprit seems private key compromise
All transfers were signed by this wallet key. Seemed like a semi automated drainer, some networks drains were scripted, while Solana appears to have been manual


Adding to @WazzCrypto's trace of the @frogmanhaha drain. We reached the same @HyperliquidX endpoint independently. A few things not covered yet:
1/ All ~$2.2M sitting as XMR1 across 41 Hyperliquid accounts is still NOT redeemed (as of 01:00 UTC). Turning it into Monero has to go through Wagyu.
2/ Wagyu doesn't need a court order to stop that. Their own policy: blocking an address "does not involve the freezing or seizure of Assets". Only freezing requires a court order. @PerpetualCow
3/ Timing: the attacker started staging gas 22 min after a 1.43M $BP withdrawal landed in the wallet, and the drain followed 11 min later. They were likely watching it.
4/ We're tracking every XMR1 account live and will flag any redemption the moment it happens.
Live tracker: solsentry.app/drains/frogman…
Fund-flow graph built on Haradrim by @mert, data via @Helius 🙏

lets try! 😈

Cloak mainnet is live.
Onchain finance shouldn't mean public finance.
Cloak keeps your balances, amounts, and counterparties private, while letting you prove exactly what matters to exactly the people who need to see it.
Private by default. Auditable when required.
⚡ 0% protocol fees on USDC transactions for launch week.
cloak.ag/privacy
🚨 ACTIVE EXPLOIT — Avici (@Avici), Solana neobank
User card-collateral is being drained on-chain RIGHT NOW — ~$652K taken so far across ~828+ vaults, and still climbing. (Briefly paused ~18:23 UTC, resumed 3 min later.)
The stolen USDC/USDT is STILL in the attacker's wallet, not yet moved — recoverable if frozen fast:
FVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj
@Avici — pause the program now.
@zachxbt @SlowMist_Team @PeckShieldAlert @cantinasecurity @m4rio_eth flagging for freeze coordination w/ Circle & Tether.
Verified on-chain by SolSentry. Technical details shared privately with the team.
UPDATE — the attacker has started cashing out.
Trail (all verified on-chain):
1. Drained victim vaults → USDC/USDT
2. Swapped ~$618K USDC → ~5,970 SOL via an RFQ fill (tx 2aZ26BQ…)
3. Consolidated ~10,000 SOL to a fresh hop wallet: MsaXH6cGDahPQDwJjFYod7RW8QLVDZGByywWvwQ9TFu
4. That wallet swapped via Jupiter + bridged the SOL OFF Solana via deBridge DLN (tx 4pmHmZD8…)
The initial gas was ALSO bridged IN via deBridge — cross-chain on both ends. The stablecoin-freeze window has largely closed; the loot is now SOL moving cross-chain.
Arkham has no label on the attacker wallet, the hop, or the deBridge solver — fresh, unlabeled infra.
The lead now: deBridge can resolve the source/destination chas the identity trail.
Still monitoring live. Attacker: FVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj
#Changelog · Jul 8
Shipped: coordination scoring now separates shared bot/router infrastructure from genuine operator coordination — fewer false "cluster" signals on operator risk.
Live (auditable): 96,166 predictions · 92.9% accuracy · 97.8% precision on CRITICAL · 71,187 confirmed rugs · ~86 days mainnet.
Full log: solsentry.app/changelog · per-mint audit: /v1/predictions/{mint}. No key, no signup.

Our founder's counterparty-gate won a slot in the @SuperteamBR Solana AI Kit bounty 👏
Same thesis we run live: don't ask "is the code safe?" — ask who deployed it, and what they've rugged before. 97.8% precision on CRITICAL, auditable per-mint.

Woke up happier today 🔥🚀
Out of 329 builders, my skill was one of the 10 winners of the @SuperteamBR Solana AI Kit bounty.
Counterparty-gate checks what auditors skip: not "is the code safe?" but "who deployed it — and what have they rugged before?"
Loved sharing this with the BR crew 👊 @raffxsolana @blchead @sou_foka — @SuperteamBR is a genuine cheat code.
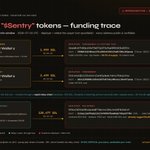
~30 hours later, all three fake "$Sentry" tokens are dead.
On-chain, right now:
→ Token 1 (pump.fun): 97.5% of supply sold back into the bonding curve. 9 wallets still holding. 0.7 SOL left.
→ Token 2 (pump.fun): 92.6% back in the curve. 2.2 SOL left.
→ Token 3 (SPL): liquidity gone since launch day.
That's how a 93.7%-concentration bag ends. Every mint is in the quoted post — verify it yourself.
Next: we're putting the full forensic trail — funding paths, relay hops, holder timelines — on a public page, so anyone can cross-check these wallets themselves. The graph is still growing as we trace more.
SolSentry has no token.


Earlier today, while I was AFK, someone launched three fake "SolSentry / $Sentry" tokens — our exact name, our logo (same IPFS file), our description copied word for word. All three minted inside a 19-minute window.
Let me be unambiguous: SolSentry has NO token. I didn't launch anything. There is no CA. If we ever launch one, it will be announced from @solsentryai first, nowhere else. Anything called "$Sentry" for sale today is an impersonation.
I promised the full on-chain trace. Here it is — pulled with SolSentry itself, the product these people cloned.
— THE THREE FAKES (do not buy, report on sight) —
1. 33NBdCKiD4Mmooi93u2hDKcEASUh19gHC3KBaJhQpump (pump.fun)
2. 6DSnjCM2WDKsZnBnk1W37mDT6GzyRKesxzJdm4XTpump (pump.fun)
3. Zz2wqzjaUFPgXp3jhjfdf895K75pmWwQzTbUga3TYMd (SPL)
All three: same stolen logo (identical IPFS CID), same description verbatim, 1B supply.
— WHO DEPLOYED THEM —
We resolve deployers by oldest fee-payer — chain history, not spoofable metadata.
Token 1 → 2wsmdkcK7nNXpvhEm73mDT2pCFGy9qwSRD26EDaUEECn
Token 2 → CXvLwta1QEz1ZExk14ry1wn81pGpmLYdniv7bkqicVsy
Both are fresh throwaway wallets — the first has 3 transactions in its entire life. And both were funded by withdrawals from the SAME Binance hot wallet, 8 minutes apart: 1.999 SOL at 02:26:10 UTC, 3.499 SOL at 02:34:06 UTC. Same source, same script, back to back. That's one operation.
Token 3 → 8fbSxZHZCwb5RLdpodqNTY8pre4J38yrknSSF8aYmCsf
Different path. It received 120.477 SOL at 02:44:48 UTC from B45FWB9i3pBRv5rGM5tnzk8uBq8TJoSdtYqMV6Z6xKom. B45F isn't a person's wallet — it's a relay: it received 119.93 SOL and forwarded 120.48 SOL twenty-three seconds later, and it repeats that same ~150-SOL hop every ~20 minutes, all night long, feeding multiple scam-token deployers. Our deployer took the 120.5 SOL in, minted the clone, sprayed dust to ~20 wallets to fabricate "holders", and drained ~119.5 SOL back out through the same relay chain.
To be precise about what's proven: the funding ties tokens 1 and 2 together. Token 3 came through a different funding path — the stolen logo and copy tie it by intent, not by wallet. I'm not claiming one person for all three.
— WHERE THEY STAND RIGHT NOW —
• Token 3 is already dead. Liquidity at $0, 99.9% of supply parked in the pool authority. Anyone who bought is holding nothing.
• Token 1 is a loaded gun: one wallet (9569PA1rf4G7…jRq71) holds 937M of 1B — 93.7% of supply, 14 holders total. When that wallet moves, that's the rug. We're watching it.
• Token 2 barely got off the ground.
— WHAT TO DO —
• Don't buy anything called $Sentry. There is no real one.
• If you bought: stop, and report the mint on pump.fun and Solscan.
• If you see an account shilling these mints, report it for brand impersonation.
I've reported all three mints and flagged the two Binance withdrawals to their fraud channel — the exchange is the one entity that can put a real name on those wallets.
One last thing. Tracing deployers back through their funding chains is literally what SolSentry does — 97.8% precision on CRITICAL calls, auditable per-mint at api.solsentry.app/v1/predict…{mint}. The people who cloned us picked the one project that ships the tool for tracing them.
The system doesn't sleep. Apparently neither do they.
x402 let AI agents pay for APIs in USDC on Solana. Every security service on it answers the same question: "is this token safe to trade?"
SolSentry answers a different one — "who keeps launching the unsafe ones?"
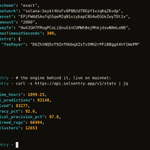
Operator risk is now payable per-call: an agent about to sign a tx pays ~$0.002 to check whether the deployer is a serial rugger, before it acts. Live at api.solsentry.app/x402/v1/* — settled on-chain (x402 / CDP facilitator). Free /v1/* tier unchanged.
The engine behind it has run on Solana mainnet 1,899 hours:
• 93,148 predictions total · 83,277 resolved · 92.6% aggregate accuracy
• 97.8% precision on CRITICAL — auditable per-mint at /v1/predictions/{mint}
• 66,994 confirmed rugs traced · 12,653 bot clusters mapped
• 23,480 wallets associated with confirmed-rug mints
x402 already has token scanners. We're the only operator-risk service we've found on it — scoring the wallet behind the deploy, not just the mint.
Agents shouldn't sign blind. @solsentry/mcp on NPM · no key, no signup.
cc @CoinbaseDev @solana #x402
Proof, not a slide. That's the actual quote an agent gets back before any data — USDC, Solana mainnet, ~$0.002, settled on-chain. Try the engine free first at /v1/* · @solsentry/mcp on NPM, no key, no signup. api.solsentry.app
