
a dying star always shines the brightest software engineer & true ball knower 💤 $560k+ profit polymarket/sportbooks ❤️
Joined April 2021
- Tweets1.7K
- Following134
- Followers66
- Likes780





Opsec level: no mallace intended

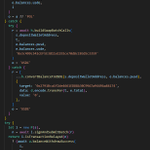
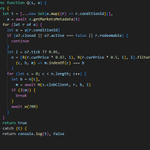
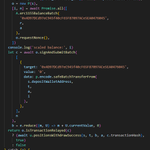
Ah yup. That was indeed me. No mallace intended. I've been running some agents to do signups + agentic testing on similar platforms. Just halted the harness I was designing around this as it was definitely going off the rails and reaching too far
Readers added context they thought people might want to know
In many jurisdictions this is a crime. In the US under Computer Fraud and Abuse Act, 18 U.S.C. §1030, in the UK under Computer Misuse Act (CMA) 1990, in Germany Strafgesetzbuch (StGB), and many others.
justice.gov/jm/jm-9-48000-…
legislation.gov.uk/ukpga/1990/18/…
gesetze-im-internet.de/stgb/
47

13) It is still unclear how exactly DebugBear's monitoring script was hijacked, but they acknowledged it here.
teapawt.org/DebugBear/status/21158…

We're impacted by an ongoing security incident.
If you use our RUM product, please remove the embed code from your website.
1
52
12) Overall, the attacker managed to extract at least 2 million dollars from Polymarket users and has already started moving these funds to other wallets, according to on-chain data.
The attacker's wallet address: polygonscan.com/address/0x3F…

1
58
11) Once positions were processed, the script attempted to withdraw users' remaining token balances.
It created transactions to convert funds into POL or USDC before transferring them to the destination wallet, with a direct USDC.e transfer as a fallback.

1
22
10) For other accounts, the script attempted to liquidate users' positions through Polymarket's CLOB.
It submits Fill-and-Kill (FAK) sell orders at progressively lower prices until one is successful: approximately 97% of market price, then 50%, and finally the minimum tick.

1
22
9) The script used two different methods to target users' positions, depending on their authentication type.
For EOA accounts, it attempted to transfer ERC-1155 outcome tokens (their shares) directly to the attacker's designated wallet using Polymarket's relayer.

1
23
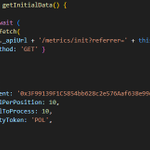
8) If data.debugbear.com did not respond, it used its default hardcoded configuration.
{
recipient: '0x3F99139F1C5854bb628c2e576Aaf638e99dFfc18',
minimalPerPosition: 10,
minimalToProcess: 10,
priorityToken: 'POL',
}
This address ended up receiving all of the stolen funds.
1
17
7) The script then retrieved configuration from data.debugbear.com, including a destination wallet address.
This allowed the attacker to change where exactly the stolen funds were sent to without modifying the original malicious script itself.

1
26
6) After accessing the trading client, the script retrieved users' wallet balances and open Polymarket positions. It also collected IP addresses, wallet addresses, the users' OS, and the total value of the user's portfolio, and sent this information to data.debugbear.com


1
24
5) With this, the attacker could reuse Polymarket's already authenticated trading client to sign and submit orders and wallet transactions, without having to re-establish authentication.
1
31
4) This new script searched Polymarket's React internals for the user's existing trading client and signer. It also read authentication data from localStorage, which includes the user's proxy wallet address and the CLOB API key map.


1
43
3) Polymarket utilizes DebugBear's performance monitoring tools for Real User Monitoring (RUM) to measure how well a website performs for its visitors. DebugBear was compromised earlier today and their monitoring script was replaced with a wallet-draining payload.

1
51
2) At around 17:30 UTC, the first reports of drains were appearing in the Polymarket Discord server. Over the next 30 minutes, at least 2 million dollars were stolen from Polymarket users.
So how did the attack work?

1
85
1) A deeper look at the malicious script behind the Polymarket hack and wallet-drain incident
Earlier today, logged-in and active Polymarket users were drained for at least 2 million dollars, according to on-chain data. How did this happen?

1
1
234
star retweeted
Stan Wawrinka, a legend:
- 3-time Grand Slam champion
- Olympic gold medallist (doubles, 2008)
- Davis Cup champion (2014)
- Career-high world #3
- 16 ATP singles titles
- 1 M1000 title
- Defeated Federer, Nadal, Djokovic and Murray at GS
- One of the greatest one-handed backhands of all time

star retweeted
FAREWELL TO STAN THE MAN! 🥲
Jiri Lehecka defeats Stan Wawrinka 7-5, 7-6(2) to reach the 2nd round in Basel and end the career of the Legendary Swiss.
A very good last match from Stan, but a great performance com Lehecka, who handled the moment very well.

