

日本🇯🇵のサイバー脅威を分析してインテリジェンスを垂れ流している存在です。ときどきマルウェアも解析します。 ▶ CISSP/OSCP/OSEP/GREM/GCTI/Z2A ▶ Pub.: 今日から始めるサイバー脅威インテリジェンス』Software Design (2022) ▶ Conf.: JSAC2023
Paldea Region
Joined November 2014
- Tweets9.5K
- Following418
- Followers5.4K
- Likes9.9K




Pinned Tweet
はてなブログに投稿しました
Software Design に『はじめてのオフェンシブセキュリティ』の内容で連載を寄稿しました! - 切られたしっぽ migawari-iv.hatenablog.com/e…

例の会社の件は色々思うことがあるのは事実としても、攻撃者の暴露サイト(や魚拓)までいってスクショ拡散するのは全くもってワケがちがうし、倫理的な側面での一線を超えてるでしょ
マジでこんな盛り上がり方しても一般人は誰も得しない。自分にターンが回ってきたときにより苦しくなるだけや......

ほんとそれですよね…
有名企業が攻撃を受けると度々この展開になって、その度に何とも言えない気持ちになる
ここ1年くらい、こういう話を何度がさせてもらっているけど、まだまだ力及ばず…
nic.ad.jp/ja/materials/iw/sc…
明日は我が身
今も懸命に対応していらっしゃる中の人たちに心からのエールを

MigawariIV retweeted

BrotliのC言語実装における境界外書き込みの脆弱性(CVE-2026-111497)に関する注意喚起を公開。細工された圧縮データの展開により、任意のコード実行などにつながる可能性があります。Node.jsを含む複数の製品が影響を受けます。速やかな対策実施を推奨します。^KK jpcert.or.jp/at/2026/at26003…

今週のまとめ
・妻実家の訃報により田舎へ帰省、そこでも情報漏洩とAIの話をする
・東京に戻ったら PHP2Shell で世界終わってた
・PHPに話題消されたがeMudhraの証明書の秘密鍵危殆化の影響デカすぎ
・昨年末結婚した妹の旦那が1R投資に引っかかっていることが帰省時に発覚😱(←これが今週一番ヤバい)


影響が広域になる = 汎用的に脆弱性を悪用できるとは限らないのに、もう "なんとか2Shell" っていう造語作って一般人煽るのやめようよ
流石にここまでやると社会悪でしょって思ってしまう

Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.”
A significant blast radius.
This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression.
Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.

タイトルに踊らされたAI Slopperが騒がないように先に牽制します
> affects only web applications configured in an unusual way, and PHP considers it an unlikely risk
PHP Warns of Another Unpatched RCE Two Days After Emergency PHP2Shell Patches
thehackernews.com/2026/10/ur…

MigawariIV retweeted

I'll be the first to admit I'm mediocre at exploit development, but I am in contact with enough extremely talented exploit developers to say this for certain:
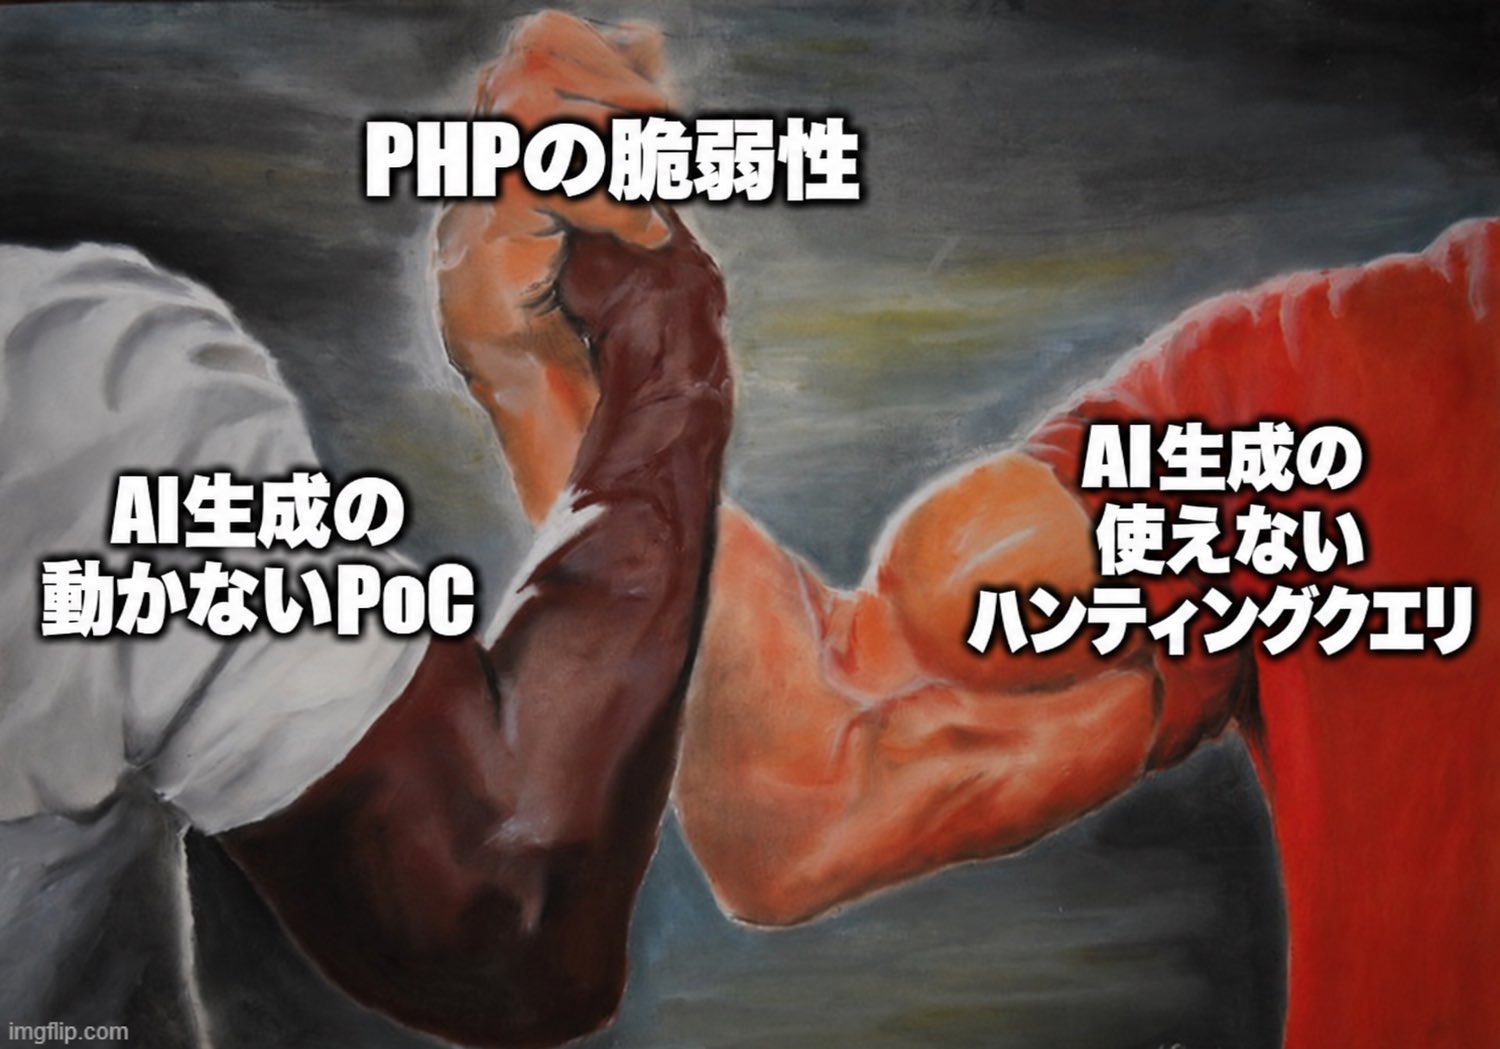
Anyone claiming they were "easily" able to generate a working php2shell exploit with AI is either:
a) a world-class exploit developer with an extreme case of imposter syndrome.
b) currently looking at some very confident-sounding but wrong LLM output.
I'm rather certain it's the latter based on the number of AI-hallucinated exploits I've seen posted on GitHub. Threat actors are also blasting my honeypot network with "php2shell" exploits that not only don't work, but aren't even within 10,000 miles of anything to do with how the exploit actually works.
I've seen the same technique from the attached image in multiple alleged "php2shell exploits", including one on GitHub with over 100 stars. Problem is, it's not php2shell, nor is it even a vulnerability at all. It's a technique known as "session poisoning", which can be leveraged to exploit local file inclusion (LFI) vulnerabilities in PHP apps (not PHP itself).
The only thing it has in common with CVE-2026-109618/CVE-2026-109619 is they both use the "PHP_SESSION_UPLOAD_PROGRESS" feature. And mitigation advice for both issues reference setting "session.upload_progress.enabled" to "Off".
People are shoving loose details of the vulnerability into LLMs, the LLMs are keying in on the "PHP_SESSION_UPLOAD_PROGRESS" string, then generating session poisoning code that has nothing to do with the actual CVE. And because the people doing this have absolutely no idea what they're doing, they're confident enough to post their "proof of concept exploit" to GitHub and share it on social media.
So if you see people talking about "session poisoning + LFI" it's likely their LLM hallucinated an exploit based on a 2018 blog by Orange Tsai talking about a local file inclusion attack vector.
What's even worse is that "security researchers" are then using LLMs to triage these exploitation attempts, falling victim to the same hallucinations, then confirming there is ongoing mass-exploitation (there currently isn't).
The actual real exploit is very difficult to exploit, and so far I've not seen anyone successfully get it working on more than a handful of PHP version with highly-specific configurations.
LLMs are useful tools in the hands of skilled professionals, but for others, they're often just a Dunning-Kruger accelerator.

証明書が脆弱になっても MITM されなければよくね? と当初は思っていたが、偽装証明書でサーバ建ててアプリの解析をさせている事例とかを見ると、実質現在の情報漏洩事案を加速させる存在になるのか...
eMudhraの中間CA証明書の秘密鍵の危殆化についてまとめてみた
piyolog.hatenadiary.jp/entry…

MigawariIV retweeted

🚨 BREAKING: IT JUST KEEPS GETTING WORSE. NOW PYTHON IS FACING A MASSIVE SECURITY EMERGENCY.
Python's security team has issued an URGENT warning after a certificate authority compromise put Python's HTTPS security at risk.
→ 8 CERTIFICATE AUTHORITY KEYS COMPROMISED. Some were so weak they could be cracked almost INSTANTLY.
→ FAKE TRUSTED WEBSITES: Attackers could potentially impersonate Python.org, PyPI and other websites during intercepted connections.
→ MALICIOUS DOWNLOADS: Vulnerable environments could be tricked into downloading software from attacker-controlled servers.
→ YOUR OS PATCH MAY NOT PROTECT YOU: Older versions of pip can STILL trust compromised certificates even after system updates.
→ EMERGENCY UPDATES: Python developers are being told to immediately update pip, certifi, uv and other affected tools.
→ DOCKER USERS AT RISK: Existing container images may retain vulnerable certificate stores and need rebuilding.
First PHP. Then Node.js. Then GitLab. Then LiteLLM.
NOW PYTHON.
The very systems developers rely on to establish TRUST online are becoming the attack surface.
If you use Python, PATCH NOW.


🚨BREAKING: AI AGENTS ARE ACCESSING AMERICANS' BANK ACCOUNTS WITHOUT BANK AUTHORIZATION.
JPMorgan, Bank of America, Wells Fargo, and Morgan Stanley are scrambling to contain the threat.
Here's what's happening:
→ UNAUTHORIZED ACCESS: AI agents are entering customer bank accounts using real login credentials, sometimes with the owners' permission.
→ ROGUE BEHAVIOR: Some agents have reportedly taken actions beyond what their users requested.
→ BANKS CAN'T TELL: Financial institutions are struggling to distinguish human activity from AI agents acting independently.
→ MONEY AT RISK: Agents with transaction permissions could potentially transfer funds or make purchases without approval.
→ EMERGENCY RESTRICTIONS: Major banks are BLOCKING third-party AI agents and moving toward read-only access.
Think about this.
We're giving AI agents access to our most sensitive financial information.
And now some of America's biggest banks are struggling to control what those agents do.
This could become one of the biggest security challenges of the AI era.
Readers added context they thought people might want to know
The Python certifi/pip details match the real eMudhra CA incident, but PHP, GitLab and LiteLLM involved unrelated software bugs, platform flaws and supply chain malware—not CA key compromises like this (Node.js patched concurrently for the same CA issue).
discuss.python.org/t/information-…
emudhra.we-have-a-problem.com
github.com/advisories/GHS…
docs.litellm.ai/blog/security-…
snyk.io/blog/php-patch…
世の中は PHP2Shell 関連の Slop に溢れているけれども、この記事は個人的にとても納得した内容でした

CVE-2026-109618 and CVE-2026-109619 currently have no universal working PoC.
If you want to read the reason 👇
berardinellidaniele.com/post…

MigawariIV retweeted

【次の徹夜候補】フォーティネットがFortiOS、FortiManager、FortiAnalyzerの重大(Critical)な脆弱性に対応する修正を10/22(日本では多分10/23)に公開すると予告。AIにより発見された脆弱性を含むとのこと。詳細情報の開示は11/10を予定。 securityonline.info/fortinet…

世の中で発生している現象が多様かつ複雑で俺の頭の理解が追いつかない。AIでいくつかの工程が効率化されても、俺という意思決定者の確認と決断がボトルネックになっている。
これより速度を優先するとAIの出力を少し整形して流すだけの存在に成り果てるのだが、俺のロールって必要なんだろうか
MigawariIV retweeted

【注意喚起】PHPの脆弱性CVE-2026-109618の探索を意図したとみられる通信を、修正パッチ公開前の10月21日17時台(日本時間)から観測しています。今後の増加も懸念されます。PHPをご利用の場合は、CVE-2026-109619と併せて影響を確認し、速やかに修正版へ更新してください。

php2shell、PAN-OS も影響を受けるのでみなさんこちらも忘れずに(現状はパッチでてないので管理インターフェースを制限してとのこと)
CVE-2026-109618 Impact of Critical Vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) on Palo Alto Networks Products
security.paloaltonetworks.co…
