





Pinned Tweet
Saya mendapatkan reward lebih dari 140 juta dari satu program bug bounty lokal.
Ternyata masih ada perusahaan di Indonesia yang benar-benar peduli dengan masalah keamanan infrastruktur mereka.


termireum retweeted

Good spot and investigation, thank you.
My thoughts: during this window (which has now mostly been closed) —
• Users should not be overly concerned about credit card skimming because most sites use third-party payment portals and their credit card details are not visible to the site or scripts (first-party or third-party).
• Users should not be too worried about account takeover because most sites do sensitive auth in HTTP-only cookies so their session tokens cannot be exfiltrated.
• Users who are on the latest iOS version are unaffected by the iOS exploit in this attack; and most web users don't use cryptocurrencies so are unaffected by crypto address swapping.
• Good security-focused sites use a strong CSP policy that restricts network requests to unknown domains.
My biggest concern would be users who change their password or update sensitive security information during this window, which has now mostly passed. This is because password resets are hosted on a first-party screen, usually on the same site as the main site. Good sites host their auth and login pages on a restricted subdomain of their main site, like account•example•com or login•example•com or auth•example•com. In this case, the account management microsite limits the use of external scripts and third parties.
--
In detail:
First, a good CSP in place would block the malicious network requests for script loading and data exfiltration.
The crypto attack isn't accessing browser extensions (client-side scripts can't, unless it's a 0-day attack). Crypto address swapping by changing instances of the address on the page is really interesting. Good idea for users to check the crypto address in another page and outside the browser.
Card skimming is bad but there are many modern browser countermeasures that defeat this in practice. The vast majority of sites do not host their own payment page; they use third-party payment processors with an embedded iframe or top-level redirect. Client-side scripts at the top (page) context cannot access iframe HTML, JS and DOM context across domains (cross-site violation), meaning they cannot see your credit card details.
Cookie theft is bad but most sites use HTTP-only cookies for auth and session state, rendering them unavailable on the client side.
If you store an auth JWT in local storage or page memory (common for SPAs and OAuth), a malicious script may be able to access the token, but if you have a good CSP that whitelists domains for form actions, fetches and network requests, the session token theft is normally stunted and prevented.
Overall, my strong recommendation is for sites to adopt a good CSP, whitelist domains in the CSP, and limit the excessive and extraneous use of third parties in their supply chain, especially in client-side scripts.


This is a big one.
We found malicious JavaScript being served through Optimizely to some of the world's largest websites.
178 organisations affected, with everything from crypto theft and card skimming to iOS exploits.
Zoom, BBC, CNN, HSBC, Salesforce, GitLab, KLM, IKEA, Equifax, Ledger. The list goes on... Full list in the post.
blog.report-uri.com/worlds-l…

From $1,000 to $10,000: "Limited" XXE to Critical Redis Session Store Exposure. By @00xalr
medium.com/@0xalr/from-1-000…

Critical Unauthorized Balance Top-Up Vulnerability Worth $3,000 by 0xSADAT
medium.com/@0x0sadat/how-i-d…

termireum retweeted

A $3,000 payout for manipulating a single API request! Here is how a researcher exploited a critical business logic flaw to infinitely top-up their account balance without ever completing a payment:
🚨 BUG: Business Logic Flaw / Unauthorized Balance Top-up
THE FLAW:
• The researcher was testing a newly added asset for a private bug bounty program.
• After adding a credit card in the Billing section to access API services, they started monitoring the HTTP traffic.
• They discovered a specific API endpoint (POST /api/credits/top-up) that handled the account recharging process.
• The backend was explicitly trusting the amount and threshold parameters sent directly by the client, instead of securely validating the transaction status from the payment gateway.
THE EXPLOIT:
• The researcher intercepted the top-up request using Burp Suite.
• They modified the amount parameter to a significantly larger value (e.g., 40000) and forwarded the request, completely bypassing the actual payment process.
• The server accepted the tampered values and immediately updated the account balance with the requested credits.
• This allowed any authenticated user to arbitrarily increase their balance and consume paid API services for free, posing a massive financial risk to the company.
STRATEGIC TAKEAWAY:
• Never trust client-side data for financial transactions.
• When hunting, always intercept the exact moment a payment or credit allocation is initiated. If the application is passing the expected top-up amount within the request body, tamper with it—if the backend lacks a secondary payment gateway validation check, you have a critical business logic flaw.
Link to the full write-up in the replies 👇
#BugBounty #AppSec #CyberSecurity #InfoSec #BugBountyTips #BugBountyReports
termireum retweeted

a $3k business logic bug, and notice where it started: a newly added asset on a private program.
recon can't find a logic flaw like this. that takes a human, a logged-in session and burp. what recon can do is get you there first: flag new hosts the moment they show up in scope, and surface exposed API specs that list endpoints like /api/credits/top-up.
that's the split monomi is built around. it finds the new asset and the endpoint, then stops. the human decides what to test.

A $3,000 payout for manipulating a single API request! Here is how a researcher exploited a critical business logic flaw to infinitely top-up their account balance without ever completing a payment:
🚨 BUG: Business Logic Flaw / Unauthorized Balance Top-up
THE FLAW:
• The researcher was testing a newly added asset for a private bug bounty program.
• After adding a credit card in the Billing section to access API services, they started monitoring the HTTP traffic.
• They discovered a specific API endpoint (POST /api/credits/top-up) that handled the account recharging process.
• The backend was explicitly trusting the amount and threshold parameters sent directly by the client, instead of securely validating the transaction status from the payment gateway.
THE EXPLOIT:
• The researcher intercepted the top-up request using Burp Suite.
• They modified the amount parameter to a significantly larger value (e.g., 40000) and forwarded the request, completely bypassing the actual payment process.
• The server accepted the tampered values and immediately updated the account balance with the requested credits.
• This allowed any authenticated user to arbitrarily increase their balance and consume paid API services for free, posing a massive financial risk to the company.
STRATEGIC TAKEAWAY:
• Never trust client-side data for financial transactions.
• When hunting, always intercept the exact moment a payment or credit allocation is initiated. If the application is passing the expected top-up amount within the request body, tamper with it—if the backend lacks a secondary payment gateway validation check, you have a critical business logic flaw.
Link to the full write-up in the replies 👇
#BugBounty #AppSec #CyberSecurity #InfoSec #BugBountyTips #BugBountyReports


termireum retweeted

Bug bounty tip: you found the bug. Now write a report that gets paid.
The triager has never seen your target. They have a queue of reports and a few minutes for yours.
1. Title says what and where. "Any user can read other users' invoices" beats "Critical bug found."
2. Lead with what an attacker can do. How you found it comes second.
3. Steps anyone can repeat. Then run your own steps from a clean session. One missing step and you get "needs more info."
4. Show proof. Screenshots for simple bugs, a short video for complex ones.
5. Impact in plain words. No "might" or "could." Say what you proved, for this company.
6. Be honest on severity. Call a low a critical and your next report gets read with doubt.
7. AI wrote the report? Fine. Retest every step yourself before you submit.
A valid bug with a bad report is still a closed ticket.
#bugbounty
termireum retweeted

I found a critical unauthenticated account takeover that let me log in as any customer on the platform. No password, no account of my own. It earned a $5,000 bounty.
Quick context: the platform runs unattended devices, and those devices sign in with no human present. So instead of a password, each account has an "auto login key." A device presents the key and gets a session. The key is the credential.
That design is fine right up until a key leaks.
The chain came down to 3 things:
- Keys are the credential: by design, holding an account's auto login key gets you a session for that account, no password.
- Wildcard injection: the lookup endpoints ran input through a SQL `LIKE` query, so a single `%` let me pull any account's key out of the database.
- No rate limiting: I could iterate the whole customer table and lift every key.
Here's how I chained them:
1. Leak accounts with a wildcard
The lookup took a `key` and found it in the database with a `LIKE` query. So I sent:
`GET /autologin/lookup?key=%`
Instead of one record, it returned matching accounts: user IDs, tenant IDs, emails. A single `%` dumped account rows.
2. Pull a victim's real key
A second endpoint resolved a key to an account. Same flaw. I sent a wildcard plus an ID I'd just leaked:
`POST /autologin/resolve?key=%`
`{"user_id": {victim-id}, "tenant_id": {tenant-id}}`
It handed back that victim's actual auto login key.
3. Trade the leaked key for a session
The device endpoint does exactly what it's built to do: present a valid auto login key for an account, get a session token for that account. The catch is the key was the victim's, leaked in the steps above, and should never have been in my hands.
`POST /autologin/devices`
`{"user_id": {victim-id}, "key": "{victim-key}", ...}`
It registered my device under the victim's account and returned a fresh session token for them.
4. Full takeover
`GET /me` with that token returned the victim's full profile. PII, billing identifiers, all of it. No authentication, no account of my own, and no notification to the victim that a new device had appeared.
The wildcard enumerated the entire customer table, there was no rate limiting, so this worked against every account on the platform at scale.
#BugBounty tip:
Any endpoint that takes a secret and looks it up is a candidate for wildcard injection. If `%` returns more than it should, it's a `LIKE` query and you can enumerate the table.
Gold Mine

One of the most critical vulnerabilities I’ve found in my bug bounty career! Critical bugs aren’t as hard as most people think—they’re out there, but they require focus and a bit of patience.
At first, I thought I’d accessed data for 80,000 users, but later I discovered it was closer to one million. The data included phone numbers, usernames, and even passwords. More dangerous still: bank card details,all without any authentication.
#Tip
Add swagger/v1/swagger.json to your wordlist and try paths like:
api[.]target[.]com/swagger/v1/swagger.json api[.]target[.]com/api/swagger/v1/swagger.json api[.]target[.]com/{Function}/api/swagger/v1/swagger.jsn
E.G.:
api[.]target[.]com/admin/api/swagger/v1/swagger.json api[.]target[.]com/login/api/swagger/v1/swagger.json api[.]target[.]com/users/api/swagger/v1/swagger.json
Or Even :
admin[.]target[.]com/api/swagger/v1/swagger.json
swagger.json lists all API calls and their required parameters. Even if some endpoints say they require auth, some may not enforce it, leading to a massive impact. It can also help uncover IDOR cases.
Never ignore swagger.json. Good luck.
#CyberSecurity #InfoSec #RedTeam #BlueTeam #BugBounty #bugbountytips #bugbountytip #HackerCommunity #Bugcrowd


1
96
$15,000 Write-Up: Unauthenticated Temporal on a Yahoo News Cluster
medium.com/@hi.david60/15-00…
termireum retweeted
I found a critical privilege escalation that took a brand new free trial account all the way to platform superadmin, with read access to every customer's data on the platform. It earned a $5,000 bounty.
The chain came down to 3 things:
- Mass assignment: a PUT endpoint let a user write their own `admin_permissions` field, including the superadmin flag.
- MFA bypass: escalating to admin triggered MFA on login, but a separate "auto login" flow handed out session tokens with no MFA at all.
- Broken tenant isolation: a superadmin token could read any user's data in any org on the platform.
Here's how I chained all three together:
1. Escalate my own account
As a new free trial user, I sent:
`PUT /api/admin/{my-user-id}`
`{"admin_permissions":"0000000f"}`
The server accepted it. No check that I was already an admin. My account was now superadmin.
2. The MFA wall
The moment I escalated, the backend started enforcing MFA on my logins:
`POST /token` → MFA challenge
Self-enrollment to MFA was disabled, so I couldn't even complete it. Dead end.
Then I remembered the auto login flow.
3. Why that flow exists
The dashboard has a feature for signing in unattended devices. Things that need a session but have no human to type a password (or MFA code).
You generate an "auto login" key, a base64 blob of `{userId}:{tenantId}:{random}`, and the device authenticates itself, headless. MFA is skipped there by design, because there's nobody at the device to challenge.
So I asked: what's stopping me from logging in as a "device" instead of a user?
4. Bypass MFA with the auto login flow
Before escalating, I'd already generated an auto login key for my own account. I replayed it against the device login endpoint:
`POST /autologin/devices`
`{"access_key":"{my-key}", ...}`
It returned a full session token. No MFA challenge, because this path was never meant to need one. And since my account was now superadmin, that token was a superadmin session.
The order is the whole trick. First I created the device key, then I performed the escalation, then I logged back in through the device flow, bypassing MFA. The key was minted before the MFA wall went up, so it still worked after.
5. What this unlocked
With that token:
`GET /api/users/{any-user-id}`
returned full PII for users in completely different orgs, not just mine. User IDs were sequential, so this exposed records across the entire platform.
#BugBounty tip:
When an app adds a second auth factor, check whether every token issuing path enforces it. One legacy or "convenience" flow, like auto login, device pairing, or an API key, that skips MFA can undo the whole thing.
And always ask: can I grab a credential before a security boundary goes up, then reuse it after?
JWT Attacks — The $5000 Bug That Forges Identity
medium.com/@cyber-ninjaaa/jw…

termireum retweeted

Solid resource 😱 This is one of the most structured open-source prompt packs I’ve seen for bug bounty hunting!
@mdp_sec broke down their entire workflow into 10+ reusable phases:
→ Recon & surface mapping
→ Authenticated access setup
→ Endpoint & vuln-class sweeping
→ Browser-based walkthrough
→ Critical-impact hunting
→ Triage, dedup & validation
→ Independent verification gates
It’s Web2 focused, but the methodology is gold for anyone building AI-assisted security workflows. The evidence-first, phase-by-phase structure is exactly how you avoid hallucinated findings and actually produce reliable results: github.com/mdpsec/bug-bounty…
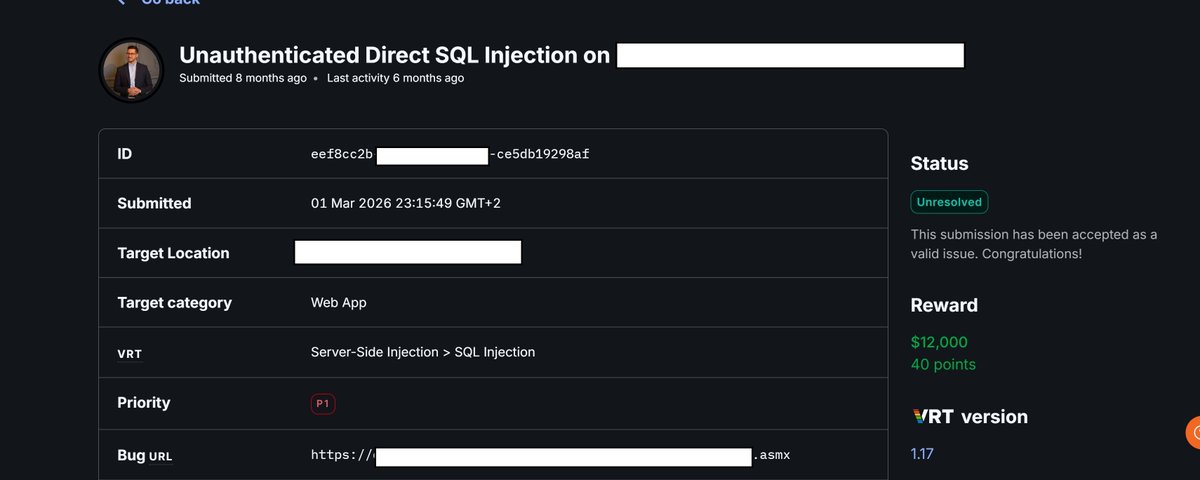
Multi-Factor Authentication Bypass Worth $10K
mfrhnkhn.medium.com/multi-fa…




termireum retweeted

Closed source is dead.
REA lets Claude Code or Codex take apart any app, all the way down to the binary, and explain exactly how a feature works.
- Native apps, Electron apps, websites, APKs, firmware, even smart contract bytecode
- Shows the evidence for every claim
- Then builds its own version of the feature
25,000+ GitHub stars in a single day. 100% open-source.
github.com/morluto/rea

From Leaked API Key to Full Account Takeover: Uncovering a Mass PII Vulnerability
medium.com/@Brian_Bange/from…
