

AWS Made Simple - Overcoming Cloud Complexity Trusted by 13k+ engineers! 📨
Bi-weekly tips →
Joined May 2009
- Tweets8.4K
- Following215
- Followers22.2K
- Likes6.1K


Pinned Tweet
The 𝗔𝗪𝗦 𝗦𝗲𝗿𝘃𝗶𝗰𝗲 𝗔𝗻𝗶𝗺𝗮𝘁𝗶𝗼𝗻𝘀 Page is live! ✨ 🎉
Currently, it includes 14 services/features, and we'll add more to our library every week!
Current catalog includes:
• The Dark Reader Deployment Pattern
• Polling vs. WebSockets via Amazon API Gateway
A leaked access key used to mean someone spun up GPU instances on your buckets. Now the expensive thing is quieter: tokenmaxxing through Bedrock 😬
The case that stuck with me: $97,000 in 48 hours, around 2 million Bedrock tokens per minute, one long-lived key.
Debugging inside a private VPC usually ends with a bastion host and a security group rule you promise to remove later. There is a mode most people never toggle: CloudShell VPC mode.
Your session runs in the subnet. It picks up the security groups and network ACLs around it, so the things that have no route from the internet just answer.
• Private EC2 instances
• RDS databases with no public endpoint
• Internal load balancers
S3 traffic from a private subnet still leaves through the internet by default.
And AWS bills you for the privilege 💸
That is the bit that gets me. A Gateway Endpoint fixes it, costs nothing, and is not enabled by default. For years now.
Why not?
If you enjoyed this post & you want to get 𝗯𝗶𝘁𝗲-𝘀𝗶𝘇𝗲𝗱 𝗔𝗪𝗦 𝗰𝗼𝗻𝘁𝗲𝗻𝘁 straight to your inbox, feel free to check out our bi-weekly newsletter 📨
You can also browse our 𝗽𝗿𝗲𝘃𝗶𝗼𝘂𝘀 𝗶𝘀𝘀𝘂𝗲𝘀 to see what you'll subscribe to 📚
awsfundamentals.com/newslett…

Yet neither S3 nor DynamoDB gets one out of the box. Not in a fresh account. Not in the console wizard.
I understand NAT Gateways are revenue. I do not understand shipping the expensive path as the default and calling the cheap one a best practice.
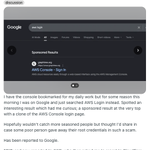
Someone googled "AWS Login" and the top sponsored result was a fake.
A clone of the AWS console login page
Didn't have this on my radar either, so just a thing to look out for 😬

• Use the Access Portal for sign-in
• Treat sponsored results as untrusted by default
Whole thread is worth a read:
reddit.com/r/aws/comments/1w…

P.S.: More AWS security gotchas like this in our newsletter: awsfundamentals.com
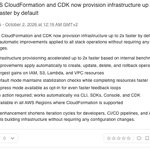
The slowness you blame on CDK has always been CloudFormation.
And CloudFormation just got up to 2x faster
It's automatic as of October 1. Your cdk deploy doesn't change, there's no flag to pass.

There's also Express mode if you want more. That one is opt-in: cdk deploy --express skips the extended stabilization checks and claims up to 4x.
Link
aws-news.com/article/2026-10…

P.S.: Our newsletter covers AWS releases like this one, visually, once a week: awsfundamentals.com