




NVIDIA GPU Attestation matters for confidential AI 🔐
GPU trust cannot stop at the VM boundary.
For platforms like Cocos AI, attestation helps extend trust to accelerated infrastructure.
👉 docs.nvidia.com/attestation/…
👉 cocos.ai/
#ConfidentialComputing #NVIDIA #GPU

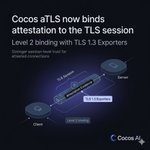
Cocos aTLS now binds attestation to the TLS session 🔐
That means:
• stronger relay-attack protection
• more robust attested connections
👉 ultraviolet.rs/blog/atls-bin…
#ConfidentialComputing #TEE #TLS

Why does vTPM matter inside a Confidential VM? 🔐
In Cocos AI, vTPM is part of the trust chain inside the CVM, enabled through Coconut-SVSM.
That helps extend trust into the guest environment.
👉 cocos.ai/docs/trusted-execut…
#ConfidentialComputing #TEE
🤖 Made with AI

Confidential workloads on Google Cloud — with more than just infra 🔐
Cocos AI adds:
• an agent inside the CVM
• Docker, Wasm, Python, and ELF runtimes
• provisioning, hardening, and integrity monitoring
👉 cocos.ai/
#ConfidentialComputing #GoogleCloud #TEE
🤖 Made with AI

KBS controls decryption 🔐
In Cocos AI:
• KBS stores decryption keys
• attestation gates key release
• separate KBS paths for algos and data
That makes OCI delivery policy-driven, not just encrypted.
👉 cocos.ai/docs/remote-resourc…
#ConfidentialComputing #OCI #TEE
🤖 Made with AI

Less exposure inside the CVM 🔐
In Cocos AI:
• SSH is disabled
• Docker uses Ramdisk
That means less persistent state inside the guest.
👉 cocos.ai/docs/architecture-c…
#ConfidentialComputing #TEE
🤖 Made with AI

Wasm inside Confidential VMs 🔐
Cocos AI supports AMD and Intel TEEs.
With Wasm in the CVM:
• lightweight runtime
• more flexibility
• more portable execution
👉 cocos.ai/
#ConfidentialComputing #WebAssembly
🤖 Made with AI

What makes a Confidential VM trustworthy beyond the TEE? 🔐
In Cocos AI, trust also includes:
• vTPM inside the CVM
• measured boot
• Linux IMA
That means guest state can be measured and verified end to end.
👉 cocos.ai/docs/trusted-execut…
#ConfidentialComputing #TEE
🤖 Made with AI

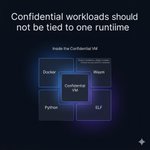
Confidential workloads need runtime flexibility
In the Confidential VM, Cocos AI runs:
• Docker containers
• Wasm modules
• Python scripts
• ELF binaries
Runtime flexibility makes confidential compute practical.
👉 cocos.ai/
#ConfidentialComputing #TEE
🤖 Made with AI

Confidential workloads across private cloud, Google Cloud, and Azure 🔐
Cocos AI supports:
• private and public cloud
• more flexibility
• an easier path to confidential workloads
👉 cocos.ai/
#ConfidentialComputing #TEE #CloudComputing
🤖 Made with AI

Encrypted algorithms and datasets as OCI images 🔐
In Cocos AI, resources use:
• OCI registries
• attestation-gated keys
• decryption only in the TEE
That makes OCI artifacts usable for confidential workloads.
👉 cocos.ai/docs/remote-resourc…
#ConfidentialComputing #OCI #TEE
🤖 Made with AI

Why build EOS with Buildroot? 🔐
In Cocos AI, a smaller guest OS means:
• less attack surface
• lower footprint
• faster CVM boot
For confidential VMs, minimalism is part of security.
👉 cocos.ai/
#ConfidentialComputing #TEE

Attestation gives evidence.
Compare it to what? 🤔
CoRIM defines reference:
• known-good values
• expected state
• trust across TDX/SEV-SNP
Cocos AI makes it policy-driven.
👉 cocos.ai
👉 CoRIM draft: datatracker.ietf.org/doc/dra…
#ConfidentialComputing #TEE
🤖 Made with AI

Trust shouldn't depend on vendor TEE attestation 🔐
Entity Attestation Token (EAT) standardizes attestation evidence.
With Cocos AI:
→ across TDX & SEV-SNP
→ verifiable runtime claims
→ portable trust layer
👉 ultraviolet.rs
#ConfidentialComputing #TEE
🤖 Made with AI

How do you collaborate on sensitive data 🤔
Without exposure?
🔐 Multi-party AI enables:
• Data is encrypted & processed in enclaves
• Attested execution
• Only insights are shared
AI collaboration without exposure
👉 prism.ultraviolet.rs/
#ConfidentialComputing #AI
🤖 Made with AI

Who verifies the machine? 🤔
🔐 Remote Attestation:
• Proof of execution in secure enclaves
• Integrity check before processing
• No trust in infra
No attestation = no proof
👉 ultraviolet.rs/
#ConfidentialComputing #CyberSecurity
Why is data vulnerable during processing? 🤔
Encryption usually stops there.
🔐 Confidential Computing:
• Encrypted in use
• Secure enclaves (TDX, SEV-SNP)
• Verifiable execution
Trust → cryptographic proof
👉 ultraviolet.rs/
#ConfidentialComputing #CyberSecurity
How do you run secure computations across clouds—without exposing data? 🔒
Prism AI:
✅ Attested TLS (remote attestation)
✅ Intel TDX & AMD SEV-SNP
✅ SHA3-256 verification
🎥 youtube.com/watch?v=1yGJ787_…
#ConfidentialComputing #PrismAI #CyberSecurity

Cocos AI first to implement next-gen aTLS 🔐
Level 2 binding:
• Session-bound attestation
• TLS 1.3 exporters
• Stronger vs relay
From identity-based → session-bound crypto trust
📖 ultraviolet.rs/blog/atls-bin…
#ConfidentialComputing #TEE #CyberSecurity

Collaborate on sensitive data — without exposing it 🔐
Prism AI enables secure, multi-party AI
across organizations — without data sharing.
Combine datasets, preserve privacy,
and keep full control over your data.
📺 youtube.com/watch?v=1yGJ787_…
#ConfidentialComputing #PrismAI