


vamitrou retweeted

A tool which bypasses AMSI (AntiMalware Scan Interface) and PowerShell CLM (Constrained Language Mode) and gives you a FullLanguage PowerShell reverse shell. github.com/Sh3lldon/FullBypa…
vamitrou retweeted

More details on the Soyboy “EDR killer” tool offered on RAMP, it uses the Zemana Anti-Malware tool, plus it requires admin privs and a UAC bypass (lol)
Basically the same how Cuba ransomware was using the Avast Anti-Rootkit tool
reddit.com/r/crowdstrike/com…


vamitrou retweeted

Here's a helpful article: thegrayarea.tech/403-forbidd…


vamitrou retweeted

“It’s just summer.” 🙄 teapawt.org/BestForBritain/status/…
vamitrou retweeted

Really well written post by @fransrosen on breaking OAuth implementations through postMessage gadgets that leak URLs. Awesome research, I loved following the journey. Totally worth the time it took you to do this. @avlidienbrunn is a great sounding board. labs.detectify.com/2022/07/0…

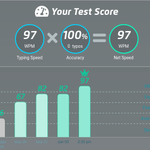
Wanted to try my keyboard switches.
97 words per minute with 100% accuracy!
Last attempt rated as PRO! :D
typingtest.com

Officially certified as Exploit Researcher and Advanced Penetration Tester
#SANS #GIAC #GXPN #SECURITY
credly.com/badges/12ba47b2-8…

vamitrou retweeted

I published a blog article detailing a phishing technique I called Browser in the Browser (BITB) Attack. It's very simple but can be very effective. I also published templates on my Github feel free to test them out.
mrd0x.com/browser-in-the-bro…
