

The largest collection of malware source code, samples, and papers on the internet. Password: infected
International
Joined August 2019
- Tweets25.2K
- Following386
- Followers455K
- Likes21.2K



I can't keep up with all of the banger cybersecurity memes
Every time I have whimsical thought I see someone else posted it first
GOD DAMN YOU, LET ME MAKE A FUNNY POST
Today silly shenanigans:
- PHP2shell, leak, bad stuff
- Something about Railway?
- The number 4 is a valid cert
- NodeJS and something about broccoli?
- LiteLLM supply chain attack
- GitLab CVSS 10
- OpenCode leaking API keys
What does this all mean? Idk

People are getting free goop and they're "warning" people?
This generation makes me SICK.
I speak for everyone when I say we need the goop NOW!!!!!

Chat, we've gone big league
Last time on Dragon Ball Z, a few weeks ago I made a crappy little video of me bonking goop (malware) with a stick. In the video I mentioned I use IDA Pro, I believed it to be the best on the market, and said as an independent researcher I can easily afford (I used a cracked version).
Following this silly video, I got an e-mail from the people who make IDA (Hex-Rays). I immediately believed they were going to yell at me, hit me over the head with a cinder block, or sue me, for using a cracked version of their very expensive product and displaying it in the video.
Instead they told me they liked my goop video and they liked my goop posts. They also said they like vx-underground because they value the goop.
So anyway, so instead of beating me over the head with a cinder block, they gave me IDA Pro Expert for free.
wtf i love hex-rays


> be me
> get on xibbler
> group of nerds do php exploit poc thingie
> make sassy repost
> nerd fight ensues
> forgot dont like nerd fights
> delete post
> get off xibbler
> eat sandwich
> get back on xibbler
> "i wonder if its calmed down"
infosec xibbler:
> wake up
> take a shit
> get out of bed
> check beep boop
> everyone saying ooga booga PHP
> wtf why
> look inside
> ultra mega fuck off exploit coming
> php2shell
> so bad PHP devs begs nerds to patch tomorrow
> proof of concept video released
> pwn website easily
> video has dancing anime lady?
> nobody explains why dancing anime lady
> no one even asks why proof of concept has dancing anime lady
> ok
> cybersecurity nerds bamboozled
> some saying will be up there with Log4J in severity
> goopocalypse
pic unrelated

I stepped away from my beep boop to go potty
Came back to see my Windows VM restarted because Windows decided to force update
Yeah, my OS was really out of date, I had to restore a snapshot, so you FORCE install an update?
Microsoft, what the actual fuck is your problem?

Dawg, I got an e-mail from a student at FSU (Florida State University) jokingly asking if they're attending the University of Goop.
They received an e-mail from a student (who has surely had their e-mail compromised) telling them they need to review the Universities conduct policy, or something, and they must install "Zoho Assist"
Zoho Assist is a legitimate tool for remotely assisting people. But, some dorky ass Threat Actor is sending out these goofy social engineering e-mails hoping a student will install Zoho on their devices
My question for the Threat Actor: what if the student isn't running Windows? Many students use Apple products, or are running the infamous LINUX OPERATING SYSTEM, so what is your plan then?
Secondly, what's the plan then? Remotely access some broke ass college kids device and steal their $13 from their bank account?
I don't get it
There has been a glitch in the matrix. @smica83 shared a heavily obfuscated .vbs which was first identified in Morocco, initially named "nouveau_cv_pdf.vbs".
I wasn't going to statically deobfuscate the piece of shit, so I emulated it. During emulation it catches it pulling a stage 2 binary from: https://qmlab1(.)com/assets/img/katyusha2
I curl the payload, look inside, and you're never going to believe it.
It's the exact same fucking binary I just discussed. It is the Go malware labeled internally as "EasyAgent"
I've never accidentally stumbled upon the same malware campaign, with different delivery methods, back to back like this. This is very silly


> be me
> get dm
> "smelly, i found goop"
> wtf i love goop (malware)
> "Someone in South Korea received a Fortinet installer, except the "ipfilter" binary looks suspicious"
> ok
> download
> look inside
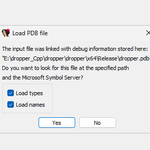
> goop malware left pdb intact
> "E:\dropper_cpp\dropper\dropper"
> ...
> image 1
> lolwtf bro
> downloads "install.exe"
> http://52.74.54.75/storage/install.exe
> install.exe is malware written Go
> registers itself as a service
> "EasyAgent"
> unobfuscated
> everything visible
> "Easyagent_connection_Connect"
> shows connecting to wss://52.74.54.75
> Image 2
dawg, if you're going to try to masquerade as a fortinet client thingie, and target large companies for initial access, you really need to up your goop game. this took me literally like, 2 minutes to reverse engineer and identify what you're doing.
Dawg, we've got MORE goop (malware) targeting the trucking industry
Holy cannoli, bro. This unidentified Threat Group is super persistent and is really swinging for the moon to compromise trucking and/or material transportation companies
If you've been following my goop posts, you've seen now this is a reoccurring goop we've encountered and these nerds NEED to know where goods at being delivered.
> make post about Coruna Exploit Kit
> initially identified by @malwrhunterteam
> share my thoughts, confirmations
> share the goop
> get off beep boop
> come back
> stinky nerds arrive on the scene
> stinky nerds doing detective research
> @AelsMartin identifies 183 other websites carrying it
> @duniel_pls identifies infection vector being vulnerable PrestaShop instances
> @ffforward retrohunt sees campaign since at least July, 2026
WHOOWEE BOIS WE GOT OURSELVES A STATE SPONSORED CAMPAIGN
*I'm being intentionally hyperbolic for comedic effect, Google Threat Intelligence linked Coruna Exploit Kit to a Chinese financially motivated Threat Group in late 2025. However, Coruna has historically been state-sponsored, and to the best of my knowledge no information available has determined how state-sponsored malware deriving from the United States fell into the hands of Chinese Threat Actors. There is lots of speculation, big that's a lot of anime lore for this post

> be @malwrhunterteam
> on a legendary run on social media
> find silly website
> estrosa-dot-it
> website for italian cosmetics
> legit website, used by the pasta people
> notice something silly on website
> /js/analytics/assets/js/group.html
> look inside
> group.html checks browser agent
> detects iOS version
> loads different files depending on iOS version
> loads 49554fde7424c31c.js
> 49*.js doing lots of crazy stuff
> layers of obfuscation and pointer arithmetic
> lolwtf
> look inside
> exact match of Coruna EK
> Coruna Exploit Kit
> Coruna originally used by US government
> rumored to be made by US contractor
> rumored US contractor illegally sold to kremlin
> UNC6353 (kremlin) found using Coruna in 2025
Chat, someone is swinging the legendary goop around. It is Coruna, the state-sponsored iOS exploit kit. All this requires is your Apple device to visit a website and (assuming you're running the targeted iOS version) you're cooked.
Although, from my initial bonking of it, it appears this delivers two different payloads depending on the iOS version. Unfortunately, I know almost nothing about iOS exploitation and iOS malware, so I have no idea what I'm doing. I encouraged my peers and colleagues to review it. It is good goop.
I've archived the payloads from the compromised domain. The shared link is below.
pic unrelated


Update
I'm on STAGE 13 of this payload.
Congratulations, random mystery goop, you're now the most chained payload I've ever encountered.
Yeah, so I'm looking at this goop (malware) right now and it's beginning to irritate me. It's not necessary super advanced goop, but it is rustling my jimmies a little bit.
> .iso file
> sends .iso to programmers or smth
> they mount .iso
> installer.lnk (windows shortcut file)
> installer.lnk runs setup.cmd
> setup.cmd runs ipyw32.exe -x submergibility.txt
> submergibility.txt is Python code
> submergibility.txt big ass fuck off Base64 encoded Python
> decode
> decodes to big ass fuck off .py file
> big ass fuck off Base64 encoded again
> Base64 encoding substituted
> .replace('о', 'b').replace('Ч', 'M').replace('Р', 'S').replace('л', 'm').replace('Л', 'W').replace('у', 'X').replace('Т', '2').replace('Е', 'H').replace('б', 'L')
> decode again
> another big ass fuck off .py file
> another base64 encoded buffer
> Base64 also XOR'd
> XOR key also Base64 encoded
> omfg we get it bro, you dont want to be bonked
> decode, undo the xor-ing
> position independent x86 shellcode
> neat
> open in ida
> bonk bonk
> connects to website
> downloads another file
Dawg, we're like, 8 stagers deep. I can tell from this goop, and the programming nerds you're trying to infect, you don't need 200 bajillion stagers to infect vibe coder Timothy Dingleberry. Timothy Dingleberry can barely read, you could have just done ai_helper.exe and be done with it
