




Wirelyss 👁️🗨️💫 retweeted

Claude Code 刚刚通过逆向工程,在 90 秒内破解了我酒店房间的门锁。2014 年的加密技术。右上角的烟雾探测器也使用同一套协议——那个红色小灯不是电池指示灯。我启动扫描时,它闪了两次。
我现在躺在一个每晚 85 美元的酒店房间里。我打开 Claude Code,输入:「扫描范围内的每一台蓝牙和无线设备。告诉我哪些设备在与哪些设备通信。」
它找到了 19 台无线设备。其中 18 台是正常的。
设备 19:一个 BLE 控制器,使用着自 2014 年以来就没有修复过的固件。它控制着电子门锁、烟雾探测器、恒温器和房间里的保险箱。四台设备共用一个控制器。同一种协议。10 年没有任何更新。
我让 Claude Code 分析这套协议。整个过程用了 90 秒。
门锁使用一个 4 字节的滚动密钥,没有会话令牌。Claude Code 在第三次尝试时生成了一个有效的主密钥。我躺在床上,听见房间的门锁咔哒一声打开了。
接着,它发现烟雾探测器也连接在同一条总线上。照片里的红色小灯?那是控制器状态指示灯。它并不监测烟雾。它每隔 8 秒就会确认一次与门锁系统之间的 BLE 握手。
这意味着,任何处于蓝牙覆盖范围内的人——走廊、隔壁房间、停车场——只需要一条提示词和 90 秒,就可以:
打开你的房门
关闭房间内的警报
打开你的保险箱
而烟雾探测器会通过那个小小的红色闪烁,确认连接状态
检查只需要 2 分钟:
步骤 1 → 打开 Claude Code → 粘贴第一条评论中的提示词
步骤 2 → 它会扫描覆盖范围内的每一台 BLE 设备,并标记存在未修复固件的设备
步骤 3 → 如果发现问题 → 要求更换房间 → 要求换到配有机械门闩的房间 → 然后使用那个房间
每一家使用 2018 年之前生产的 ASSA ABLOY 或 Onity 门锁的酒店连锁都存在这个问题。这大约占全球酒店的 30%。
我本周测试了 3 家酒店。3 家全部存在漏洞。
看看照片。右上角。那个每隔 8 秒闪烁一次的红点。那就是握手信号。
保存这条提示词。下次入住酒店时 → 先运行它,再打开行李。


Wirelyss 👁️🗨️💫 retweeted

THIS IS A WARNING TO EVERYONE.
The ONLY REASON large companies aren't saying they've been hacked is BECAUSE THEY ARE TOO INCOMPETENT to know. They are staffed with INDIANS with FAKE CREDENTIALS.
YOU ARE ALL FUCKED.

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.

Did you know there is a patron saint of the internet? His tomb is Livestreamed 24/7. Pray to Saint Carlo Acutis!


Wirelyss 👁️🗨️💫 retweeted

Thanks for the continued donations $UNICORN ! We are going to use it for making more genetically modified horse embryos on a quest to make real unicorns


Wirelyss 👁️🗨️💫 retweeted

what’s a good critical vulnerability for someone just getting into PHP core?
Wirelyss 👁️🗨️💫 retweeted

tonight is the night


So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Wirelyss 👁️🗨️💫 retweeted
Just so people know, This is JUST ONE hosting companies STATS:
230,000 websites are frozen/can't be updated by their owners so they can't be updated -- and many are SITTING VULNERABLE -- as well as 20,000 apps.
Their keys have all been stolen -- their customers are YOU in many cases, so I would say you're info is all in the hands of hackers.
THIS. IS. JUST. ONE. COMPANY. that is actually doing incident response now. MOST COMPANIES AREN'T EVEN LOOKING.

🚨 High-severity Node.js flaw could allow remote code execution; CVE-2026-111497
Node.js has patched an out-of-bounds write vulnerability in its bundled Brotli decoder.
⠀
An attacker able to supply malicious Brotli-compressed data to an application could potentially corrupt memory and execute code on the underlying server.
⠀
Affected:
• Node.js 22.x
• Node.js 24.x
• Node.js 26.x
Fixed:
• Node.js 22.23.4
• Node.js 24.22.1
• Node.js 26.12.1
⠀
End-of-life Node.js versions may also be vulnerable and will not receive upstream security updates.
Administrators should upgrade and restart affected services.
Source:
nodejs.org/en/blog/vulnerabi…


Wirelyss 👁️🗨️💫 retweeted

Admin keys for Swell DAO's swETH and rswETH appear to be compromised (railway related?)
* Attackers are raising NAV by max 1% (unbacked) each hour
* Four malicious upgrade contracts have been deployed (although not queued yet through multisig) that could steal approx 2500 ETH
Wirelyss 👁️🗨️💫 retweeted

the vamps on pumpfun are ______
stop directing fees to randoms and just stick to holder rewards.
also fudding coins on pumpfun works?
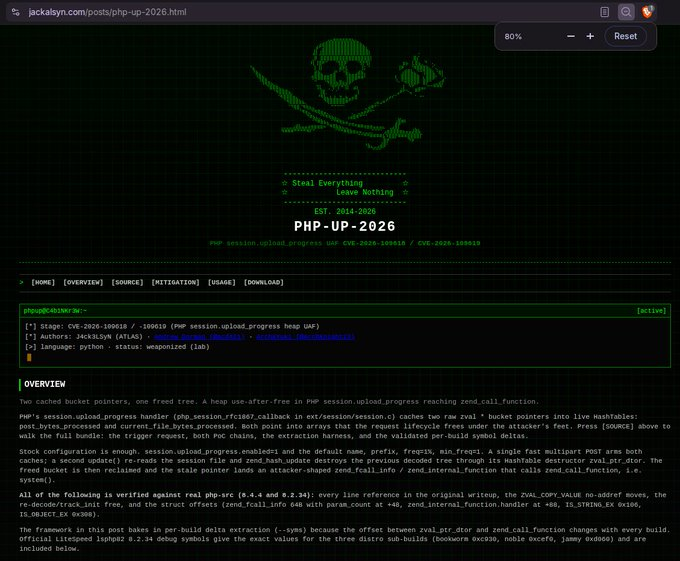
#php2shell

NEW CYBERLEEK?
There is a PHP vulnerability going GIGA viral
People are recommending you revoke accces to EVERYTHING you don't use.
And these 3 DROPPED THE EXPLOIT?
Redirecting and splitting 100% of pumpfun github creator rewards between the 3 authors.
xitter.cf/J4ck3LSyN/status/21127…
Meanwhile, thanks to Elon people's ability communicate is restored via Neuralink, people can get around safely in self driving electric cars, people in crisis areas of natural disaster have starlink connection


I've never seen a pfp used quite like this before. Just when you think you've seen it all.

Hi @united Today my husband and I boarded to go to Japan. See my picture? I’m crying because I was DOWNGRADED from the business class we paid for with our hard earned money for a special trip.
Wirelyss 👁️🗨️💫 retweeted

Like we are legitimately sending fees to guys that leaked potentially what the issue was (They didnt find it) & left millions of people vulnerable to it. Also went against the industry which was dropping a patch at a specific time so everyone could update at the same time & be protected. Then they said they had a fix for it. Which didnt work. These people are hated & larping using llms & call themselves cybersecurity experts. But are spam claiming a coin.... zero
YQ4NNeQxHAtdcB8ohx21eJ9U8eTzxNRvGNHkRaA4Pnw

Wirelyss 👁️🗨️💫 retweeted
For what its worth, i dont like shilling coins atm because its -EV because people dont want to hold & rotate. But i think this is a huge narrative & as such im just in the og + holder rewards coin. Dont think there is any need for anyone to get fees
FjLFsaPKSxJGh25iTKCLEkthbeHKLJrxvHyJG9wqpump