
State-of-the-art vulnerability research & exploit intelligence • @alisaesage @zerodaytraining
Worldwide
Joined January 2015
- Tweets429
- Following1
- Followers12K
- Likes808
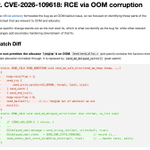





⚡️ 0-Day Alert: PHP remote code execution
CVE-2026-109618: OOM bailout to UAF
CVE-2026-109619: state corruption to UAF
We independently scrutinized the bugs, they are legitimate and should be fixed asap.
Update to: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35


Most importantly: the fixes are systemic, closing many distinct attack paths that could count as individual bugs with no CVE assigned beyond what is currently published, and different IOCs.
Deep dive in our intelligence community: intelligence.zerodayengineer…
xitter.cf/zerodayalpha/status/21…


Keynote: The Art of Looking Deeper zerodayengineering.com/resea…
Presented by @alisaesage at @_c0c0n_ 2026

Chromium VRP just raised reward amounts – after lowering it to near 0 earlier this year.
4x memory safety baseline, increased rewards for logic sandbox, and the fuzzer bonus is back (!)
Still no incentives to report the bugs that could pay 10x at comps...


Zero Day Engineering retweeted

My take on reversing the CoreGraphics bug: <1h net solo time, 95% autonomous, without ghidra or ida!

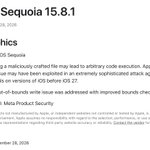
⚡️ 0-Day Alert: Apple CoreGraphics RCE exploited in targeted attacks
CVE-2026-86950: out-of-bounds write in CoreGraphics parsing a maliciously crafted image/PDF, leading to arbitrary code execution.
Both iOS and macOS are vulnerable.
This AV is reachable through a wide variety of iOS native and 3rd party apps that render graphics, such as WhatsApp (first suspect due to report credit), Safari, iMessage, etc.
Zero-click where auto-preview renders the file.
However, the bug alone is not enough to compromise the device, and requires further chaining such as sandbox escape and EoP. These further bugs are not public.
Patched in iOS/iPadOS 26.7.1, macOS Tahoe 26.7.1, macOS Sequoia 15.8.1.
intelligence.zerodayengineer…
We now have email alerts, too. Subscribe on: intelligence.zerodayengineer…

Zero Day Engineering retweeted
Recent 0-Day in Chrome is a canon JSE bug class like those I exploited 10 years ago. Most researchers think they no longer exist. This year’s regression
⚡️ 0-Day Alert: Chrome v8 RCE exploited in the wild
CVE-2026-85046: v8 array-builtin callback side-effect to elements-kind transition confusion.
Affects both Turbofan and Maglev.
Exploit will work in default config but requires multiple other bugs to achieve arbitrary code execution on the system. The bug alone without helpers could do for an UXSS.
Patched in Chrome 152.0.7977.82/.83


⚡️ 0-Day Alert: Chrome v8 RCE
CVE-2026-87491: WasmGetOwnProperty builtin may invoke a getter from user's JavaScript, leading to OOBW.
Patched in Chrome 153.0.8010.36/.37
intelligence.zerodayengineer…

Zero Day Engineering retweeted
If you think like me, you don't see "the bug that broke the system".
You see: limitless possibilities, multi-dimensional structures, abstract patterns, recurrent archetypes, and trend lines striking from past into future, like a crack in the block universe.
But can you still collapse the complexity into one concrete 0D instance that gets the bounty? Yes
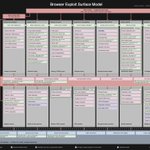
Browser Exploit Surface model + bug overlay
CVE callouts: randomly picked exploitable bug samples from historical records
@alisaesage
xitter.cf/alisaesage/status/2091…

⚡️ 0-Day Alert: Chrome v8 RCE exploited in the wild
CVE-2026-85046: v8 array-builtin callback side-effect to elements-kind transition confusion.
Affects both Turbofan and Maglev.
Exploit will work in default config but requires multiple other bugs to achieve arbitrary code execution on the system. The bug alone without helpers could do for an UXSS.
Patched in Chrome 152.0.7977.82/.83
We made a dedicated masterclass that goes into understanding JSE bugs from the first principles – JavaScript Engine Internals: zerodayengineering.com/train… (@alisaesage)
This specific bug class stems from the ECMAScript specification, has many concrete shapes and had countless instances over the years
Browser Exploit Surface model + bug overlay
CVE callouts: randomly picked exploitable bug samples from historical records
@alisaesage
xitter.cf/alisaesage/status/2091…


Exploit surface modeling is the spine that our VR learning content is built around. Currently available within Hypervisor and Browser specializations - early model versions, complete way of thinking and practical navigation. zerodayengineering.com/train…
Mastery container: Multi-Specialization Essentials
A curated course of foundational webinars and hands-on masterclasses taught by @alisaesage, covering the introductory essentials of the three classic specializations at Zero Day Engineering: vulnerability discovery, hypervisor and browser exploitation.
Made for self-paced study with minimal prerequisites that can be taken over a weekend as orientation in the field or initialization of multi-specialized work with AI.
Details: zerodayengineering.com/train…
Purchase within 21 September 2026 to get 10% off any full training of your choice.
Both of VMware vCenter remote bugs that we warned about from the recent Broadcom advisory, are now reported under active exploitation in the wild:
⚡️ VMware just released a critical security update for ESXi hypervisor suite (VMSA-2026-0006).
Two attack vectors:
1. Remote attack on vCenter –
CVE-2026-59309: auth bypass via network access
CVE-2026-59310: directory traversal RCE
An exploit would allow control of entire ESXi infrastructure.
2. A VM-escapable set of two bugs –
CVE-2026-59310: vmxnet3 OOBW
CVE-2026-41703: core OOBR
These are likely chainable to break out of VM and achieve code execution on hypervisor OS, as a privileged guest OS user.
Diffing and exploiting (1) is straightforward and should be patched promptly.
Zero Day Engineering retweeted
Bottom line: abstract modeling in VR has predictive power that was just validated with a 250K bug in an ultra hardened system.
Answers the question: where do you point AI when everybody is using the same models to find bugs in the same code? Obviously must “think different”, but where does the difference come from?
It comes from depth, abstraction, experienced intuition, structured frameworks, weird angles, personal taste, and the courage to push the frontier.
That’s what I put in the foundation of all @zerodayalpha frameworks years ago. It’s still there unchanged.
⚡️ 0-Day Alert: IBM LangFlow OSS RCE
LangFlow agent orchestration deployments have been under active exploitation since May.
CVE-2025-34291: CORS misconfiguration + SameSite=None
CVE-2026-33017*: Unauthenticated RCE via build_public_tmp's data parameter
CVE-2026-55255: IDOR in /api/v1/responses: run any user's flow by ID
CVE-2026-0770: Unauthenticated RCE via validate_code() / decorator abuse
CVE-2026-9198: Unauthenticated RCE via auto_login + validate/code chain
Bugs are not hard, likely spotted by generally available AI. Public exploit POCs exist.
Majority takes input from an API endpoint variable and executes it directly on the OS.
Attack pattern suggests that LangFlow has not seen basic security QA from the developer, and shouldn't be deployed in environments where arbitrary code execution poses a risk.
* Attached: 33017 patch diff and code trace to exec()


We are enrolling Q4 cohort of Alpha Exploit Intelligence. Make sense of the vulnerability landscape with an advanced exploit engineer, getting honest briefing on what matters and why: zerodayengineering.com/intel…
Zero Day Vulnerability Research course teaches deep models of how bug and exploit works which makes no difference between a webapp and a hardened kernel: zerodayengineering.com/train…