

rebuilding https://xitter.cf/t.co/oFH3BQm9YZ and creating zseano methodology v2. *COMING SOON!!* ex full time amazon hacker 2018-2026 🫡
Joined February 2012
- Tweets7.7K
- Following722
- Followers83.4K
- Likes10.7K





zseano retweeted

Kudos to @GeminiApp, @php_net Core, @OpenAI, @calif_io, & partners for coordinated disclosure.
👇 Full breakdown & PoC: wiz.io/blog/php2shell-php-rc…

pay attention bug bounty program owners.
if your top hackers are walking away and not submitting anything anymore, then you have failed somewhere.
(although let's be honest.. these days *most* programs don't actually care if people stop submitting. they're like "okay w/e")


92% of 77 CTBBP researchers surveyed have stopped or reduced submissions due to poor program experiences.
Fair treatment ranked above bounty size when choosing a new program.
Our new research with @ctbbpodcast:
The Researcher Attention Problem
bugbountymaturity.com/resear…

zseano retweeted

You can now perform content discovery at 100k requests per second with h3fuzz on http/3 hosts (fork of ffuf with http/3 support).
Tool here: github.com/assetnote/h3fuzz
Research post here: slcyber.io/research/how-prac…
non hacking post, but did anyone here ever do Halo2 Superbouncing? then Halo3 came out and the bouncing era ended as it didn't work anymore.
Well thanks to AI, 22 years later.. superbouncing on Halo 3, ODST and Halo: Reach has been unlocked
youtube.com/watch?v=zPGxUCEd…
Mindblown.
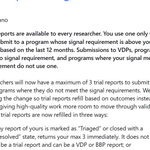
1 month to triage which then burns one of your trial reports. imagine you report 3 valid bugs, but no one touches 'em for 1month++. and then you find more bugs.... but you can't submit them. what then?
there is a better solution than all platforms adding submission limits imo


zseano retweeted

I got $90,000 for a RCE in Google.
simonkoeck.com/writeups/goog…

zseano retweeted

Bug bounty queues are drowning in AI-generated reports. Platforms, programs, triagers and researchers all pay for it.
So we're open-sourcing the triage skill we use internally @BugBunny_ai to filter out false positives and non-actionable reports. It does two things:
1. Validates the report with an end-to-end test
2. Escalates valid bugs to their highest defensible impact, e.g. a DOM XSS pushed to full account takeover
Every report gets a verdict:
🟢 Green: validated end to end, ready to submit
🟡 Yellow: more work needed first
🔴 Red: do not submit
github.com/Sequester-AG/bug-…

Did a bit of hacking past few days and I still prefer manual hacking over relying on AI. Even for writing reports. Manual hacking is just so fun (time consuming tho..) and gets my brain working. And when I find a bug I feel like *i* have achieved it. Not AI.. “found a bug!”🙄


zseano retweeted

Blog post about From header smuggling in Apple iCloud just dropped.
Sending emails as [email protected], exotic parsing, and a $15,000 bounty.
sec-consult.com/blog/detail/…


