

Threat-Hunter/Film-Nerd 🎬 https://xitter.cf/t.co/8wOiKi2F25 💾 https://xitter.cf/t.co/JHM8u3D9na
Joined July 2016
- Tweets1.5K
- Following1.6K
- Followers337
- Likes3.6K




piggy-backing on research from @ossmalware and seeing interesting EtherHiding procedures in the PolinRider samples - this newer cluster runs a simple algo against the Ethereum transaction "to" addresses to resolve the dead drops
163.34.229[.]243
211.17.211[.]8

Seeing around 130k vulnerable Plex servers still out there on Shodan (probably quite a few honeypots); if fellow corpo rat then run these IPs against your IdP/VPN logs and find employees with exposure
#plex2shell #plex


You needed an AI model to understand what this is? For the love of god please invest in real security folk


We discovered a sophisticated recording device that was hidden inside one of our offices. We used our models to understand the device and where it had come from, identifying that a specific employee had planted it a few days earlier. We referred the matter to the FBI, and we’re grateful to the agents and prosecutors who moved quickly to make an arrest. The FBI’s investigation is ongoing and we will continue to support their work.
At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data. The employee was terminated.
We take protecting our technology, data, and people seriously, and as a matter of national importance. Our security program is designed to protect against a wide range of threat actors, from insider risks to cybercriminals to nation states, and this case is an example of how AI can help address these sophisticated security threats.
I have several oceanfront properties in Idaho to sell any individuals who register this as a real risk

Anthropic's Frontier Red Team believes small AI models may now be months away from being capable of self replicating without access to a datacenter.
Quoting from the blog:
'The capabilities that make AI models generally powerful coding agents also generalize to cyber tasks, including autonomous replication. Like coding agents in 2024, we’re seeing signs of life for AI worms. We don’t yet have a full rogue replicator, but agents are becoming increasingly capable of completing the individual steps in the replication chain (and passing on their adaptations to future copies of themselves).
At the same time, increasing amounts of inference compute are now available both inside and outside of datacenters (see Appendix D). It’s uncertain exactly what form autonomous AI replication will take. It could be a slow, distributed “digital slime mold,” living on relatively insecure compute. It could also be a powerful cyber model that breaches datacenters at a high pace, or a model that scams people for compute credits.
As a prediction that goes beyond our experiments, we expect a future awash with agents running on all types of hardware, including some that aren’t under human control. While it’s true that IoT devices have been vulnerable for a long time, lightweight agents may be much more willing than human attackers to put in the effort to compromise large fractions of the world’s IoT compute. The rise of slow replicators would also be a bellwether for more aggressive, faster ones that can breach more hardened machines or be effective API key thieves. We should aim to harden our systems to make it difficult for such replicators to spread, but also prepare to deal with a world where they are here to stay.'

Droogy retweeted

Six years ago, SolarWinds became the victim of a supply chain attack that impacted thousands of customers and government entities.
In this new 3-part blog post series, I'll walk you through my three unauthenticated RCEs that existed across the SolarWinds product line (before 2020) and required only network accessibility.
Link to each blog post in the comments and a big shoutout to my team at @ArmadinSecurity for helping to make this series possible!
All bugs have been remediated, and I waited an extra two weeks after the patch to provide all customers time to update to the latest version.
Droogy retweeted

New domain:
ancientrooftops[.]de
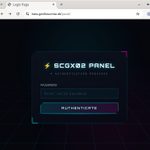
Same C2 panel hosted on https://lunar64[.]ancientrooftops[.]de/panel/


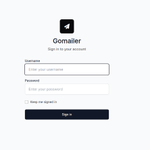
Haven't seen much reporting on this - recently discovered a ton of exposed panels for "Gomailer". Seems to be 100% vibe-coded delivery infrastructure for PhaaS toolkits.
Find more exposed panels on URLScan:
page.title:"Mailer\-Go Mission Control"
link[.]bubblybank[.]com

You can also look for one-time URLs generated from this platform with the following regex (pattern likely to change)
([a-f0-9]{4,10}\.).+\/(v3\.[a-f0-9\.]+)$
If you aren't regularly hunting your Okta logs or do not regularly update your configs, then this is guaranteed to find some questionable stuff in your network and lead to some tough questions around commercial VPN usage...
github.com/THORCollective/HE…

Droogy retweeted

Disable this immediately in your Direct message settings, as it's on by default.
Anyone can voice call you and see your IP address when they do

audio and video calling are now available to everyone on X! who are you calling first?
Readers added context they thought people might want to know
Contexte important pour la sécurité : par défaut, les appels sont activés et chaque appel révèle les adresses IP des deux utilisateurs. Les utilisateurs qui souhaitent garder leurs adresses IP privées doivent modifier leurs paramètres de confidentialité. (Traduction Française)
t.co/w0no8idGoK
> nothing special

Seems like there is malware abusing GitHub attachments to create file links in legitimate repositories. Here's a funny example github.com/microsoft/MSRC-Se… nothing special, but just seemed neat.
Droogy retweeted

We just put down a deposit for the venue, have 10+ artists committed, and iconic NYC dj’s scheduled.
If you’re interested in helping make the FIRST EVER NET GALA a reality by sponsoring the intersection of hacking, art, and malware, please dm me!
It’s going to be iconic.


very cool and normal that other countries' police are using the playbook ours developed to cover up crimes
This Post is from an account that no longer exists. Learn more
Droogy retweeted

Imagine giving an engineering team 3 years to learn a new way of working (say waterfall-to-agile for example), and then declaring that the new thing failed and will never work, despite hundreds of other teams having success with the new thing.
This is that, but so much easier.
because video games fucking rule thats why
