
A security analyst/enthusiast. Blue team.
Ann Arbor, MI
Joined June 2017
- Tweets18
- Following34
- Followers5
- Likes22


CaffeinatedSecurity retweeted

KRACK Vulnerability: Details and Moving Forward nwg.io/2xPR4Hp by @networksgroup

CaffeinatedSecurity retweeted
Excited to release our case study with @zingermans! Alignment of common values makes our partnership successful. nwg.io/2xVP7WH

CaffeinatedSecurity retweeted
Apparently some fax company got hacked. teapawt.org/equifax/status/9059187…

CaffeinatedSecurity retweeted
[New Blog] Equifax breach: A learning opportunity to get ahead of the constant threats nwg.io/2jaNnoE by @infosystir #EquifaxBreach
Excellent talk given by @NielsProvos at #duosecurity this past Friday! Always eye opening to hear how the best in the biz handle sec threats
The fact that next-gen endpoint solutions may not be ready to show internal to internal endpoint traffic is....strange.
CaffeinatedSecurity retweeted
We're hiring! Interested in cyber threat detection and helping to keep our customers safe 24x7 from cyber attacks ? hubs.ly/H082Wbc0
CaffeinatedSecurity retweeted
Chrome extension intercepting every form submission. Check the permissions of your browser extensions now! blog.asdfx.us/ #privacy
CaffeinatedSecurity retweeted

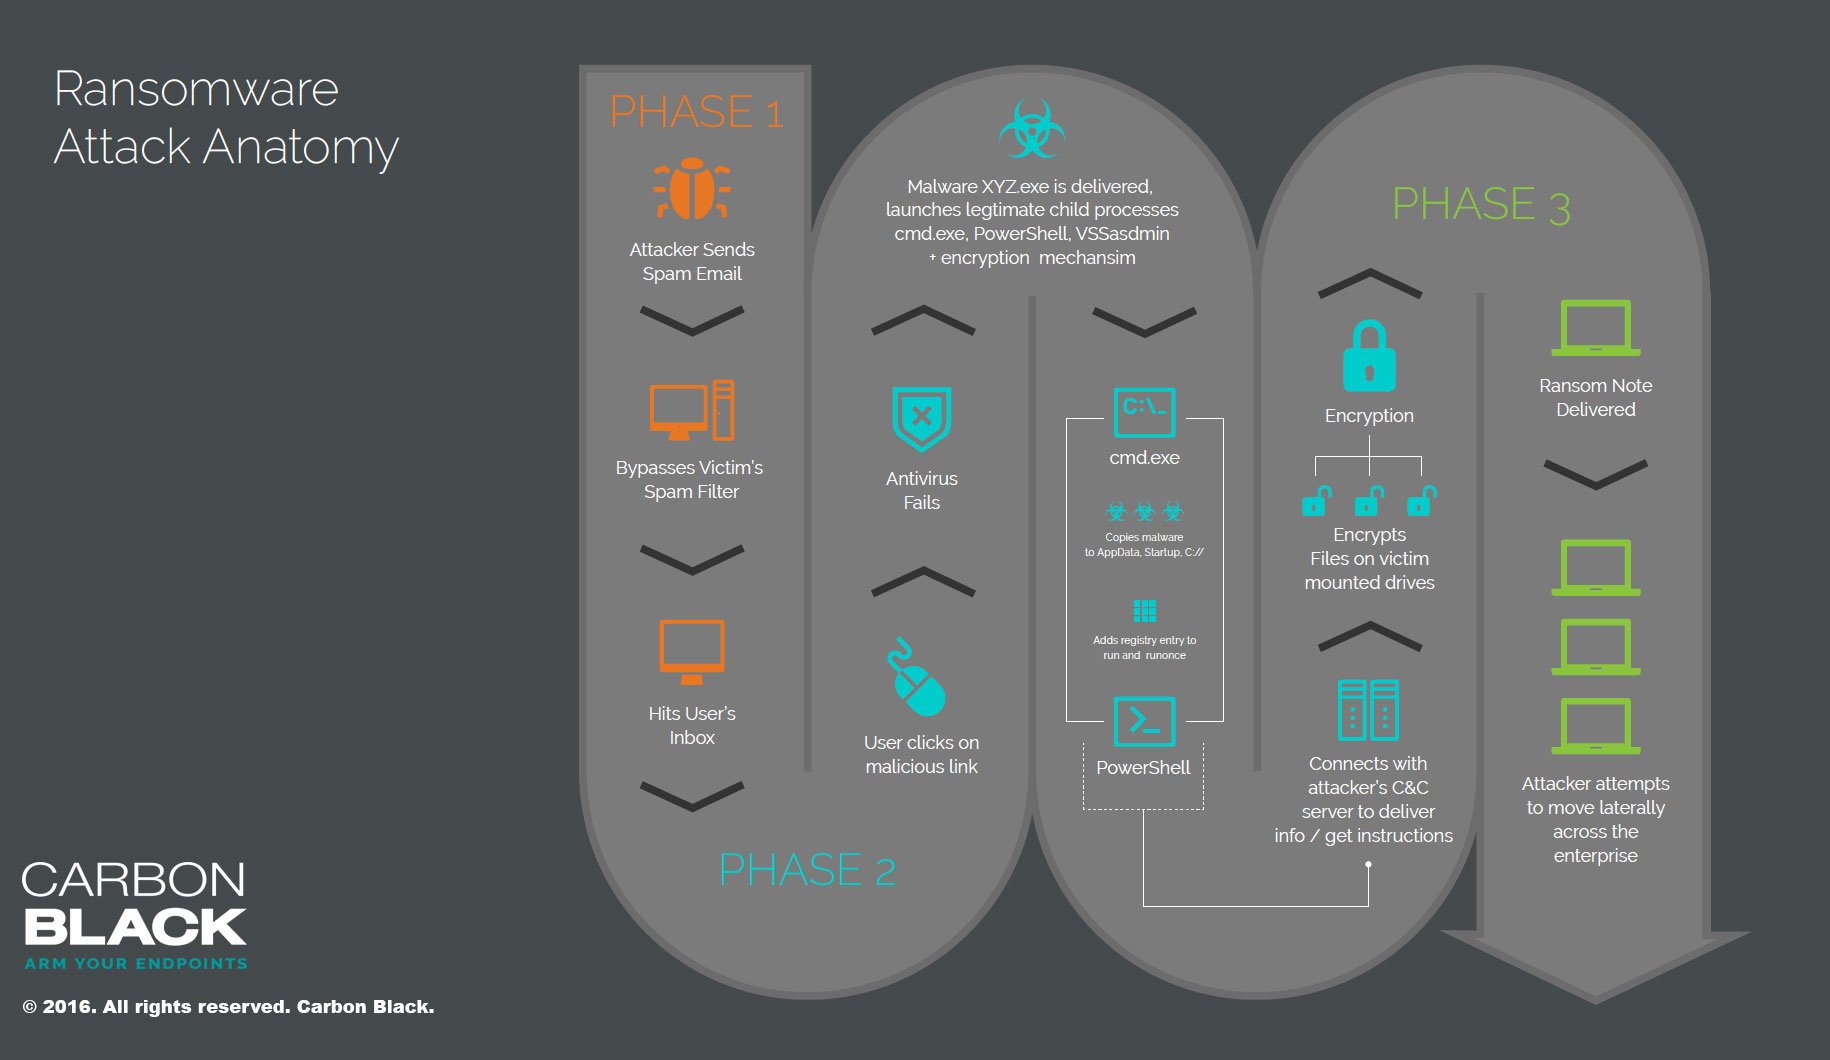
To quickly stop Petya right now - MS17-010 patch AND blocking ADMIN$ via GPO will stop lateral movement on WMI and PSEXEC.
#Petya

CaffeinatedSecurity retweeted

"Red is sexy, but we forgot our true calling - that BLUE is the one that has to win".
Gospel truth from @Sidragon1 at #bsidestlv
