

Co-founder @getfailsafe. Ex-CISO/eng leader @Grab, @Google. Writing on AI security, building companies, and lessons at 40.
Keeping the world safe
Joined April 2022
- Tweets2.4K
- Following7K
- Followers34.1K
- Likes5.2K




Pinned Tweet
#1 on the most difficult black box benchmark globally. nuff said.

Security through obscurity is not security.

despite the unfortunate timing, we take disclosures seriously at @typesafeai
at approximately 6:49PM this Friday evening, we became aware of a massive unauthorized leak of ALL customer noul outputs
in effort to maximize transparency, here is the link: gist.github.com/diogo149/810…
Advice to CISOs for 2027 - ask for budget for agentic tooling.


My biggest takeaway?
1 school kid with a flash subscription hacked the largest banks in South Korea in his dorm room, with no professional training.
Enterprises need to wake up and stop thinking security through obscurity (and some traditional security tools) will protect them in today’s world.

Last week some of South Korea's biggest banks were hit by a cyberattack. Thanks to a report from CrowdStrike tonight, we now know the entire hack may have been done by a single person. He used a combined stack of an open-source AI penetration tool named ARTEX, DeepSeek v4.1-Flash, GLM-5.3, Grok 4.6, and Claude Code.

Wui | FailSafe retweeted

If you're in Singapore for @F1 Week, Singapore @GovWare and @token2049, we're lining up a stellar set of events for our partners, clients, and friends:
👇🧵


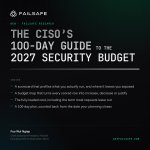
That's why the good people at @getfailsafe put together a plan -
The CISO's 100-Day Guide to 2027. A scorecard, a Master Budget Map (increase, decrease, justify, named vendors), and a 100-day plan to land a costed ask.
getfailsafe.com/cisobudget20…

In 100 days, your board will expect a response to agentic threats.
In 100 days, you're gonna be facing roughly 10x the number of agents probing your attack surface.
Are you ready?

Our @getfailsafe agent created this with one prompt and $6.80 in credits.
gg marketing agencies.
Wui | FailSafe retweeted
Announcing FailSafe's listing as a solution provider on the @MAS_sg Pathfinder Programme (PathFin.ai).
PathFin.ai is a collaborative initiative between the Monetary Authority of Singapore and the financial industry that fosters knowledge exchange in Artificial Intelligence (AI) implementations.
For financial institutions in Singapore, this means FailSafe’s agentic offensive security platform is now among the solutions available for consideration through the programme.
FailSafe SWARM continuously pentests applications, APIs, cloud and AI systems the way a real attacker would. Confirmed findings include proof-of-concept evidence, remediation guidance and audit-ready reporting, supported by traces showing how vulnerabilities were identified and validated.
The practical difference is cadence. Offensive testing that keeps pace with release cycles rather than arriving once a year. SWARM achieved the highest publicly reported score on CVE-Bench v2.1.0, an autonomous black-box exploitation benchmark, scoring 62.5% in the zero-day setting on a single run per target.
Let's chat about a new security model for the age of AI.

feels like a movie right there.

Wui | FailSafe retweeted
Attending @superai_conf ? Come for the closing event of the week, where our cofounder @0xWui will be chatting about agents, enterprise deployments and more!
luma.com/mqxgtrj5

@getfailsafe is hosting an enterprise agent mixer with @awscloud , @coinbase , @NEARProtocol and friends.
Agents are moving from demos to production. That means new questions around evals, security, runtime controls, and trust.
We’ve been spending a lot more time in the Bay lately as we deepen our R&D presence here. Come join us!


chad
FailSafe Swarm has been cooking with @nvidia's Nemoclaw, @NEARProtocol 's Openclaw, @NousResearch's Hermes and more.
Keeping the world safer, one PR at a time. receipts below 👇🧵
