
Doing my best to protect web3 protocols. Top 100 HackenProof all-time
Joined August 2025
- Tweets496
- Following411
- Followers428
- Likes448




I think the bigger question is whether there’s actually a way to prove, with absolute certainty, that an EVM contract is free from all possible asset theft exploits, rather than just proving that it satisfies a predefined set of security properties under certain assumptions 🤔
So you got Mythos 5.1 access with Defense tier in Cyber Verification Program? I just got accepted but I still getting refusals when trying to use Fable or Mythos
LoopGhost retweeted

Okay, are you kidding me?
At this point, OpenAI is treating us all like clowns.
Why did you even promise us 28 days of improvements to Codex or Work if you clearly couldn't deliver on that promise?
This is incredibly disappointing. I genuinely feel misled.
This is very true, and it’s what allowed me to build the AI workflow I use today and that has helped me uncover huge criticals on big protocols. Very good advice!
Your approach always seems to be blaming researchers and being unnecessarily hostile rather than working towards constructive solutions.
You also publicly misrepresented my situation, yet never bothered to respond when I challenged your claims and provided the actual context.
Perhaps you should take your own advice and try being a little more constructive.
Totally agree. This, combined with the fact that platforms consistently seem to favor projects over researchers in mediation decisions, makes the situation even more concerning
Always the same. Then everybody wonders why exploits happen to protocols that have bug bounties. Whitehats tend to be disrespected in many cases…
It’s always the same story. No matter what you uncover or how severe the demonstrated impact is, they’ll claim they already knew about the “root cause.”
They’ll thank you for the thorough analysis, then effectively take your impact demonstration for free. The very demonstration that finally pushes them to fix a “known issue” they had dismissed as harmless and left unpatched for over a year.
Apparently, knowing a root cause exists is the same as understanding its actual impact.
Same shit, every single time.
So if I want to submit a vulnerability I can’t because Immunefi cares 0 about their project’s security? What can I do now? I have a confirmed vulnerability to report, but I have no path for this disclosure
Probably this interesting bug writeup! And… unfortunately many hacks 🫠

Unfortunately, no updates. They don’t seem to care at all.
They responded by twisting the entire situation and bringing up events from over a year ago, completely ignoring the promises they made just weeks ago. I addressed all of that in my reply, and since then, complete silence.
I guess it’s easier to stay silent than to acknowledge that they failed to honor their own commitments.
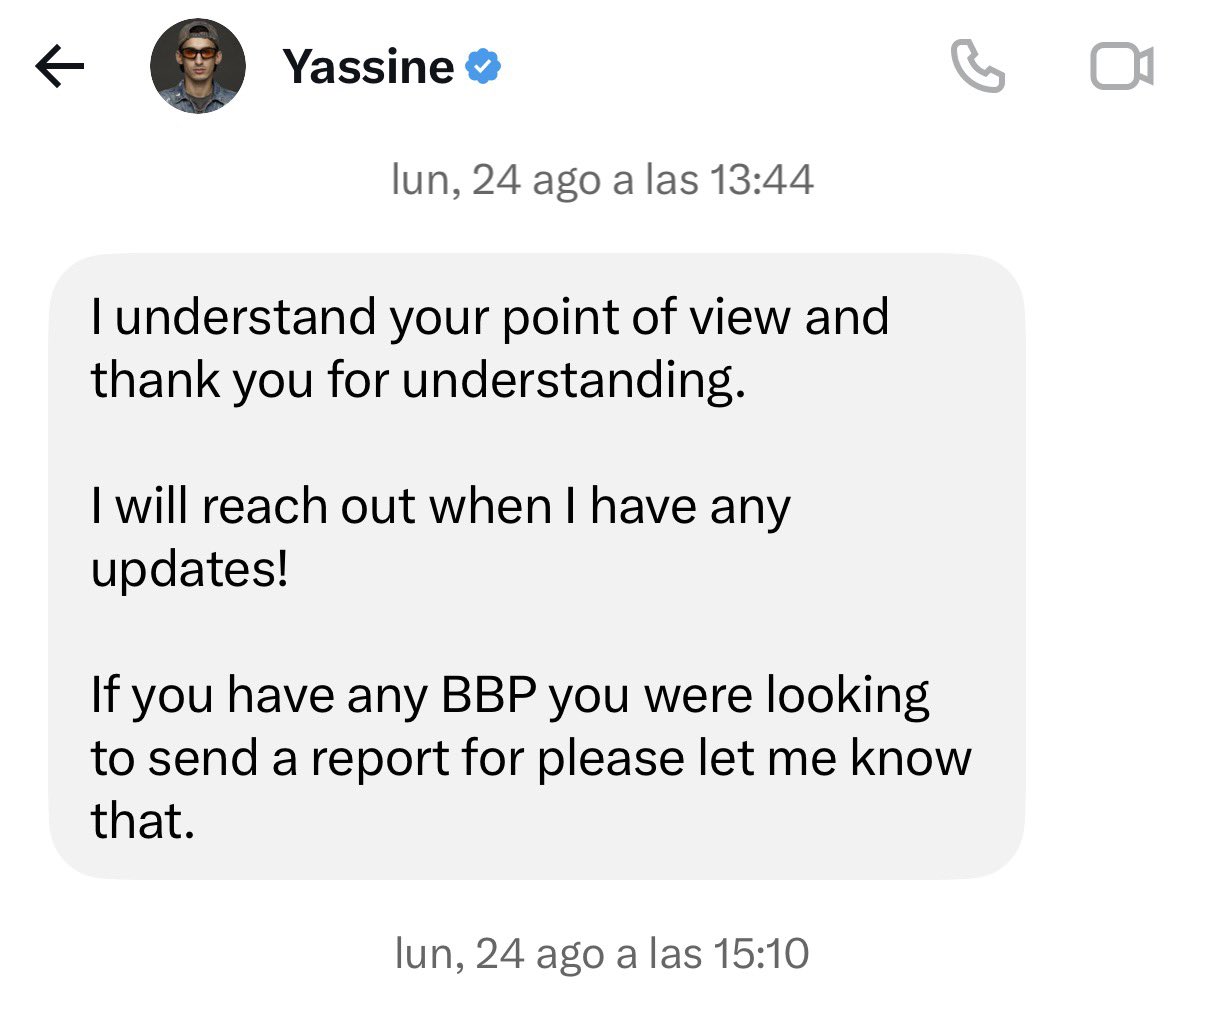
And here’s the proof of what Yassine personally promised me.
xitter.cf/loopghost007/status/21…



I’m not going to deny my past mistakes. Yes, my research is fully AI-assisted, and yes, I made many mistakes last year. I’ve acknowledged them and apologized to Immunefi privately countless times.
But those mistakes are precisely what allowed me to improve my AI-assisted research workflow and become the researcher I am today.
People make mistakes. People learn. People evolve. My current track record speaks for itself, and I’m not hiding any part of my past.
Immunefi itself introduced a program to give banned researchers who had improved their skills a second chance. Isn’t that exactly what this program was created for?
Despite my independently verifiable portfolio, I haven’t even been given the opportunity to demonstrate that progress.
And what disappoints me most is that Yassine personally promised to review my case and provide an answer by the end of September. He also offered to help me report vulnerabilities in the meantime. Neither commitment was honored. Instead, I was repeatedly ignored and ultimately blocked.
And since you mentioned @0xTimofey, I encourage you to contact him. I’m currently working on vulnerability reports involving companies collaborating with CertiK. Feel free to ask him for a reference regarding my current research and professionalism.
I’m not asking you to erase my history or excuse my mistakes. I’ve taken responsibility for them many times. I’m simply asking you to recognize that people can genuinely improve and to honor the second chance your own program was designed to offer.
I encourage you to take your time to read this.
I’m among the top 100 all time Hackenproof hackers btw and have saved more than one blockchain from a full drain already.
I’m not going to deny my past mistakes. Yes, my research is fully AI-assisted, and yes, I made many mistakes last year. I’ve acknowledged them and apologized to Immunefi privately countless times.
But those mistakes are precisely what allowed me to improve my AI-assisted research workflow and become the researcher I am today.
People make mistakes. People learn. People evolve. My current track record speaks for itself, and I’m not hiding any part of my past.
Immunefi itself introduced a program to give banned researchers who had improved their skills a second chance. Isn’t that exactly what this program was created for?
Despite my independently verifiable portfolio, I haven’t even been given the opportunity to demonstrate that progress.
And what disappoints me most is that Yassine personally promised to review my case and provide an answer by the end of September. He also offered to help me report vulnerabilities in the meantime. Neither commitment was honored. Instead, I was repeatedly ignored and ultimately blocked.
And since you mentioned @0xTimofey, I encourage you to contact him. I’m currently working on vulnerability reports involving companies collaborating with CertiK. Feel free to ask him for a reference regarding my current research and professionalism.
I’m not asking you to erase my history or excuse my mistakes. I’ve taken responsibility for them many times. I’m simply asking you to recognize that people can genuinely improve and to honor the second chance your own program was designed to offer.