

A crypto tracking and compliance platform for everyone. Built by @SlowMist_Team
Web3 Security
Joined March 2022
- Tweets2.5K
- Following237
- Followers25.8K
- Likes2.2K




MistTrack🕵️ retweeted
Four years ago, we built @MistTrack_io to make on-chain tracing and AML compliance analysis more accessible. Today, it’s trusted by 500+ institutions and 100,000+ users.
Whether you’re investigating fund flows, building tools, or managing compliance, we’ve got options for every budget 🔎
✅ Free tracing & wallet risk checks
✅ Premium from $229/month
✅ API from $20 for 100 calls across 19 chains
Explore what we’ve built → misttrack.io


🚨 MistTrack Fund Tracking 🚨
Drift Protocol Exploiter is moving funds.
💸 25,710 $ETH mixed via Tornado Cash
📌 Address: 0xAa843eD65C1f061F111B5289169731351c5e57C1
We’ll continue tracking the movement of these stolen funds.🕵️♂️
light.misttrack.io/address/E…

🚨 MistTrack Fund Tracking 🚨
CryptoBillis Ledger Drainer-related address is moving funds.
💸 ~463 $ETH transferred into Tornado Cash
📌 Address: 0x83aeaC166f6832aE3500000a24510a95a052A599
We’ll continue tracking the movement of these stolen funds.🕵️♂️
light.misttrack.io/s/Qler6


We’re seeing @tether freeze a significant number of $USDT across addresses linked to this incident.
Based on our current tracking, the reported losses are approaching $90 million. Some affected users have contacted us for assistance, and our team is actively following up on these cases.
bc1qjqgwejnp8dc0x2938x9n9954hj97t82unx49dl
bc1qqnkwurxs99xkx5t4yffqhq3u6qwy0qpjyujtm9
bc1qgqheemzla77pesl227hdtgf5ykz62d0zvld26n
TK6DWNpNe1w2iJRNFpU8aHdrPTATxvXT6C
TBkcUMYC7CkTK99tkTnaStQVBastfrs9d9
TCGE3xp6YGRKXxDZiLfysgJW3f22KfMNsW
TSDWtuZ2pARUVz4v3PkL2hi3iXPjowAr5a
0x69c8f401cfc6cd40ac94691d6d7c48e3b7a47841
0x033636e45d519bebb7b5c2520ca6ce56fbdb4f7a
0x83aeac166f6832ae3500000a24510a95a052a599
🫡 cc @SpecterAnalyst

Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: support.ledger.com/
🔎 The @bitget exploiter is moving stolen DAI on Ethereum through a series of swaps and cross-chain transfers:
DAI → USDT on Ethereum → USDT0 → Tron
💱 One recent transaction:
100,000 DAI → 100,034.89 USDT via #Uniswap.
etherscan.io/tx/0xe71fe8f06d…
🌉 The USDT was then transferred from Ethereum to Tron via #USDT0 infrastructure.
tronscan.org/address/TSjHkJL…
USDT0 OFT:
0x1f748c76de468e9d11bd340fa9d5cbadf315dfb0
Tron-side USDT0 OFT:
0x3a08f76772e200653bb55c2a92998daca62e0e97
On Tron, the funds continued moving via #SunSwap:
• 90,967 USDT → $USDD
• 19,000 USDT → $TRX
This activity is part of an ongoing flow from an address linked to the Bitget exploiter. The same address has been repeatedly converting $DAI to $USDT and bridging the funds to #Tron.
We’ll continue tracking the movement of the stolen funds across chains and services. 👀


🔎 MistTrack TrackAgent spotted a notable cross-chain pattern in the movement of funds stolen from Bitget: Using a CoW Protocol + Chainflip combination to automate cross-chain transfers.
The flow:
1) An automated script creates an order on #CoWProtocol.
2) The order’s recipient is set to a pre-prepared #Chainflip Deposit Contract address.
3) Once the order is executed, the assets enter Chainflip and are swapped across chains into BTC.
⤵️ One example:
Create Order on CoW Protocol:
etherscan.io/tx/0xae6b115344…
Order execution:
etherscan.io/tx/0xfcb591c1c6…
Chainflip Deposit Contract:
0xcEAE932A8bEE3a81a681A59890cb26d3110FDb65
Chainflip swap:
scan.chainflip.io/swaps/1861…
Destination BTC address:
bc1qa0rjjhyu9pg3adgpel4v7dct6a8606az863jyh
The interesting part is the automation: rather than manually interacting with each bridge or swap, the attacker can prepare the destination and let the flow execute once the order is filled.
We’ll continue tracking how the stolen funds move across chains and services. 👀


我们的 @MistTrack_io TrackAgent 发现朝鲜黑客采用 Cow Protocol + Chainflip 组合跨链操作:Bitget 被盗资金,朝鲜黑客自动化脚本通过 Cow Protocol 创建订单,订单收款地址设置为预先准备好的 Chainflip Deposit 相关合约地址,订单成功后即可完成在 Chainflip 的资产跨链操作,换成 BTC。
如这笔:
在 CoW Protocol 上创建订单:
etherscan.io/tx/0xae6b115344…
订单成交:
etherscan.io/tx/0xfcb591c1c6…
收款地址(即 Chainflip Deposit Contract):
0xcEAE932A8bEE3a81a681A59890cb26d3110FDb65
对应 Chainflip 记录:
scan.chainflip.io/swaps/1861…
跨链资产到 BTC 地址:
bc1qa0rjjhyu9pg3adgpel4v7dct6a8606az863jyh
@MistTrack_io @SlowMist_Team


The @bitget exploiter tried to move the stolen funds through @Chainflip.
Chainflip’s response?
“Deposit rejected by the broker.” 👋
No freeze, but no luck either — the funds were refunded. 👍
Nice try. 😶
We’ll continue tracking the movement of the stolen funds.
🔗 scan.chainflip.io/channels/1…


AGREE

Because multiple Asgardex contributors explicitly refused to return the ~$900K in fees you profited from the Bybit hack by DPRK.
Multiple of those teams you mentioned decided to return fees.
Choosing to keep Thorchain as decentralized as possible and not censoring activity at the protocol level is one thing.
Profiting fees off the hack (knowingly) and then refusing to return those fees after is criminal.
MistTrack🕵️ retweeted

THORChain 在美国当地时间 9 月 25 日实现了约 38.2 万美元收入,交易量超 2 亿美元。交易量创下了 4 月 23 日以来的第二高,仅次于 9 月 10 日的约 2.8 亿美元。cc @MistTrack_io
可笑的是这背后是犯罪分子的狂欢 🙂↕️

MistTrack🕵️ retweeted
I don’t think THORChain’s TSS + validator model represents true decentralization.
The selected validators set collectively controls the underlying assets in the TSS vaults. Once the signing threshold is reached, those validators can move the funds. So from a custody perspective, THORChain is not comparable to Bitcoin or Ethereum base-layer consensus — it effectively acts as an intermediary between users and the native chains.
TSS distributes control among multiple parties, but distributing an intermediary does not eliminate the intermediary.

We are devasted to hear about the recent exploit and can imagine how difficult this must be for everyone involved.
THORChain is decentralized and permissionless like Bitcoin, Ethereum, and BNB Chain.
What responsibility should Bitcoin, Ethereum, and BNB Chain bear when handling known stolen funds?
@star_okx @GracyBitget
MistTrack🕵️ retweeted

Our attacker addresses are publicly listed and actively tracked. We are formally asking @THORChain to refuse service to these addresses. Decentralization is a design principle, not a shield for facilitating known stolen funds.
The industry is watching.
THORChain and Stolen Funds: The Industry Needs Answers
After the $1.46B @Bybit_Official hack last year, nearly $1.2B in stolen funds was reportedly traced through @THORChain as the attackers moved assets across chains.
Today, following another major security incident at @Bitget , we are once again observing Bitget Exploiter funds being sent into the THORChain for asset swaps and cross-chain transfers.
The question is no longer:
“Does THORChain know these funds are associated with hackers?”
The attacker addresses have already been publicly flagged and are being actively tracked by exchanges, blockchain security/aml firms, and the wider crypto industry.
The real question is:
When a protocol is aware that funds originate from a publicly identified major hack, yet continues to facilitate large-scale cross-chain swaps, how should the industry view this under the banner of “decentralization”?
Decentralization should not become a blanket excuse when dealing with known stolen funds.
If, after every major crypto hack, attackers can continue using THORChain as a route to move funds from ETH → BTC, BNB → BTC, and across other chains, the industry needs to seriously ask:
What responsibility should THORChain bear when handling known stolen funds?
@GracyBitget @xiejiayinBitget @benbybit
Please use the official @Bitget API for hacker addresses; our Google Sheet will no longer be updated. bitget.com/support/articles/…

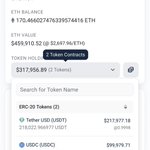
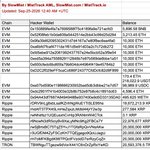
So far, we have identified the following addresses associated with the @bitget exploiter that still hold funds. We will continue to update this list. @GracyBitget @xiejiayinBitget @Bitget_zh docs.google.com/spreadsheets…

Tether banned the wallet owned by the bitget exploiter etherscan.io/tx/0xdd30e4831e…

So far, we have identified the following addresses associated with the @bitget exploiter that still hold funds. We will continue to update this list. @GracyBitget @xiejiayinBitget @Bitget_zh docs.google.com/spreadsheets…
THORChain and Stolen Funds: The Industry Needs Answers
After the $1.46B @Bybit_Official hack last year, nearly $1.2B in stolen funds was reportedly traced through @THORChain as the attackers moved assets across chains.
Today, following another major security incident at @Bitget , we are once again observing Bitget Exploiter funds being sent into the THORChain for asset swaps and cross-chain transfers.
The question is no longer:
“Does THORChain know these funds are associated with hackers?”
The attacker addresses have already been publicly flagged and are being actively tracked by exchanges, blockchain security/aml firms, and the wider crypto industry.
The real question is:
When a protocol is aware that funds originate from a publicly identified major hack, yet continues to facilitate large-scale cross-chain swaps, how should the industry view this under the banner of “decentralization”?
Decentralization should not become a blanket excuse when dealing with known stolen funds.
If, after every major crypto hack, attackers can continue using THORChain as a route to move funds from ETH → BTC, BNB → BTC, and across other chains, the industry needs to seriously ask:
What responsibility should THORChain bear when handling known stolen funds?
@GracyBitget @xiejiayinBitget @benbybit
MistTrack🕵️ retweeted
We’re working closely with @bitget on the ongoing investigation. For further details, please refer to Bitget’s official updates.

[UPDATES] We are currently working with independent third-party experts Mandiant and SlowMist for a full investigation.
Our first priority is our users. User balances remain intact, and Bitget's User Protection Fund covers the impact on this platform-wide incident.
Bitget Wallet operates as a self-custodial wallet on a completely separate and independent infrastructure from Bitget Exchange and was not affected by this incident.
Bitget Wallet users' assets remain onchain under users' control and remain unaffected.
The Bitget Exchange platform continues to operate normally.
Withdrawals are still temporarily paused while we complete additional security checks, and we will restore them as soon as we are confident that it is safe to do so.
We know that during an incident like this, users want answers quickly. We will provide timely updates through Bitget's official channels.
MistTrack🕵️ retweeted

来自 @SpecterAnalyst 的链上分析关联出朝鲜黑客历史上的有关资金。另外,这次手法上确实和之前朝鲜黑客相关组织的手法类似,包括资金归集习惯…
更多信息见 Bitget 官方披露就好,我们在协同调查中。

Regarding who is behind the hack:
I present to you THE LAZARUS GROUP.
just linked this hack to the AFX hack, which stole $24M in July and was specifically attributed to TraderTraitor.
The stolen XRP from Bitget was bridged and can be directly linked to the funds stolen in the AFX hack.
Stay smart.

So far, we have identified the following addresses associated with the @bitget exploiter that still hold funds. We will continue to update this list. @GracyBitget @xiejiayinBitget @Bitget_zh docs.google.com/spreadsheets…

[SECURITY NOTICE] Bitget Hot Wallet Incident — September 24, 2026
At 18:31 UTC on September 24, 2026, Bitget's security systems detected unauthorized transfers from some of our hot wallets. Our security team activated emergency response protocols immediately.
What we have confirmed:
-Estimated funds affected: approximately $351.6 million
-Cold wallets remain fully secure. Bitget operates a three-tier wallet architecture — the breach contained only a portion of the hot wallet and warm wallet layers.
-User funds are safe. The full amount of this loss falls within the coverage of Bitget's User Protection Fund, which currently holds over $464 million
Actions we have taken:
-Emergency response team activated within minutes of detection
-Abnormal transfer addresses identified, flagged, and reported
-Withdrawals temporarily suspended as a precautionary measure, pending security review
-Law enforcement and on-chain security firms have been formally notified and are engaged
What this means for you:
-Your account balances are accurate and your assets are protected
-Deposits and trading remain fully operational
Withdrawals are temporarily paused and will be restored as soon as the security review is complete
-What comes next: We will provide updates on an hourly basis across this channel and all official platforms. A full incident report — including root cause analysis and corrective actions — will be published within 24 hours. We will not speculate on the attack vector until the investigation is complete.
Bitget has navigated multiple market cycles. We will not run from this. Every dollar and every decision will be accounted for, transparently and in full.
Updates will be posted here and across all official Bitget channels as they become available.
— Gracy Chen, CEO, Bitget

All hacker addresses have been tagged. We’re actively monitoring fund transfers and expanding our blacklist. We remain fully committed to combating illicit transactions.
[SECURITY NOTICE] Bitget Hot Wallet Incident — September 24, 2026
At 18:31 UTC on September 24, 2026, Bitget's security systems detected unauthorized transfers from some of our hot wallets. Our security team activated emergency response protocols immediately.
What we have confirmed:
-Estimated funds affected: approximately $351.6 million
-Cold wallets remain fully secure. Bitget operates a three-tier wallet architecture — the breach contained only a portion of the hot wallet and warm wallet layers.
-User funds are safe. The full amount of this loss falls within the coverage of Bitget's User Protection Fund, which currently holds over $464 million
Actions we have taken:
-Emergency response team activated within minutes of detection
-Abnormal transfer addresses identified, flagged, and reported
-Withdrawals temporarily suspended as a precautionary measure, pending security review
-Law enforcement and on-chain security firms have been formally notified and are engaged
What this means for you:
-Your account balances are accurate and your assets are protected
-Deposits and trading remain fully operational
Withdrawals are temporarily paused and will be restored as soon as the security review is complete
-What comes next: We will provide updates on an hourly basis across this channel and all official platforms. A full incident report — including root cause analysis and corrective actions — will be published within 24 hours. We will not speculate on the attack vector until the investigation is complete.
Bitget has navigated multiple market cycles. We will not run from this. Every dollar and every decision will be accounted for, transparently and in full.
Updates will be posted here and across all official Bitget channels as they become available.
— Gracy Chen, CEO, Bitget
如果你手机上安装过 FomoPeek 而且最近有被盗,可以把被盗地址、黑客地址提交给我们 aml.slowmist.com/cn/recovery…
⚠️最近一些 iPhone 用户的钱包被盗,是因为安装了 FomoPeek 这个 App,v1.1-1.2 主要版本引入了恶意 SDK,其包含一套专业的 iOS 内核攻击框架,集成 8 种漏洞利用方案,可根据设备型号及系统版本自动选择攻击方式,已知受影响 iOS 版本:iOS 12.0–18.7、26.0–26.1。
攻击成功后,该 App 可突破 iOS 沙盒隔离机制,进而读取并解密系统钥匙串(Keychain),并访问设备上其他 App 的数据文件。用户存储在设备中的私钥、助记词、登录凭据、聊天记录及文件等,均可能因此面临泄露风险。此外,该 App 还会连接与公开业务无关的隐蔽服务器,接收远程指令。
⚠️⚠️⚠️这里重点做个提醒,由于该手法已经开始泛滥,iPhone 千万不要下载不明 App。
并保持 iPhone 及时更新到最新版本,比如现在是 27(不代表以后不会有风险,攻防对抗永远在升级)。
具体细节见我们的推文👇
