

Onchain Investigator | Peace ✌️ Specteranalyst.sol (.eth)
Joined May 2024
- Tweets14.4K
- Following463
- Followers16.3K
- Likes25K




Specter retweeted
For those who don't know how to identify stolen funds, it's often pretty easy.
One way to identify a potentially compromised wallet is to look for a sudden change in its established transaction patterns.
For instance, TQKJQ, a CoinDCX deposit address, had consistently been sending funds to the entity's hot wallet. Then, suddenly, wallets associated with the entity, including TQKJQ, were swept into a single wallet, which began distributing funds, swapping assets, using OTC services, and more.
That's a potential sign of a compromised wallet.
So, the point is: CoinDCX and its co-founder are lying.


Specter retweeted
It's crazy that CT has such a short memory. Scammers, grifters, and rug pullers are quickly forgotten.
There seems to have been a coordinated push around @kimchi1x, with CT claiming that he "made eight figures from the TRUMP token." lol
I decided to look into @kimchi1x . Based on my on-chain analysis, he and his group, including @orangie , have exposure to token launches, bundling, and rug pulls.
Since this thread is about Kimchi, I'll focus on him.
Wallet (publicly shared by Kimchi in a reply on X back in April 2024):
2yu3iNjH6zLa8Uqf1s4yKJ1kB9MHYPhMkDbpu8tLmBMC
Example 1 – $STAR
On May 30, 2024, at 13:41 UTC, $STAR was deployed. Within the same minute, the wallet linked to Kimchi bought 2.96 SOL ($407) and later sold the position for $45.6K.
Tx:
zWstdZjTHRGzPSEX5NPnfv7QS2412iroNx1HpwHNRBwu6UeyNA57ZMRcZRFfmDSi4V3uF7yHshA1YBKi3TncnF1
Example 2 – DADDY ANSEM
On June 11, 2024, at 23:38 UTC, DADDY ANSEM (not launched by Ansem) was deployed. Two minutes later, the wallet linked to Kimchi bought 4.94 SOL ($730) and later sold it for $14.6K.
Tx:
4DqJrynmKbaLLjPKLzZYfZwGPxSKtBCirH2Du2vDdd5Z7sfaGfA89W15x4VBzM5wzdm8BiMVA5xk1M8M9UGUut9c
Example 3 – MUVA
On June 26, 2024, at 22:45 UTC, MUVA was deployed. One minute later, the wallet linked to Kimchi bought 2.9 SOL ($407) and later sold the position for $53K.
Tx:
55ZSNgEMDQRKvAvhcSYicrUnPoxuTV1iUR5FdSVoFK7GGXJ4S2rAtEoZ62wh7S4F39DMAHN5guoxfAmpSQwWfwS7
An exchange deposit address also clusters five other wallets that bundled the same MUVA launch.
These are just a few examples. I decided not to dig through the wallet's entire bundling history.
they have a private group known as @pioneerfnf
While there is no verifiable evidence that @kimchi1x made eight figures from the TRUMP token, it's crazy to see someone with this kind of on-chain history being pushed as a role model.
It's crazy how CT celebrate grifters and rug pullers even after knowing who they are.
Stay smart.


Since ZachXBT posted about the Bitget attacker shielding stolen funds via Zcash (ZEC), we’ve seen other stolen funds flow into ZEC, including funds from the Cryptobills Ledger incident and the $12M Triple-A hack.
Threat actors are actively using ZEC to move stolen funds.
Stay smart.

There have been a reports on X and Reddit of wallet-draining by Ledger users.
I traced the theft addresses and identified inflows from more hundreds of victim wallets across several major blockchains, including Ethereum, TRON, and Bitcoin.
Total losses $86M+
bc1qjqgwejnp8dc0x2938x9n9954hj97t82unx49dl
TK6DWNpNe1w2iJRNFpU8aHdrPTATxvXT6C
TBkcUMYC7CkTK99tkTnaStQVBastfrs9d9
TCGE3xp6YGRKXxDZiLfysgJW3f22KfMNsW
0x69c8f401cfc6cd40ac94691d6d7c48e3b7a47841
0x033636e45d519bebb7b5c2520ca6ce56fbdb4f7a
0x83aeac166f6832ae3500000a24510a95a052a599
bc1qqnkwurxs99xkx5t4yffqhq3u6qwy0qpjyujtm9
bc1qgqheemzla77pesl227hdtgf5ykz62d0zvld26n
TSDWtuZ2pARUVz4v3PkL2hi3iXPjowAr5a


Specter retweeted
I spent about 13 minutes reading this, and I must say, this is incredible. Just imagine the amount of risk involved and the money spent throughout this investigation.
I hope Jimmy gets what he deserves, and that his fat-reducing meals are served with plenty of water in prison.
Great job, ser. 👏


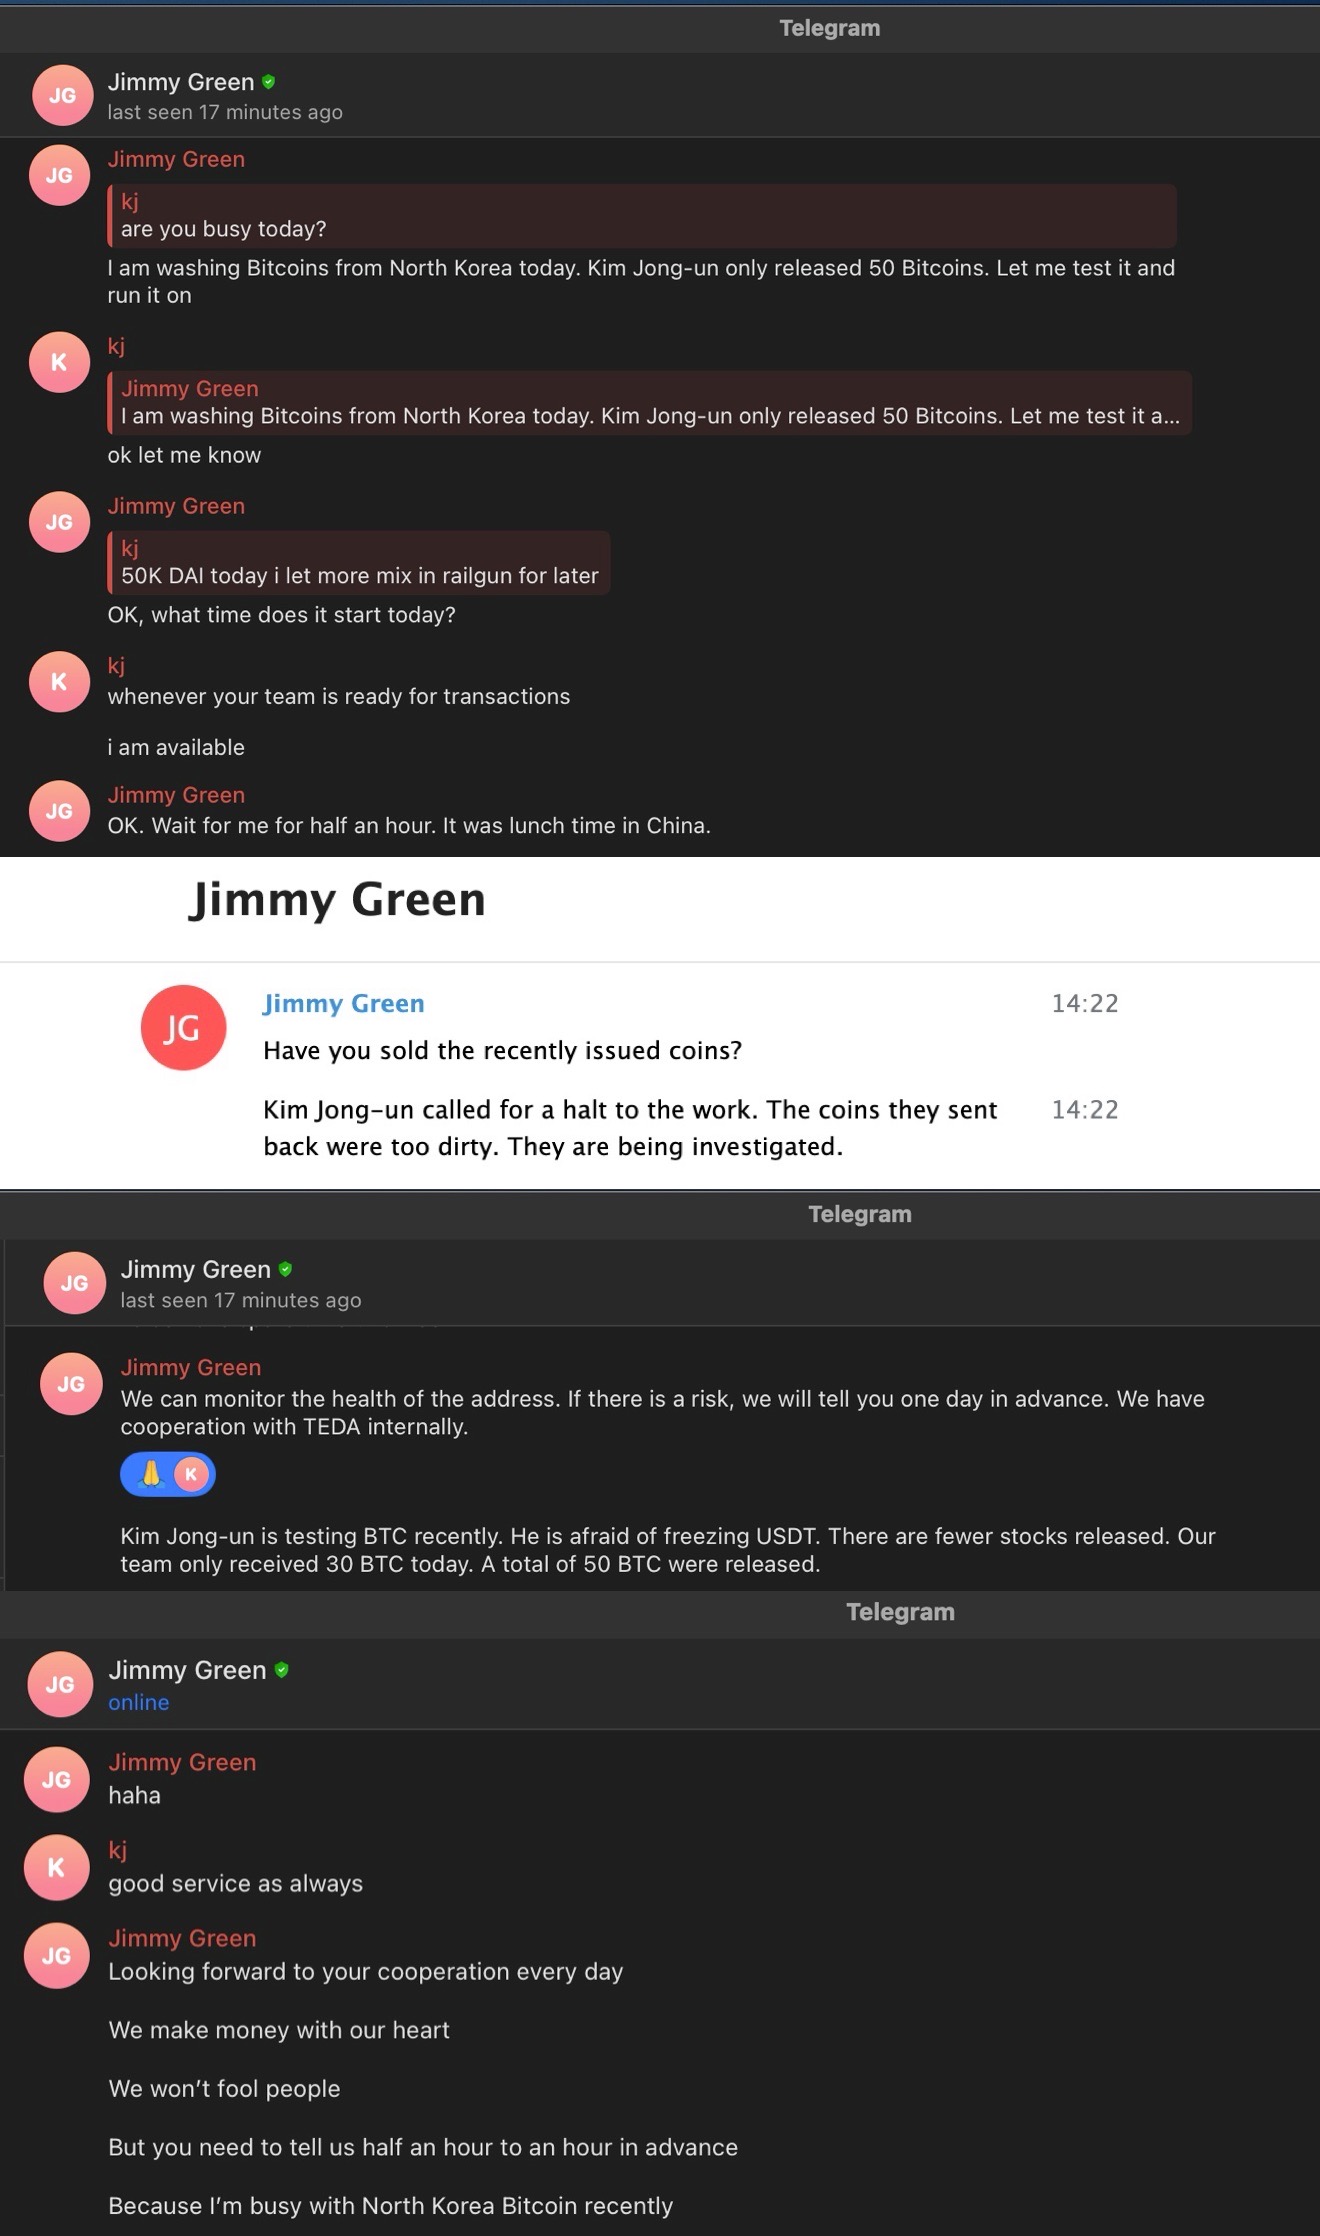
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

I spent about 13 minutes reading this, and I must say, this is incredible. Just imagine the amount of risk involved and the money spent throughout this investigation.
I hope Jimmy gets what he deserves, and that his fat-reducing meals are served with plenty of water in prison.
Great job, ser. 👏
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.
I also contributed to freezing of 173k XRP ($257K) via near intents (yet to be awarded to me)
Thanks to near team for swift action


Specter retweeted
If there was no THORChain, shit would be hell for these guys😑.
They’re laundering funds across several chains, even on bottom chains like dYdX, Noble, and Osmosis. So annoying.
How stupid can you be to publicly post txs link of stolen funds that are being tracked by the public? very soon....
BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen laundering funds from the Kelp DAO $292M exploit earlier this year.
I've observed the same pattern after multiple TraderTraitor attributed exploits, and I've closely tracked these groups. I plan to share more of my data on them in coming weeks.
Currently, funds are being chain-hopped via bridges and being deposited into mixing services such as Wasabi.
Alias 1 - Cc
Discord: cc02006
Discord ID: 1351486674386948148
Txn: F08657EFAEAE7B58217CD17A22BF4779582E5D080C2E92E173BC239A5D828363
Alias 2 - jack
Discord: jack_34808
Discord ID: 1553705721768714377
Txn: 68583D313A0CCC99F2702D61D05A242A69C86CAE09ED252B65F34B677C377F69
Alias 3 - Melon
Discord: under0346
Discord ID: 1394240539108573215
Txn 1: ABE2AEF8B10057E60F8259CA2CA2CD5D71D38D254960FEEE89CB3C95A964873F
Txn 2: 7BE290865901DEB1680A6D692A11392D1FDDACA0D31C48F26DCB249F2444BD6B
Alias 4 - lolo / Marin
TG: pvpcz
TGID: 6223514198
Discord: losern
Discord ID: 1024415186527985704
Txn: 8E935C19D00F40639B78BF1FD094FE48C92118F3E586AB52DF93851080CCCE15
Alias 5 - HELP ME
Discord: helpme031897
Discord ID: 1554035533817188384
Txn: 7C58CAD760EBBED54F2CA4D2146D056910B7B6688B4F524396DC8807353C2379
Specter retweeted

THORChain and Stolen Funds: The Industry Needs Answers
After the $1.46B @Bybit_Official hack last year, nearly $1.2B in stolen funds was reportedly traced through @THORChain as the attackers moved assets across chains.
Today, following another major security incident at @Bitget , we are once again observing Bitget Exploiter funds being sent into the THORChain for asset swaps and cross-chain transfers.
The question is no longer:
“Does THORChain know these funds are associated with hackers?”
The attacker addresses have already been publicly flagged and are being actively tracked by exchanges, blockchain security/aml firms, and the wider crypto industry.
The real question is:
When a protocol is aware that funds originate from a publicly identified major hack, yet continues to facilitate large-scale cross-chain swaps, how should the industry view this under the banner of “decentralization”?
Decentralization should not become a blanket excuse when dealing with known stolen funds.
If, after every major crypto hack, attackers can continue using THORChain as a route to move funds from ETH → BTC, BNB → BTC, and across other chains, the industry needs to seriously ask:
What responsibility should THORChain bear when handling known stolen funds?
@GracyBitget @xiejiayinBitget @benbybit
Specter retweeted
Regarding who is behind the hack:
I present to you THE LAZARUS GROUP.
just linked this hack to the AFX hack, which stole $24M in July and was specifically attributed to TraderTraitor.
The stolen XRP from Bitget was bridged and can be directly linked to the funds stolen in the AFX hack.
Stay smart.


Specter retweeted

The #1 reason you don't want to launder money for DPRK is that DPRK will absolutely hack you.
RIP Bitget. TraderTraitor says thank you for your service.
0xCbCfd64A96837D874943641fc9BA159C10d6CC80 -> 0xA0772d6E70D2c97CFB70628C7B00f666A6476feb


Regarding who is behind the hack:
I present to you THE LAZARUS GROUP.
just linked this hack to the AFX hack, which stole $24M in July and was specifically attributed to TraderTraitor.
The stolen XRP from Bitget was bridged and can be directly linked to the funds stolen in the AFX hack.
Stay smart.
Regarding who is behind the hack:
I present to you THE LAZARUS GROUP.
just linked this hack to the AFX hack, which stole $24M in July and was specifically attributed to TraderTraitor.
The stolen XRP from Bitget was bridged and can be directly linked to the funds stolen in the AFX hack.
Stay smart.

Specter retweeted
Total loss: $353M
The remaining addresses
rwNhefsz1UQEusxhCvHip3RANinWi4CTck
rDRV9nLg8xbLsafKZnhNgWuE1TiSLE95hs
TBWNguTTgezw9dVorX441C6nDrZpRxYwKD

Where tf is bitget team @BitgetWallet @GracyBitget
Another $8.2M was just withdrawn on avalanche
Loss: 185M
Total loss: $353M
The remaining addresses
rwNhefsz1UQEusxhCvHip3RANinWi4CTck
rDRV9nLg8xbLsafKZnhNgWuE1TiSLE95hs
TBWNguTTgezw9dVorX441C6nDrZpRxYwKD
Where tf is bitget team @BitgetWallet @GracyBitget
Another $8.2M was just withdrawn on avalanche
Loss: 185M
Where tf is bitget team @BitgetWallet @GracyBitget
Another $8.2M was just withdrawn on avalanche
Loss: 185M