

🛸Research Team of @Orbiter_Finance Cutting-edge ZK Tech exploration #OminiRollup #ZK
Layer 2 and Cross-rollup
Joined November 2022
- Tweets343
- Following160
- Followers6.6K
- Likes120




Orbiter Research🛸 retweeted

Ohno, the famous author of 2 EIPs is no longer .eth. Don't forget to close the door on your way out bro.
Formal verification is crucial to the security of decentralized protocols, especially for financial products like cross-chain bridges. We've prioritized the security of our bridge @Orbiter_Finance since day one.
We're excited to share our collaborative research with Prof. Feng (@captain8299) and his team from UCSB(@ucsantabarbara) and Kyle(@kcharbo0) from PSE(@PrivacyScaling) and Luke(@lukejdpearson) from Polychain(@polychain) where we developed a novel formal verification model to evaluate the mainstream cross-rollup bridges including Orbiter Bridge protocol!
Check out the work-in-progress paper:
eprint.iacr.org/2024/1834

Orbiter Research🛸 retweeted
Articles/threads
• ZK Hack Montréal Recap | ZK Hack
zkhack.dev/2024/09/02/zk-hac…
• The Elegant Foundation: Plonkish Arithmetization | Psycho Virtual
psychovirtual.io/posts/mina_…
• What Does It Mean To Know? | Samuel Spitz
mirror.xyz/0x62D8aAfD495613C…
• Glue and Coprocessor Architectures | Vitalik Buterin
vitalik.eth.limo/general/202…
• Hashing It Out: coSNARKs at TACEO | TACEO
blog.taceo.io/hashing-it-out…
• Web Proof, Make More Data Verifiable | @samoyedali
paragraph.xyz/@moyed/webproo…
• Ova: A Slightly Better Nova | Benedikt Bünz
hackmd.io/V4838nnlRKal9ZiTHi…
• The (Zero-Knowledge Proof) Singularity Is Near | Coindesk
coindesk.com/opinion/2024/09…
• Turbocharged Zero-Knowledge Proofs for Mobile | Reclaim Protocol
blog.reclaimprotocol.org/pos…
• Introduction to Interactive Proofs and Mina | Psycho Virtual
psychovirtual.io/posts/mina_…
• Cracking Proofs: The Benefits of ZKPs and Fraud Proofs | Lagrange
lagrange.dev/blog/cracking-p…
• Cracking ZK Coprocessors: Scaling Onchain Computation | Lagrange
lagrange.dev/blog/cracking-z…
• The Hitchhiker's Guide to Scaling Bitcoin with STARKs | Omar Espejel
espejel.substack.com/p/the-h…
• Solving Reproducibility Challenges in Deep Learning and LLMs: Our Journey | Ingonyama
medium.com/@ingonyama/solvin…
• Data as a New Asset Class | Zap
medium.com/@0xzap/data-as-a-…
• (Re)Introducing Kimchi: How the Berkeley Upgrade Transformed Mina's Proof System | o1Labs
o1labs.org/blog/reintroducin…
• Plonk: A Mathematical Overview of this Proof System | Aligned
mirror.xyz/0x7794D1c55568270…
• RISC-V ZKVMs: the Good and the Bad | Argument
argument.xyz/blog/riscv-good…
• Provable Watermark Extraction | Ingonyama
medium.com/@ingonyama/provab…
• Fake GLV: You Don't Need an Efficient Endomorphism to Implement GLV-like Scalar Multiplication in SNARK Circuits | Youssef El Housni
ethresear.ch/t/fake-glv-you-…
• Introduction to Polynomial Commitment Schemes (PCS) | Aligned
mirror.xyz/0x7794D1c55568270…
• Binius: Surfing on Binary Fields | Taiko
taiko.mirror.xyz/quzxgRJtj5r…
• The Acceleration of zkEVM Prover | Orbiter Finance
orbiter-finance.medium.com/t…
Being confused that what’s the usecase of preconf if it can not provide us with the finality?


In our quest to run ZK Rollup provers on more cost-effective hardware while maintaining the timeliness of ZK proofs, we've conducted a fascinating and comprehensive trade-off study. We're excited to serve up the results of our research – a smorgasbord of innovations we've been cooking up just for you!
orbiter-finance.medium.com/t…
#ZKRollup #Blockchain #Innovation
We should try to build decentralized systems on math-based security assumptions rather than centralized license-based ones. Don't take any unnecessary risks.


Congrats @IrreducibleHW , yet another ZK-VM !

Irreducible has joined the list of contributors developing the AggLayer 🌊
Polygon Labs and @IrreducibleHW are building a production-grade zkVM based on Binius, bringing the breakthrough properties of binary fields to the problem of verifiable, offchain computing.

Big congratulations to the Mina community on the Berkeley Update! This marks a new era for Mina Protocol, where Proof of Everything sets sail.
Proof of Everything is a game-changer. At @Orbiter_Finance , we're focused on providing a seamless experience across Ethereum ecosystems with our innovative @Vizing_L2 solution. While we operate in different domains with unique goals, our shared passion for Zero-Knowledge #ZK technology unites us. Mina's lightweight 22KB blockchain showcases the beauty and immense potential of ZK.
Recently, Vizing launched the interoperability of our omnichain services, powered by ZK technologies. We're also tackling data availability, integrity, and scalability challenges within #Ethereum ecosystems. We look forward to more opportunities to collaborate and contribute to the ZK community in the future. Together, we're shaping the future of blockchain!
#Mina #Vizing #ZeroKnowledge #ZK #Orbiter

A new paradigm— do you see it?
From the beginning, Mina Protocol was designed differently.
The mainnet launch in 2021 introduced a brand new lightweight blockchain that eliminates bloat, paving the way for low operating costs and unprecedented decentralization at scale.
This was thanks to a breakthrough in zero knowledge cryptography: a blockchain with its entire state inside a tiny proof of just a few kilobytes, that anyone could download and verify in milliseconds.
Now, the recent Berkeley upgrade extends these revolutionary ZK features to real-world applications. It empowers developers to build off-chain and verify on-chain for scale, customizability, cost-efficiency, and optional privacy.
Beyond scalability and privacy, Mina now can serve as a global database of verified statements that seamlessly interact with one another— a ‘Proof of Everything.’
More than just attesting to individual statements of facts, Mina’s true potential will be realized by those who use it to harness the power of one massive collaborative computation.
So, what will you build?

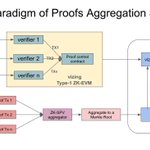
We may add another solution which is by utilizing Type1 ZKEVM, that means most stable/existing zk application can seamless migrate their proof verification (solidity verifier) without lost security. Morden CPU and GPU will effective enough to reduce the latency.


Why all the proof aggregation solutions will use RISC-V zkVMs
The development of RiscV proving vms like @RiscZero, @SuccinctLabs, @a16zcrypto, and @lita_xyz will transform how we work with zk. For example, aggregation layers will use them to perform recursion efficiently.🧵
1/

Yahoo!! After two weeks, we achieved 6X improvement in proving a batch of 20 ECDSA signatures, reducing the proving time from 72.4s to 11.4s 🚀. The time for computing wire commitments in the prover, accelerated by a 4090 GPU and involving a Merkle tree with 2^24 leaves and a leaf size of 136 Goldilocks, has a 22X improvement (29.1s to 1.3s). We extend our gratitude to the ZK community, especially the teams at @0xPolygon and @the_matter_labs , from whom we have learned a great deal!


ENS will be offloaded to a specified Layer2. For the past & current, a complex task can be executed in ONE tx ONE network, in the future, this will be executed in SEVERAL txs SEVERAL networks.

Our engineer have conducted a thorough analysis of the overhead of proof verification, comparing Groth16 and FFLONK. Every comment is strongly supported by practical results! Here is the dish we have been preparing for you 🍕:
orbiter-finance.medium.com/m…

If you wanna get more details, pls read this: hackmd.io/Fa4A8lVKRM2TwVh1dh…
