


Pinned Tweet
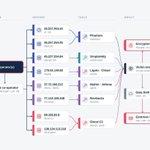
A Joint Operation by #Lynx and #INC Ransomware Groups: #FortiBleed
FortiGate Credentials → Ransomware Deployment
We've unmasked the actors behind the campaign.
An affiliate's mistake exposed both groups' members.
Want to know who they are, and how we tracked them?
Check out the report: socradar.io/resources/whitep…

Faruk retweeted

No exploits. Just stolen credentials and $7,200+ worth of AI coding agents.
A staging server exposed the n0n ransomware group’s pipeline:
→ 829 custom scripts
→ 305 FortiGate VPNs targeted
→ $283.7M demanded across 27 countries
Link in comments.
#Ransomware #ThreatIntel
🚨 New Research | AI-Assisted #Ransomware Operation Exposed
We identified an exposed n0n #Ransomware operator server, revealing an AI coding agent environment, the n0n locker source code, a C2 panel, and the group’s full extortion pipeline.
Key findings:
- 23 Identified Victims across 14 countries (7 US-based)
- $7.2K+ AI spend, mostly on “abliterated” models
- Credential-only access: FortiGate SSL-VPN spraying, exposed AWS keys, weak RDP
- Victim’s Cisco FMC hijacked to cut an ISP’s network
- S3 buckets and backups wiped for leverage
- n0n locker reusing hardcoded keys across victims
Blog: socradar.io/blog/n0n-ransomw…
Whitepaper: socradar.io/resources/whitep…
#ThreatIntelligence #CTI #ThreatHunting


Faruk retweeted
One exposed attacker server, 2 phases of the same operator:
→ Oct 9–11: a reused SSH key turned 1 breach in Japan into nearly 20 more sites
→ Oct 21 on: weaponized PHP2Shell exploits aimed at PHP hosts
Full Analysis:
socradar.io/blog/php2shell-w…
PHP2Shell Checker: socradar.io/free-tools/php2s…
#ThreatIntelligence #PHP2Shell
🚨 148 Million Brazilian PII Records Exposed
A misconfigured Elasticsearch instance was discovered, potentially exposing over 148 million records containing Brazilian citizens' personally identifiable information (PII).
The exposed data includes:
- CPF (Brazilian taxpayer ID) numbers
- Full names
- Dates of birth
- Residential addresses and postal codes
- Phone numbers
Validation: Sample records were cross-checked against Brazil’s official CPF registry, confirming matching identity details.
The dataset shares similarities with previously reported Brazilian data leaks, including the massive 2021 breach. However, its original source remains unconfirmed. Reported to the hosting provider.
⚠️ Risks: Identity theft, financial fraud, targeted phishing, and social engineering.
#ThreatIntel #CyberSecurity #DataBreach

Faruk retweeted

🚨 Exposed infrastructure reveals how ransomware affiliates used AI to hack networks and steal data.
8,257 messages. 133 AI sessions. 62 organizations targeted.
Operators exploited Fortinet, SimpleHelp, and cPanel flaws.
Inside the operation ↓ thehackernews.com/2026/10/ex…

Faruk retweeted

🚨 EXPOSED SERVERS REVEAL AN AI-ASSISTED RANSOMWARE WORKBENCH TIED TO INC AND THE GENTLEMEN
A threat research report published Oct 20, 2026 describes seven exposed adversary servers used by affiliates of the INC and The Gentlemen ransomware operations, with 62 targeted organizations and more than $23,920 spent on commercial AI services. The investigation began in late September, after operator OPSEC failures left the servers' open directories exposed.
What the report says the servers held:
• OpenCode AI session logs (8,257 messages across 133 sessions) using commercial models: the AI planned recon, generated commands and triaged stolen data, but waited for the human operator's approval before every step
• Source code for "Phantom", an autonomous red-team framework with 18 skill modules, alongside Ghost C2, RevSocks, MCP servers and exfiltration tools; plus extortion procedures and scripted vishing
• 46 custom INC encryptor builds for six victims, packed on Sep 30 for a planned Oct 1 deployment wave
• A Sep 30 screenshot showing the encryptor running on one victim workstation
• Operator records of mass exploitation of FortiClient EMS (CVE-2026-35616), SimpleHelp (CVE-2024-57727) and cPanel/WHM (CVE-2026-41940); those counts are the operators' own and not independently verified
⚠️ Analyst Note:
This is firsthand research from the team that found the servers, not independent validation. The researchers link the workbench to both INC and The Gentlemen operations but rate a formal alliance as low confidence; a shared tooling environment used by several partners is the more likely model. Staged builds do not prove deployment: the planned Oct 1 encryption wave is unconfirmed beyond the one workstation screenshot. The report grades organizations by depth of activity, including reconnaissance-only targets; DDW does not name them, and none should be read as a confirmed breach. Defenders: patch FortiClient EMS, SimpleHelp and cPanel/WHM, check EMS for unauthorized admin accounts, and lock down RMM tools.
Source: socradar.io/resources/whitep…
#DDW #DarkWeb #Ransomware #AISecurity #INCRansomware #TheGentlemen #ThreatIntelligence

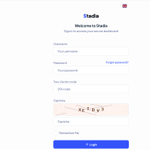
New #RAT: Stadia, developed by the author of #StealC
Live C2 Panel: 93.152.220[.]30
Advertised capabilities:
- Browser-based HVNC (shared/hidden desktop)
- StealC v3.5-based stealer
- In-memory/disk loader, remote CMD, file & process management
- Targets 50+ browsers, 120+ crypto extensions & 50+ wallets
- Crypto wallet brute-force functionality
Plymouth TA stated: "All StealC customers are offered a free month with the Pro plan!"
Additional C2 IPs:
2.27.248[.]147
45.194.66[.]165


Well... our research actually uncovered a custom MCP server called "ransom-ops" that handles much of this, including negotiation strategies, victim response analysis, and even recommendations on ransom demands.
Check out our report for more details: socradar.io/resources/whitep…


Faruk retweeted

🚨 BREAKING: AI-enabled ransomware hackers using Claude left their logs on an open server.
SOCRadar found 8k+ AI messages from INC and The Gentlemen affiliates using Claude and Kimi, plus 46 INC encryptor builds.
To fight refusals, they authorized it by calling it red-teaming.


🚨 New Research | AI-Driven #Ransomware Operations Exposed
We identified an AI-driven intrusion ecosystem associated with INC and The Gentlemen #Ransomware affiliates. The investigation uncovered seven exposed adversary-controlled servers containing AI session histories, operational knowledge bases, credentials, and the source code of #Phantom, an Autonomous Red Team Kill Chain Framework.
Key findings:
- 62 Identified Victims (36 US-based)
-46 customized INC Ransomware encryptor builds
- $23K+ in AI service spending
- AI session logs and operational knowledge bases
- Phantom, Ghost C2, RevSocks, and custom offensive tooling
Blog: socradar.io/blog/inc-gentlem…
Whitepaper: socradar.io/resources/whitep…
#ThreatIntelligence #CTI #ThreatHunting #Malware

Another #UNC6671 #phishing domain:
signin-options[.]com (2026-10-05)
Observed subdomains:
aave.signin-options[.]com
dwt.signin-options[.]com
fennemorelaw.signin-options[.]com
klgates.signin-options[.]com
thompsonhine.signin-options[.]com
bipc.signin-options[.]com
cov.signin-options[.]com
schwab.signin-options[.]com
Same *-options naming pattern


Update on #UNC6671:
New subdomain:
gunder[.]signinsettings[.]com → 46.19.136[.]147
Same IP previously observed hosting myaccountapps[.]com subdomains.


Another #UNC6671 domain: myssosettings[.]com (Registration Date: 2026-10-02)
pillsburylaw[.]myssosettings[.]com
steris[.]myssosettings[.]com
linklaters[.]myssosettings[.]com
iag[.]myssosettings[.]com
medibank[.]myssosettings[.]com
fisherphillips[.]myssosettings[.]com
Worth watching: signinsettings[.]com - Registered on 2026-10-02 via NICENIC, Cloudflare NS
@malwrhunterteam @1ZRR4H @TLP_R3D
Faruk retweeted

SOCRadar Threat Research Unit (STRU) has published new research on #ICMacOS (Icarus macOS), a macOS Malware-as-a-Service that rapidly evolved from an infostealer into a persistent RAT.
Full breakdown 👉 socradar.io/blog/icmacos-inf…

Faruk retweeted
New Okta Vishing Theme: "Contact"
Themes switching: support -> claims -> report -> contact
Hunt for:
- contact-{org}.com
- {org}.contact
Tracked through @ValidinLLC

Potential #UNC6671 #phishing infrastructure impersonating Okta SSO
Root Domains:
- okta-ssolink[.]com
- okta-signinsso[.]com
- okta-linksso[.]com
Targeted Brands:
rainxyz[.]okta-signinsso[.]com
withpersona[.]okta-linksso[.]com
appsflyer[.]okta-ssolink[.]com
All registered on Oct 2 via NICENIC, using Cloudflare NS.


Add 2 more brands:
morganlewis[.]myssoauth[.]com - Legal
fico[.]myssoauth[.]com - Finance
#UNC6671

🚨 UNC6671 INFRASTRUCTURE UPDATE ⚖️
Fresh legal-sector impersonation observed:
🔎 hollandhart.myssoauth[.]com
The hostname appears to spoof US law firm Holland & Hart and continues the cluster’s SSO/authentication theme.
Detection at observation: 0/92 👀
#UNC6671

Faruk retweeted

🚨 UNC6671 INFRASTRUCTURE UPDATE ⚖️
Fresh legal-sector impersonation observed:
🔎 hollandhart.myssoauth[.]com
The hostname appears to spoof US law firm Holland & Hart and continues the cluster’s SSO/authentication theme.
Detection at observation: 0/92 👀
#UNC6671
Faruk retweeted
New STRU Research: NetScaler C2
An autonomous framework designed to identify Citrix devices at scale, fingerprint their versions, exploit CVE-2026-88771 and deploy a lightweight agent.
socradar.io/blog/netscaler-c…

