

🧠 Malware analyst & reverse engineer 🦠 Ransomware, loaders, stealers & RATs 🔬 Reverse engineering • crypto • tooling 📍 Technical research. No buzzwords.
Joined May 2025
- Tweets779
- Following190
- Followers1.2K
- Likes4K



Pinned Tweet
🚨NEW RAT UNCOVERED
I didn’t stop at “this malware has a C2”
💥I rebuilt it
BotC2 RAT: native x64 reverse engineering, custom framing, command dispatcher, persistence, injection, screencast, and a working C2 emulator talking to the real sample.
Research ↓
github.com/ShadowOpCode/BotC…


🚨ALERT🚨
PhantomStealer4 has a #ransomware module.
AES-256-CBC + HMAC-SHA256, .phantom files, FTP key escrow and file deletion.
Disabled in this build (RansomCheckBox = false)
Bazaar👇
bazaar.abuse.ch/sample/13cee…


Just uploaded 203 #RGBLoader samples to MalwareBazaar, all discovered through hunting with my custom #YARA rule! 🔬
The samples are now available to the malware research community under the RGBLoader tag.
🔗 bazaar.abuse.ch/browse/tag/R…
#MalwareAnalysis #ThreatHunting


🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇


🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇
IMPORTANT UPDATE
xitter.cf/ShadowOpCode/status/21…
The loader I’ve been tracking as #RGBLoader is very likely a #GraftLoader variant, documented by @trendaisecurity. Both share the same pixel extraction, crop constants and payload cipher, including implementation quirks.
xitter.cf/ShadowOpCode/status/21…
trendaisecurity.com/en-us/re…
The loader I’ve been tracking as #RGBLoader is very likely a #GraftLoader variant, documented by @trendaisecurity. Both share the same pixel extraction, crop constants and payload cipher, including implementation quirks.
xitter.cf/ShadowOpCode/status/21…
trendaisecurity.com/en-us/re…
🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇
NEW generalized #YARA rule for #RGBLoader
👇
yaraify.abuse.ch/search/yara…
xitter.cf/ShadowOpCode/status/21…
⚠️NOT tested against FP, consider it a beta⚠️

🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇
hxxps://katfiore[.]com (not personally validated as compromised at the moment, just reported)
hxxps://xenseyu[.]com/hex/dr7kggqq4y
hxxps://xenseyu[.]com/p?id=b5b1eb33425d9811d17ff3045684db5a993a9a68&k=0c1507711b004009
cc @shalkie @tobersotski

"french/viet fake program" refers to the language seen in the code, not the threat actor origin or affiliation

hxxps://github[.]com/gpt-6-astra/gpt-6-astra.github.io/releases/tag/Astra
@malwrhunterteam @vxunderground @skocherhan @tobersotski

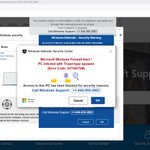
Support #scam
"Your computer has virus"
Starts at full screen with a scary and loud alarm sound
@MsftSecIntel @illegalFawn @JAMESWT_WT @tobersotski
#threatintel #IoC
hxxps://nozazisoda.z11.web.core.windows.net/gx/index.html?phone=%2B1-844-959-2863#
🤡🤡🤡Vulnerable to XSS🤡🤡🤡


🚨 Malvertising / Trading Scam campaign spotted🚨
Promoting a fake trading platform through misleading ads and fake news-style content.
The flow pushes victims to register and deposit a minimum of €250.
hxxps://g-globalapp[.]com
#ThreatIntel #Malvertising #Scam #CyberSecurity


@quesadilla_exe and @x86x64_IA32, since you asked for it.
Honestly, the analysis went much further than I expected.
🚨Another fake Microsoft file-sharing lure spotted in the wild.
The page impersonates a Microsoft shared document flow and asks the victim to enter a "verification code" before authenticating.
IOC: z0bce7yh5[.]flyseem[.]xyz

🚨ALERT🚨
Threat actors are using Adobe Acrobat as lure to install Remote Management Tool #FleetDeck
eml>url (geofenced)>msi>FleetDeck
deploymentID 394813e8-03cd-47fa-a194-92033da9086f
@anyrun_app : app.any.run/tasks/edc72712-e…
Related tweet (2 years ago)
👇
xitter.cf/WhichbufferArda/status…


🚨 Beware! Threat actors are using PDFs to lure victims into installing the FleetDeck RMM tool. These malicious PDFs embed a URL (agent[.]fleetdeck[.]io) behind a button, tricking users to click and download the FleetDeck executable. Once installed, this remote management tool could give attackers control over your device. #CyberSecurity #PhishingAlert
virustotal.com/gui/file/1e17…

🚨ALERT🚨
Italian #smishing campaign targeting road users
Fake speed ticket
Identity and credit card data extortion
hxxps://www.cnl[.]it[.]com/it/home.html
@AgidCert @guelfoweb have a look


