




Pinned Tweet
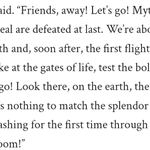
This thought by Tom Kirkwood probably makes a good &hopeful closing message #WhyWeAge2020.Should have tweeted it last.I think I tweeted a summary of what I found striking in all talks you can find them under the hastag #WhyWeAge2020, I have more pictures from the slides just ask!

#WhyWeAge2020 RT: Tom Kirkwood points out that we are not biological programmed for aging¬ programmed to die - it's just that our repair mechanisms don't work well enough to maintain our bodies indefinitely. A very hopeful message!
Hard to believe but apparently true
oliverwyman.de/content/dam/o…
Simon L retweeted

To that I say mathematics is not a science in any conventional sense of the word. Sorry, folks. You can cry about it but history suggests otherwise.


Simon L retweeted

RIP Jeffrey Goldstone, who never received the Nobel Prize for physics he so richly deserved:
share.google/Dy3AwBTpYjMknbR…

Simon L retweeted

Lmao, how are docs going to even pick drugs for UC patients in a few years. Is there a more crowded/competitive indication than IBD?
investors.gilead.com/news/ne…
The news about the treasury limiting pharma china deals I unsuprising only that they left the doors open so long isn't. Defending industrial base of the knowledge economy avoiding capabilities being lost in the West
What were they trying to do?

Still happy with this one so not to fazed by the ups and downs today - think I'll sell tomorrow, doesn't look to attractive to me now hold this until closure
$QIA nice deal we got. In retrospect I could have played it better by adding more as time went by (and risk of no deal down) but pretty happy with the outcome as is (let's see where/what spread to price we open tomorrow)
Simon L retweeted

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.


Here is a website to check if your client still trusts compromised eMudhra certificates
emudhra.we-have-a-problem.co…
Great summary of this day

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Some clever people on here said MRNA has to go done for biotech to recover- come round to the view that they are onto something
Human security system compromised

Internet encryption is currently having a nuclear meltdown.
Cryptographers are calling it "bigger than Heartbleed."
A global Certificate Authority just leaked 8 master private keys that allow anyone to impersonate any server on Earth (Google, banks, government sites).
A normal master key has 116 digits of entropy.
The actual leaked keys?
4. 56. 66. 115.
A toddler on a calculator could have cracked them.
While browsers patched it today, millions of IoT devices, Linux servers, and Docker containers will take years to clean up.
We bet global digital security on centralized human gatekeepers who forgot to check their math.
True security can't rely on trust cartels. It has to be governed by mathematical consensus.
See the signal. ♾️
