

Think Tank - Seguridad y Defensa en el Ciberespacio.
Madrid, España
Joined March 2013
- Tweets7.8K
- Following148
- Followers3.3K
- Likes2.5K



Pinned Tweet
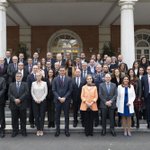
Presentación La Moncloa de los primeros entregables elaborados por el Foro Nacional de #Ciberseguridad del @dsn, con la participación de @Adolfo_Hdez de @THIBER_ESP, y anuncio de la próxima aprobación del Plan Nacional de Ciberseguridad thiber.org/2022/03/15/presen… #foroCiber

Un año más agradecemos a @SicRevista la oportunidad que nos brinda de compartir nuestra visión sobre el panorama #riesgo digital y los retos a los que haremos frente en 2026 en el ámbito de la #ciberseguridad y la #ciberdefensa revistasic.es/

THIBER retweeted

#ICYMI: The NCA’s biggest ever money laundering job - Operation Destabilise is a three-year long investigation into multi-billion dollar Russian money laundering networks with links to ransomware, espionage & UK drugs gangs.
Read the full story ➡️ nationalcrimeagency.gov.uk/n…

ALT Stacks of seized cash

ALT Stacks of seized cash in a suitcase

ALT Stacks of seized cash in a bag

ALT Seized cash
THIBER retweeted

We can confirm that early this year we saw the largest ransomware payment ever at $75M. The "big game hunting" trend we discussed in our 2024 crime report – fewer attacks on larger targets with deeper pockets – is becoming more pronounced. chainalysis.com/blog/ransomw…

THIBER retweeted

#NotaDSN El 13 de junio 2024 se ha celebrado la octava reunión plenaria del Foro Nacional de #Ciberseguridad, presidida por directora @dsn, en la que coordinadores de los cinco grupos de trabajo han presentado el estado de los trabajos en elaboración shorturl.at/6lZZd

International investigation disrupts phishing-as-a-service platform #LabHost via @Europol europol.europa.eu/media-pres…

Law enforcement disrupt world’s biggest ransomware operation | @Europol europol.europa.eu/media-pres…
THIBER retweeted

Some interesting points from the article: Stuxnet costed more than 1 billion USD to build (!). If true, it was brought into Natanz in a "water pump", that later spread it to the network. The guy who did this died in 2009, so very important detail, the Stuxnet variant he brought in 2007 would be a really early one, like Stuxnet 0.5. IMHO, the really impactful variants were the later ones, that were seeded through 5 different organizations in Iran, in 2009 and 2010.

Stuxnet mystery revealed years later. Huge if true. nltimes.nl/2024/01/08/dutch-…

THIBER retweeted
#DestacadoDSN #PublicaciónDSN «#Drones y Seguridad Nacional - Un estudio multidimensional 2023» shorturl.at/iqvW0

Detenido el líder del grupo de ciberdelincuencia ‘Kelvin Security’ tras 300 ataques internacionales
cybersecuritynews.es/detenid…
International Counter #Ransomware Initiative 2023 Joint Statement whitehouse.gov/briefing-room… a través de @whitehouse
Microsoft exposed 38TB of private AI data, including passwords and secret keys thestack.technology/microsof…

THIBER retweeted

Today Lockbit ransomware group issued a poll to all of their affiliates.
Lockbit is considering implementing new rules for Lockbit affiliates due to their frustration with ransomware negotiators. Currently, Lockbit ransomware group has no rules in place for how much (or how little) affiliates can ransom a company for. They are considering "regulating" ransom demands.
They state newer affiliates are giving large discounts to victim companies out of desperation for money, whereas more experienced affiliates do not cave to negotiator's proposed payment from the victims.
Lockbit administrative staff are proposing the following options.
1. No changes in payment policy, payment options will remain "unregulated" and remain up to the affiliates.
2. New rules in place which set the minimum payment allowed to be 3% of the victim companies annual revenue with the option of a 50% discount, bringing it down to 1.5% of annual revenue.
3. Establish a new rule where affiliates can only grant a 50% discount of the original ransom price.
4. Establish a new rule where they will not accept a payment below the victims maximum ransomware insurance policy.
5. Establish a new rule where they will accept a minimum payment of 50% of the victims ransomware insurance policy.
In regards to this poll, National Hazard Agency, a subdivision of Lockbit ransomware group, has stated they will no longer accept payments below 3% of the companies annual revenue. They will immediately retaliate against any negotiator who approaches them with an offer of less than 3% of the companies revenue. The retaliation will be complete destruction of company data.
Image 1. Original Lockbit poll (Russian)
Image 2. Lockbit poll (English)
Image 3. Message from National Hazard Agency


THIBER retweeted
#LibroDesinfoSN #DestacadoDSN #PublicaciónDSN @aprensamadrid @fape_fape #VideoDSN ↔️ <Tipos de mala información y #desinformación> PDF➡️ bit.ly/3LNUmxr

#LibroDesinfoSN «Lucha contra las campañas de #desinformación en ámbito de #SeguridadNacional: propuestas de la sociedad civil» #PublicaciónDSN bit.ly/3fptJCL @aprensamadrid @fape_fape #DestacadoDSN Descarga PDF ➡️ bit.ly/3LNUmxr
For the first time, U.S. government lets hackers break into satellite in space politi.co/3YuBFp0 a través de @politico

THIBER retweeted
#ConoceDSN Riesgos y Amenazas a la Seguridad Nacional🇪🇸 #ESN2021 #SeguridadNacionalSomosTodos #PICSN bit.ly/3sIT2V7

New acoustic attack steals data from keystrokes with 95% accuracy bleepingcomputer.com/news/se… #CyberSecurity
#Hackers Compromised the Russian Defense Satellite Communications Provider gbhackers.com/russian-satell… a
THIBER retweeted
We can confirm that Russian satellite operator Dozor Teleport (AS41942) left the global routing table at about 02:00 UTC earlier today. It is now unreachable, reportedly due to a cyber attack.
4 of 5 routes previously announced by AS41942 were withdrawn, one is now announced by Amtel-Svyaz (AS51764), parent company of Dozor Teleport.


PMC Wagner has announced that they have taken down the satellite provider Dozor-Teleport and damaged user terminals. Their rivalry with the RU MoD is manifesting in an unusual way. This is the second major satellite provider breach after Viasat t.me/RichardWgn
